MeshCentral on AlmaLinux 9
(Self-Hosted Remote Management + Node.js + Nginx + SSL)
MeshCentral is a powerful, open-source remote management and remote access platform that allows administrators to securely control, monitor, and manage computers and servers through a web browser. It supports remote desktop, terminal access, file transfer, device grouping, user and role management, and optional out-of-band management, all without relying on third-party cloud services.
Unlike proprietary tools such as TeamViewer or AnyDesk, MeshCentral can be fully self-hosted, giving you complete ownership of devices, credentials, and connection data. This makes it an excellent choice for system administrators, MSPs, DevOps teams, and privacy-focused organizations.
Running MeshCentral on AlmaLinux 9, a RHEL-compatible, enterprise-grade Linux distribution, provides long-term stability, predictable updates, and strong security defaults. AlmaLinux 9, combined with Node.js LTS, Nginx, and HTTPS (SSL), offers a production-ready foundation for a secure and scalable remote management server.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | AlmaLinux 9 | Enterprise-grade, RHEL-compatible Linux base |
| Runtime | Node.js LTS (18 / 20) | Runs the MeshCentral server |
| Application | MeshCentral | Web UI, device management, relay services |
| Database | Built-in (NeDB / SQLite) | Stores users, devices, and settings |
| Reverse Proxy | Nginx (recommended) | HTTPS termination and routing |
| TLS | Let’s Encrypt / PKI | Encrypted secure connections |
| Clients | Browsers + Mesh Agents | Remote access and device control |
MeshCentral uses a single-service, lightweight architecture, which makes it easy to deploy, maintain, and scale.
Why Use MeshCentral?
- Fully self-hosted — no vendor lock-in
- Remote desktop & terminal — browser-based access
- Agent-based management — Windows, Linux, macOS
- Granular permissions — users, groups, roles
- WebSocket-based connections — fast and efficient
- File transfer & power controls
- Multi-tenant capable — suitable for MSPs
- Open-source & actively maintained
- Very low resource usage
MeshCentral is designed for secure, scalable remote administration with full infrastructure control.
MeshCentral vs Other Remote Management Tools
| Feature / Capability | MeshCentral | TeamViewer | AnyDesk | Apache Guacamole |
|---|---|---|---|---|
| Hosting | Self-hosted | Cloud only | Cloud only | Self-hosted |
| Open-source | ✅ Yes | ❌ No | ❌ No | ✅ Yes |
| Data ownership | Full control | Vendor-controlled | Vendor-controlled | Full control |
| Agent-based | ✅ Yes | ✅ Yes | ✅ Yes | ❌ No |
| Web UI | ✅ Yes | ❌ No | ❌ No | ✅ Yes |
| Cost | Free | Paid | Paid | Free |
MeshCentral stands out for privacy, transparency, and flexibility.
Security & Best Practices on AlmaLinux 9
- Always run MeshCentral over HTTPS.
- Use Let’s Encrypt SSL certificates with automatic renewal.
- Bind MeshCentral to 127.0.0.1 and expose it via Nginx.
- Store secrets only in configuration files or environment variables.
- Disable public account creation if not required.
- Enforce strong passwords and role-based access.
- Enable SELinux (enforcing mode) and label Docker/Node paths correctly.
- Configure firewalld and allow only ports 80 / 443.
- Keep AlmaLinux, Node.js, and MeshCentral updated.
- Regularly back up:
- MeshCentral data directory
- Configuration files
- Monitor logs for authentication and device activity.
Typical Use Cases
- Remote server administration
- IT support and helpdesk operations
- MSPs managing multiple clients
- Home labs and self-hosted environments
- Device inventory and monitoring
- Secure alternative to TeamViewer or AnyDesk
- Enterprise or compliance-sensitive environments
Deploying MeshCentral on AlmaLinux 9 gives you a secure, scalable, and fully self-hosted remote management solution — combining modern Node.js performance with enterprise-grade Linux stability, strong encryption, and full control over your infrastructure.
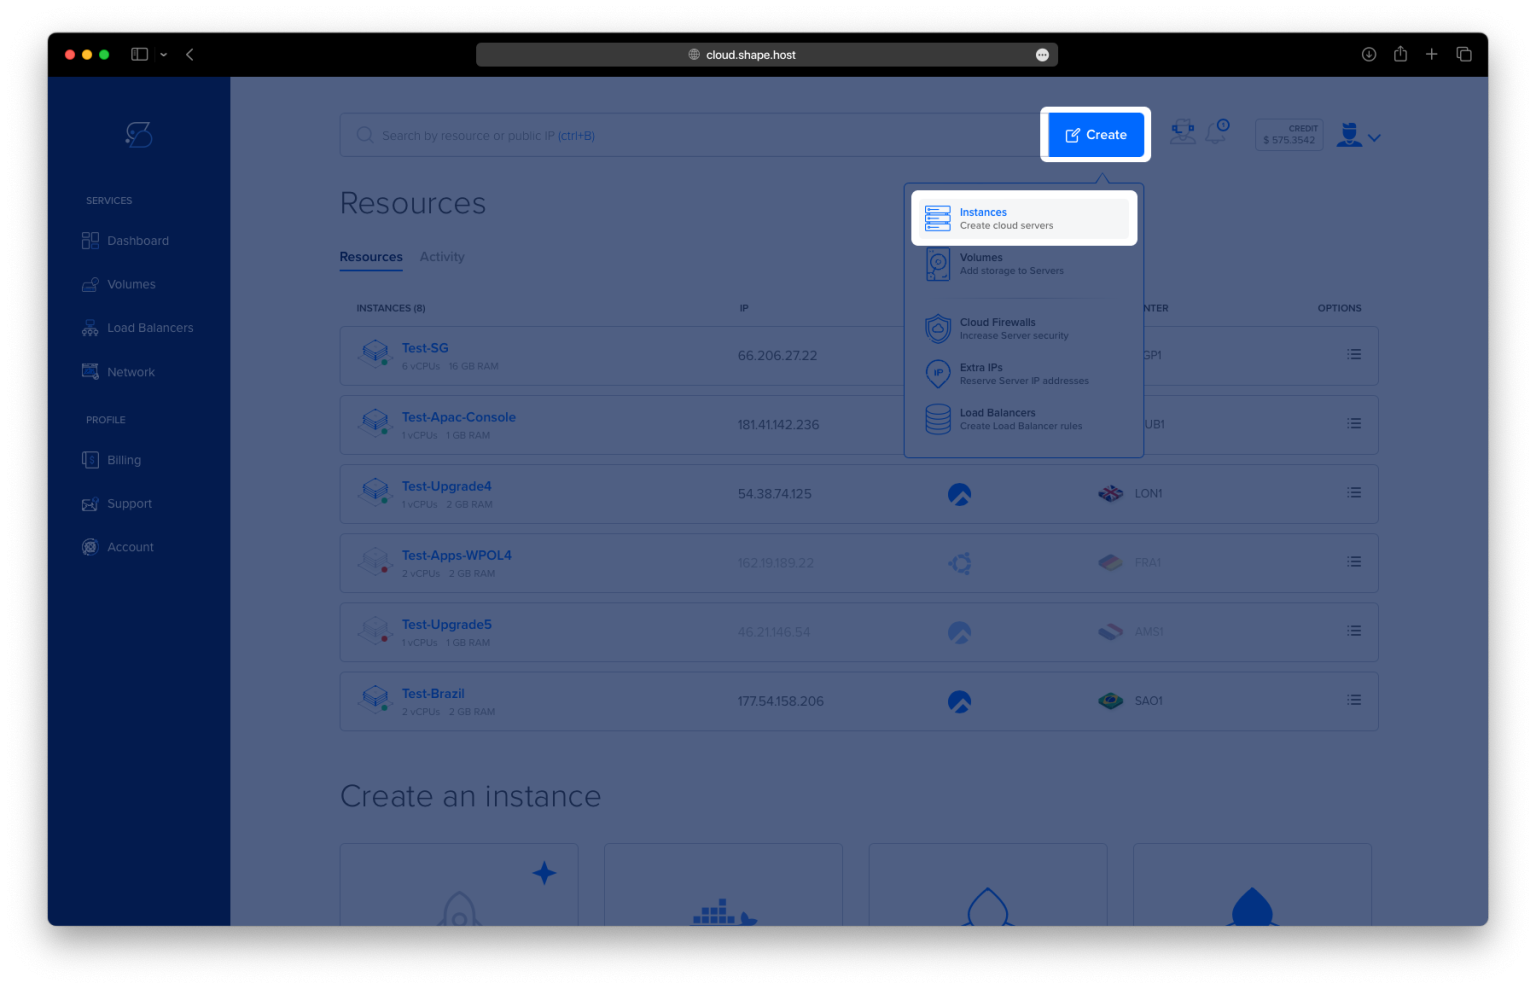
Step 1: Create a Server Instance on Shape.Host
Before installing MeshCentral, you need a VPS with a public IP address.
Log in to https://shape.host
Click Create → Instance

Choose a data center close to your users

Select a plan with at least:
2 CPU cores
4 GB RAM
30–40 GB SSD
Choose AlmaLinux 9 (64-bit) as the operating system

Create the instance and wait for provisioning

Copy the public IP address

Step 2: Connect to the Server (Linux, macOS & Windows)
Linux / macOS
ssh root@YOUR_SERVER_IP
Windows (PowerShell / Windows Terminal)
ssh root@YOUR_SERVER_IP
Windows (PuTTY)
- Host Name:
YOUR_SERVER_IP - Port:
22 - Connection Type: SSH
- Username:
root
Step 3: Update the System
dnf update
This command:
- Updates all installed packages
- Applies security patches
- Prepares the system for Node.js and MeshCentral installation

Step 4: Install Required Dependencies
dnf install curl ca-certificates gnupg
These packages are required to:
- Securely download external scripts (
curl) - Validate HTTPS connections (
ca-certificates) - Verify repository signatures (
gnupg)

Step 5: Install Node.js 20 (Required by MeshCentral)
MeshCentral requires a modern Node.js runtime.
curl -fsSL https://rpm.nodesource.com/setup_20.x | bash -

- Adds the official NodeSource repository for Node.js 20
dnf install nodejs

Verify installation:
node -v
npm -v

Step 6: Install MeshCentral
Create the application directory:
mkdir -p /opt/meshcentral
cd /opt/meshcentral
Install MeshCentral using npm:
npm install meshcentral

Create the data directory:
mkdir -p /opt/meshcentral/meshcentral-data
This directory will store:
- Configuration files
- SSL certificates
- Runtime data and logs
Step 7: Initial MeshCentral Configuration
Create the configuration file:
nano /opt/meshcentral/meshcentral-data/config.json
Initial configuration:
{
  "settings": {
    "cert": "almalinux-tutorials.shape.host",
    "port": 443,
    "redirPort": 80,
    "selfUpdate": false
  },
  "domains": {
    "": {
      "title": "MeshCentral",
      "newAccounts": true
    }
  }
}
What this configuration does
- Sets the domain MeshCentral will use
- Runs MeshCentral on HTTPS (443) and redirects HTTP (80)
- Disables automatic updates (recommended for stability)
- Allows creation of the first administrator account

Test-run MeshCentral manually:
node /opt/meshcentral/node_modules/meshcentral
- Confirms MeshCentral starts correctly
- Stop it with Ctrl + C after verification

Step 8: Create a systemd Service
Create the systemd service file:
nano /etc/systemd/system/meshcentral.service
Paste the following:
[Unit]
Description=MeshCentral Server
After=network.target

[Service]
Type=simple
ExecStart=/usr/bin/node /opt/meshcentral/node_modules/meshcentral
WorkingDirectory=/opt/meshcentral
Restart=always
RestartSec=10
Environment=NODE_ENV=production

[Install]
WantedBy=multi-user.target

Reload systemd configuration:
systemctl daemon-reload
Enable and start MeshCentral:
systemctl enable meshcentral
systemctl start meshcentral
Check service status:
systemctl status meshcentral

Step 9: Enable Let’s Encrypt SSL
Edit the configuration file again:
nano /opt/meshcentral/meshcentral-data/config.json
Final production configuration:
{
  "settings": {
    "cert": "almalinux-tutorials.shape.host",
    "port": 443,
    "redirPort": 80,
    "selfUpdate": false,
    "letsencrypt": {
      "email": "contact@shape.host",
      "names": "almalinux-tutorials.shape.host",
      "production": true
    }
  },
  "domains": {
    "": {
      "title": "MeshCentral",
      "newAccounts": false
    }
  }
}
What changed
- Enables automatic Let’s Encrypt SSL
- Issues a trusted HTTPS certificate
- Disables public account creation (recommended for security)

Restart MeshCentral to apply changes:
systemctl restart meshcentral

Step 10: Access MeshCentral
Open your browser:
https://almalinux-tutorials.shape.host
You now have:
- A fully self-hosted MeshCentral server
- Running on AlmaLinux 9
- Secured with Let’s Encrypt HTTPS
- Managed as a systemd service


You installed MeshCentral on AlmaLinux 9, configured it to run persistently as a system service, and secured it with Let’s Encrypt SSL. This setup provides a robust, centralized, and secure platform for remote management of systems and devices.
For production-grade hosting with full root access, high performance, and long-term stability, Shape.Host Linux SSD VPS is an excellent foundation for running platforms like MeshCentral.