Jitsi Meet on Rocky Linux 9
(Self-Hosted Video Conferencing + Nginx + SSL)
Jitsi Meet is a powerful, open-source video conferencing platform that allows secure audio and video meetings directly in the browser, without requiring user accounts, plugins, or proprietary software. It supports HD video, screen sharing, chat, meeting moderation, recording/streaming, and optional end-to-end encryption (E2EE), making it a strong alternative to Zoom, Google Meet, or Microsoft Teams.
Unlike cloud-only conferencing solutions, Jitsi Meet can be fully self-hosted, giving you complete control over meeting data, media traffic, and access rules. This makes it especially suitable for organizations that value privacy, compliance, and infrastructure ownership.
Running Jitsi Meet on Rocky Linux 9, a RHEL-compatible, enterprise-grade Linux distribution, provides long-term stability, predictable updates, and strong security defaults. When combined with Nginx and HTTPS (SSL), Rocky Linux 9 offers a production-grade foundation for secure, scalable, self-hosted video conferencing.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | Rocky Linux 9 | Enterprise-grade, RHEL-compatible Linux base |
| Web Server | Nginx | HTTPS termination and web access |
| Web App | Jitsi Meet | Browser-based meeting interface |
| Media Server | Jitsi Videobridge | Handles audio/video streams |
| Signaling | Prosody + Jicofo | Authentication, signaling, room control |
| Transport | UDP / TCP | Real-time media transport (WebRTC) |
| TLS | Let’s Encrypt / PKI | Encrypted connections |
Jitsi’s modular architecture allows it to scale from small private meetings to large multi-participant conferences.
Why Use Jitsi Meet?
- Open-source & self-hosted — no vendor lock-in
- No user accounts required — join meetings via simple links
- High-quality audio & video — WebRTC-based
- Screen sharing & chat — built-in collaboration tools
- Meeting moderation — lobby, passwords, participant controls
- End-to-end encryption (E2EE) — optional enhanced privacy
- Browser-based — works on all modern browsers
- Scalable architecture — suitable for teams and organizations
Jitsi Meet is ideal for users who want private, secure video conferencing without SaaS dependencies.
Jitsi Meet vs Other Video Conferencing Platforms
| Feature / Capability | Jitsi Meet | Zoom | Google Meet | Microsoft Teams |
|---|---|---|---|---|
| Hosting | Self-hosted | Cloud only | Cloud only | Cloud only |
| Open-source | ✅ Yes | ❌ No | ❌ No | ❌ No |
| Data ownership | Full control | Vendor-controlled | Vendor-controlled | Vendor-controlled |
| Accounts required | ❌ No | ✅ Yes | ✅ Yes | ✅ Yes |
| E2EE | ✅ Yes | Partial | Partial | Partial |
| Cost | Free (self-hosted) | Free / Paid | Free | Paid |
Jitsi stands out for privacy, flexibility, and full infrastructure control.
Security & Best Practices on Rocky Linux 9
- Serve Jitsi only over HTTPS.
- Use Let’s Encrypt SSL certificates with automatic renewal.
- Open required ports:
- 443/TCP — HTTPS
- 10000/UDP — media traffic
- Optional fallbacks: 4443/TCP, 5349/TCP
- Configure firewalld to restrict unused ports.
- Enable room moderation (passwords, lobby).
- Keep Rocky Linux and Jitsi packages updated regularly.
- Monitor CPU, RAM, disk, and network bandwidth usage.
- Use a dedicated domain or subdomain (e.g.
meet.example.com). - Tune Nginx and Videobridge settings for performance.
- For large deployments, consider multiple Jitsi Videobridge nodes.
Typical Use Cases
- Team meetings and daily stand-ups
- Private business calls
- Remote education and training
- Internal company conferencing
- Privacy-focused organizations
- Self-hosted alternatives to Zoom or Google Meet
- Government, NGO, or compliance-sensitive environments
Deploying Jitsi Meet on Rocky Linux 9 gives you a secure, scalable, and fully self-hosted video conferencing solution — combining modern WebRTC technology with full data ownership, strong encryption, and enterprise-grade Linux stability.
Step 1: Create a Server Instance on Shape.Host
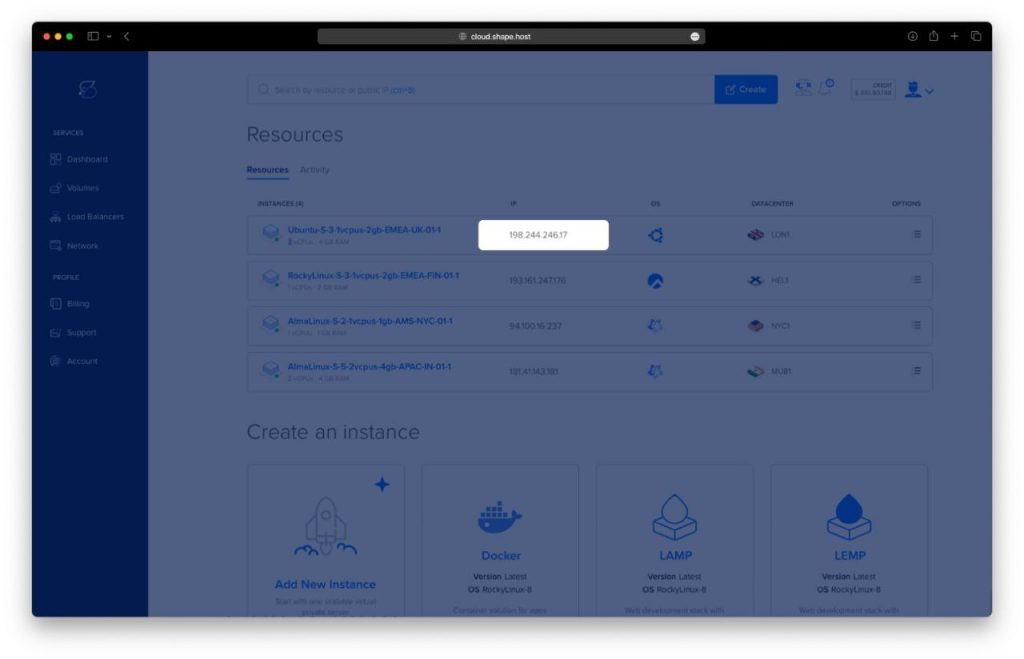
Before installing Jitsi, you need a VPS with a public IP address.
Log in to https://shape.host
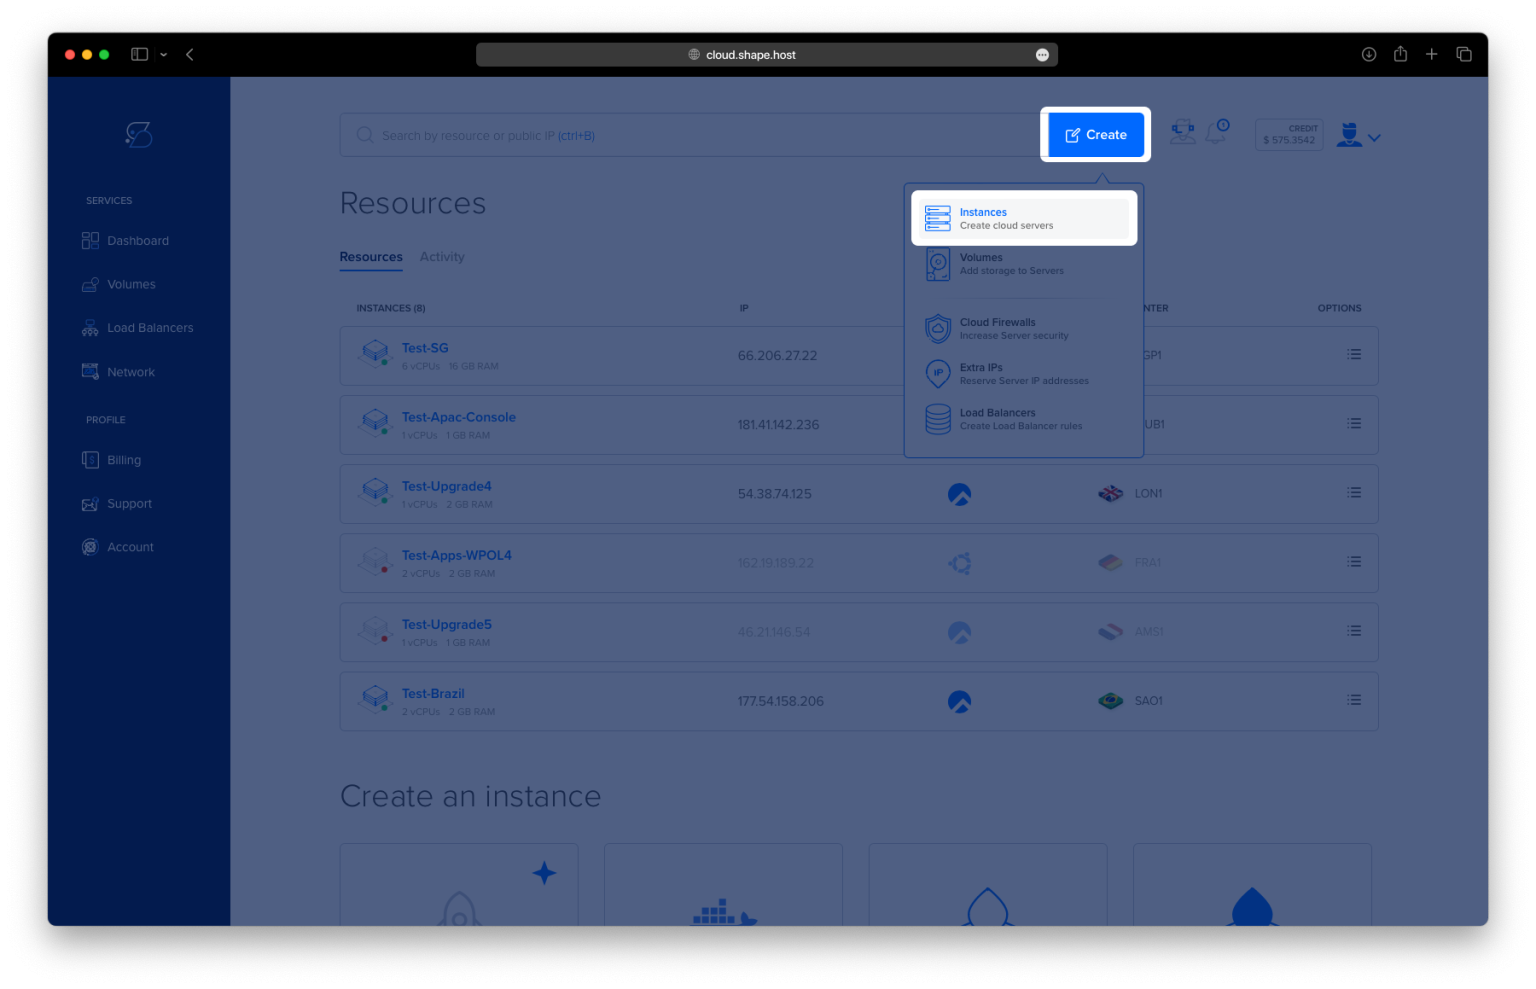
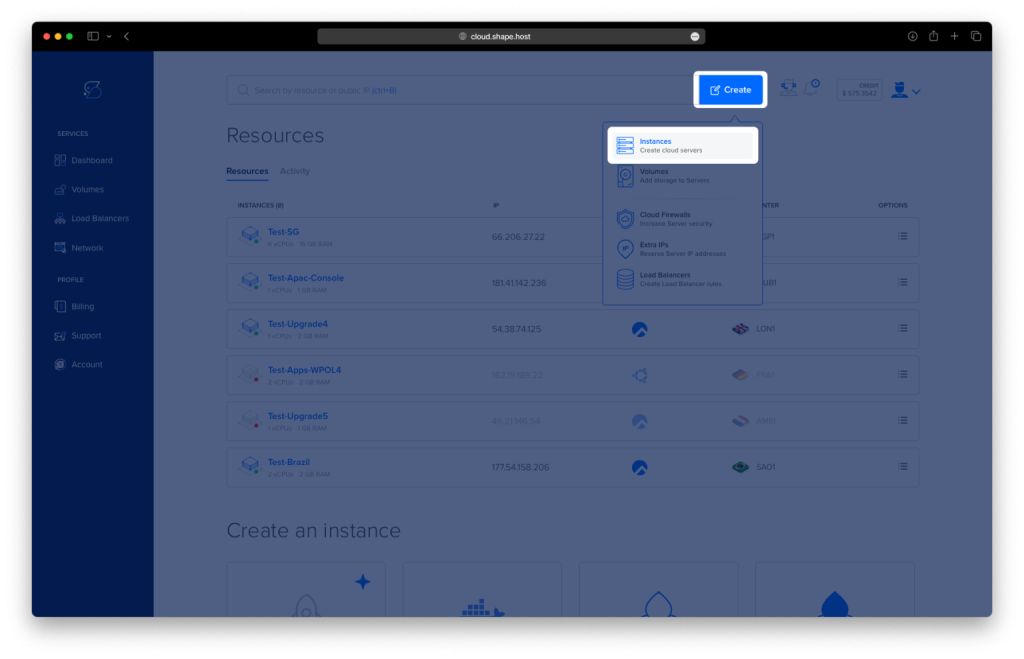
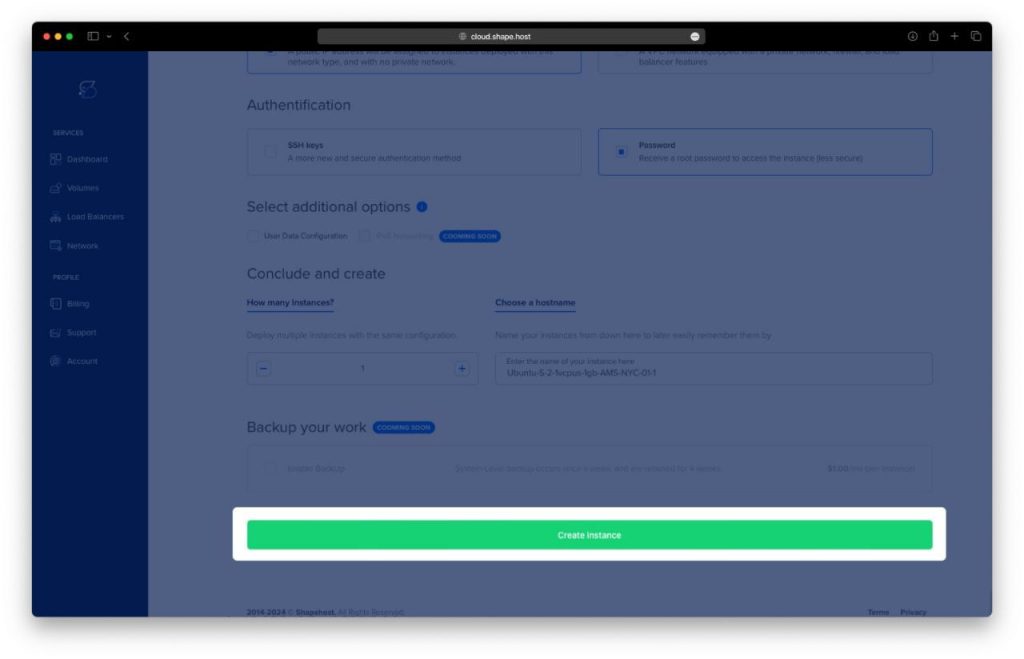
Click Create → Instance
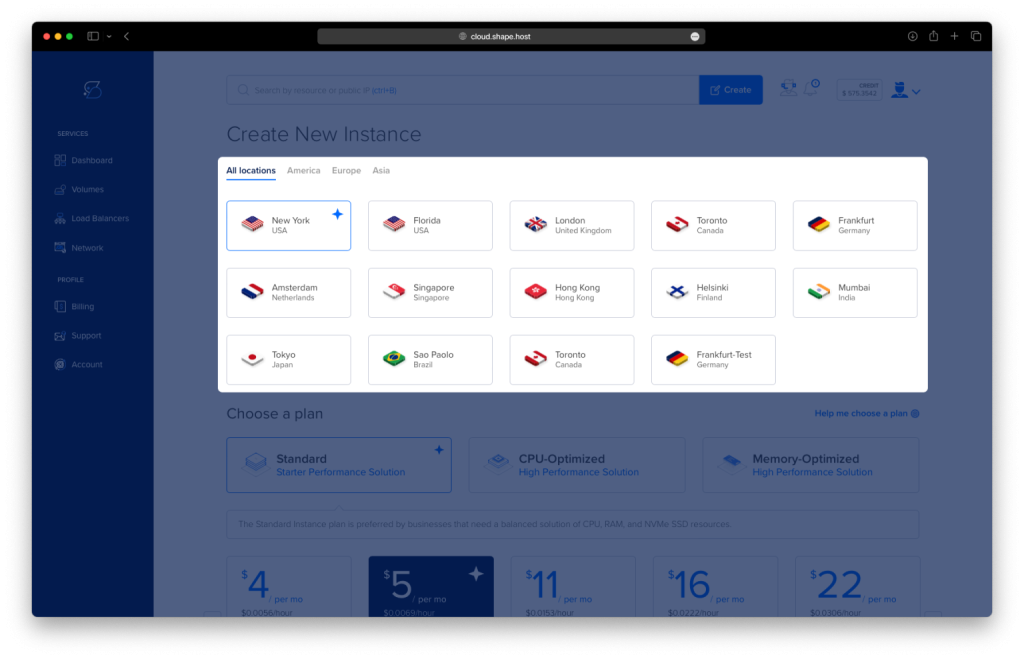
Choose a data center close to your users
Select a plan with at least:
2 CPU cores (4 recommended)
4 GB RAM
40 GB SSD storage
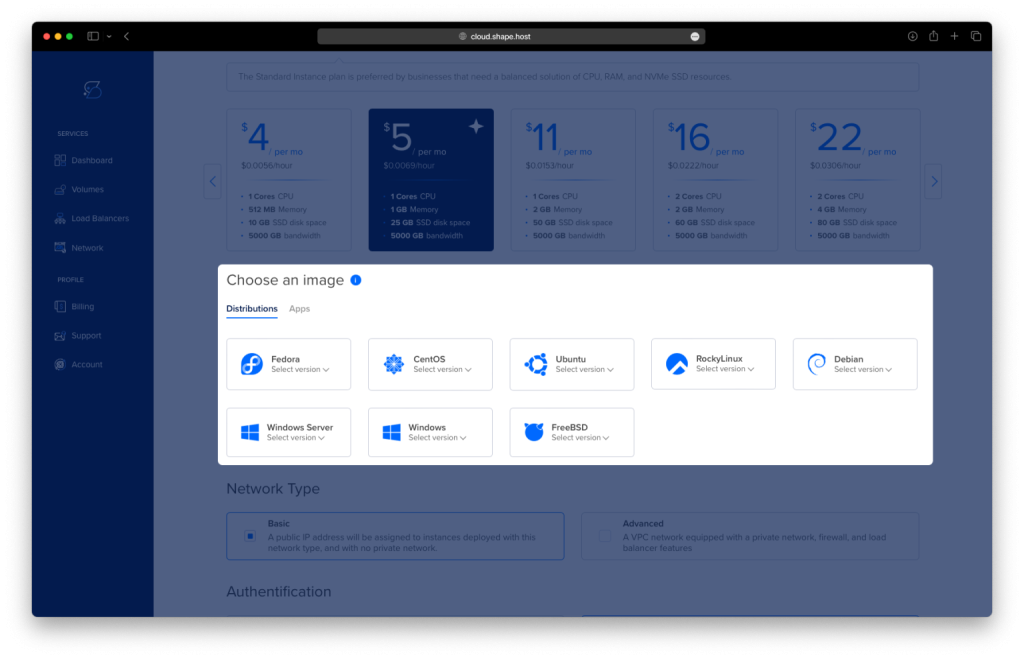
Choose Rocky Linux 9 (64-bit)
Create the instance and wait for provisioning
Copy the public IP address
Step 2: Connect to the Server
Linux / macOS
ssh root@YOUR_SERVER_IP
Windows (PowerShell / Windows Terminal)
ssh root@YOUR_SERVER_IP
Windows (PuTTY)
- Host Name:
YOUR_SERVER_IP - Port:
22 - Connection type:
SSH - Username:
root
Step 3: Update the System
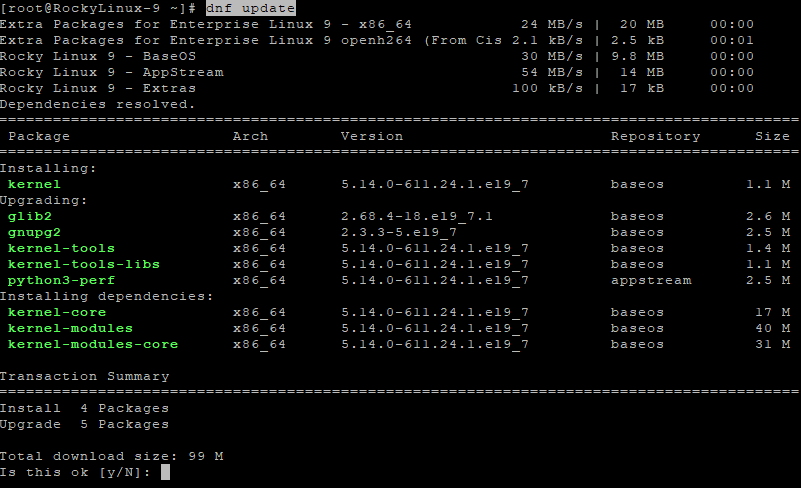
dnf update
- Updates all installed packages
- Applies security patches
- Ensures compatibility with Docker and firewall components
Step 4: Set Hostname (Required by Jitsi)
Jitsi requires a valid fully qualified domain name (FQDN).
hostnamectl set-hostname rockylinux-tutorials.shape.host
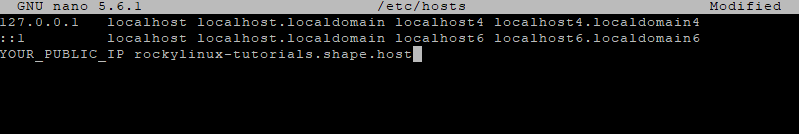
Edit the hosts file:
nano /etc/hosts
Add or update:
127.0.0.1       localhost
YOUR_PUBLIC_IP  meet.example.com
Verify hostname:
hostname
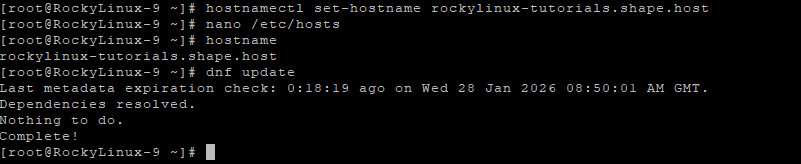
Update again and reboot:
dnf update
reboot
Reconnect via SSH after reboot.
Step 5: Disable SELinux (Required for Docker-Jitsi)
Docker-Jitsi-Meet does not function correctly with SELinux enforcing.
Edit SELinux configuration:
nano /etc/selinux/config
Set:
SELINUX=disabled
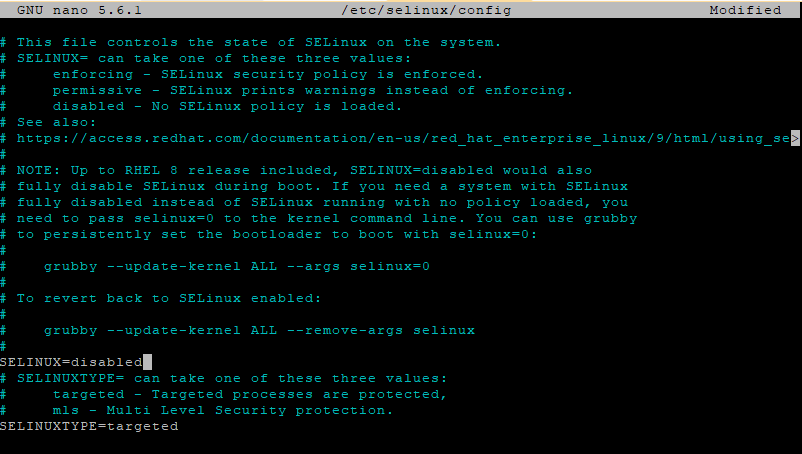
Disable SELinux immediately:
setenforce 0
Reboot to apply permanently:
reboot
Verify SELinux status:
getenforce
Expected output:
Disabled

Step 6: Clean Repositories and Prepare System
Remove any leftover Jitsi repository:
rm -f /etc/yum.repos.d/jitsi.repo
Clean and rebuild cache:
dnf clean all
dnf makecache
dnf repolist
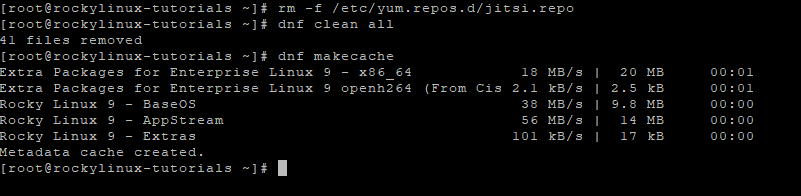
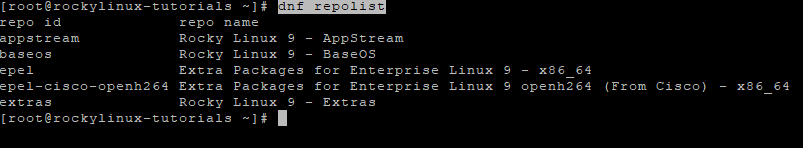
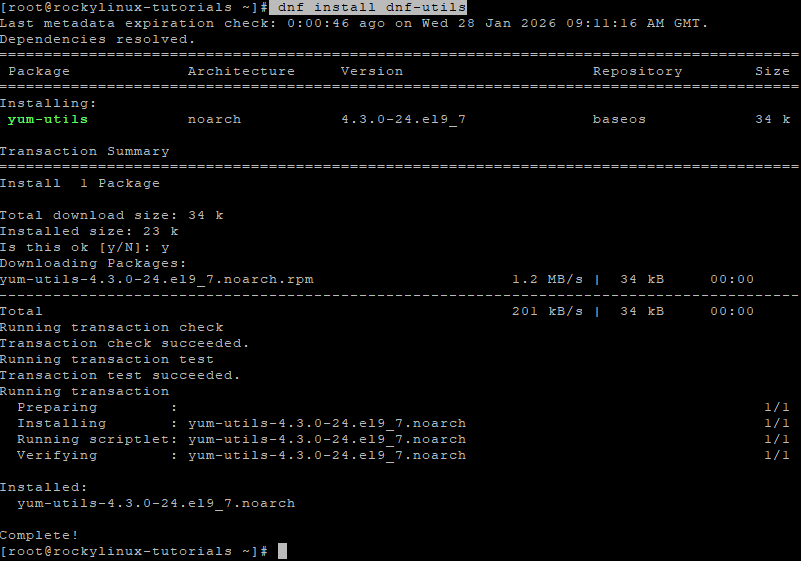
Install repository management tools:
dnf install dnf-utils
Step 7: Install Docker and Docker Compose
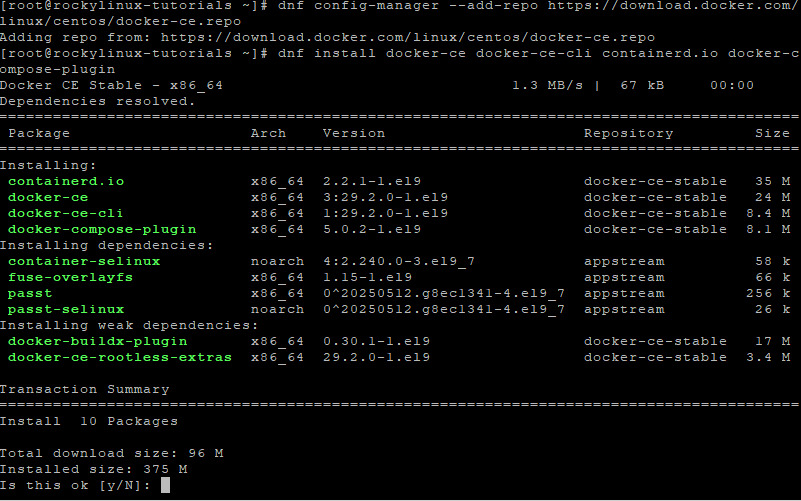
Add Docker repository:
dnf config-manager --add-repo https://download.docker.com/linux/centos/docker-ce.repo
Install Docker components:
dnf install docker-ce docker-ce-cli containerd.io docker-compose-plugin
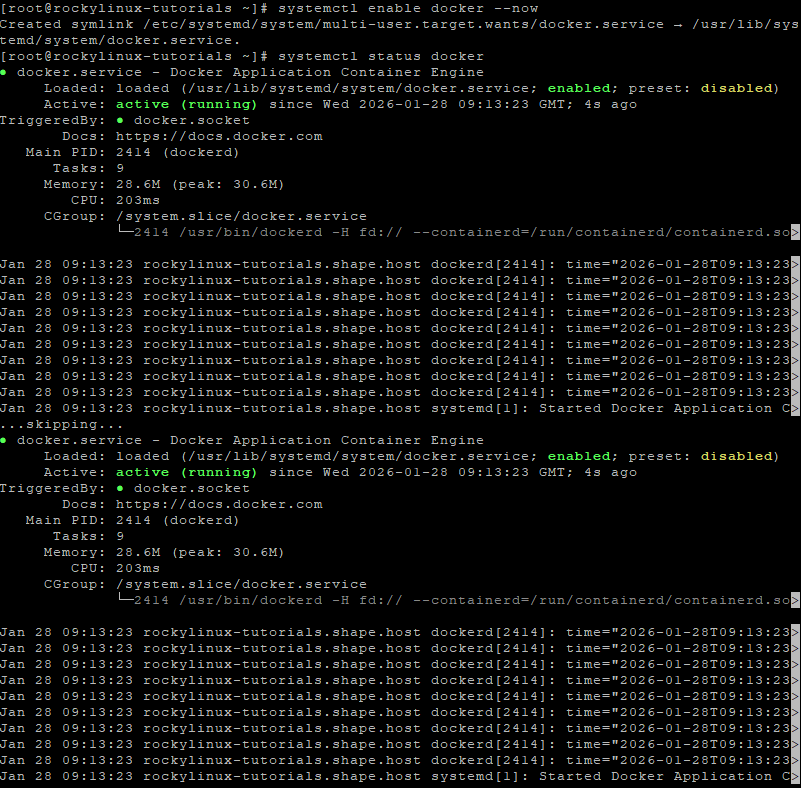
Enable and start Docker:
systemctl enable docker --now
Verify Docker status:
systemctl status docker
Step 8: Configure Firewall (Firewalld)
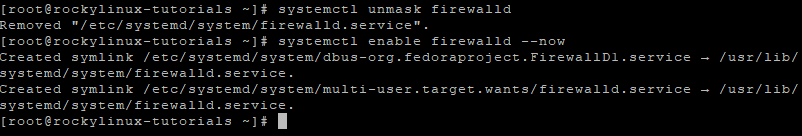
Enable firewalld:
systemctl unmask firewalld
systemctl enable firewalld --now
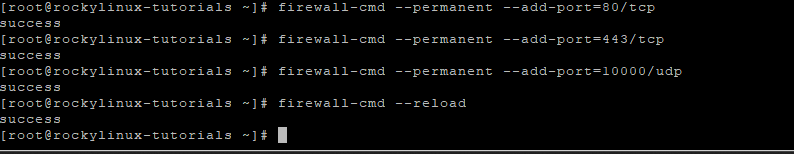
Open required Jitsi ports:
firewall-cmd --permanent --add-port=80/tcp
firewall-cmd --permanent --add-port=443/tcp
firewall-cmd --permanent --add-port=10000/udp
Apply rules:
firewall-cmd --reload
Verify:
firewall-cmd --list-ports

Step 9: Download Docker-Jitsi-Meet
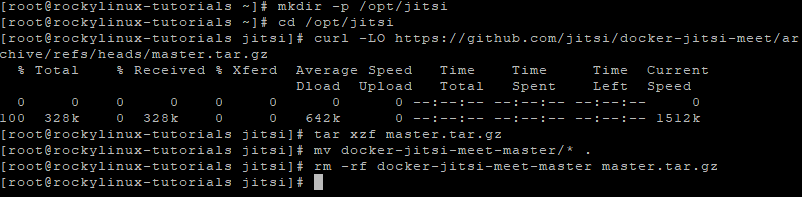
Create working directory:
mkdir -p /opt/jitsi
cd /opt/jitsi
Download project:
curl -LO https://github.com/jitsi/docker-jitsi-meet/archive/refs/heads/master.tar.gz
Extract and clean:
tar xzf master.tar.gz
mv docker-jitsi-meet-master/* .
rm -rf docker-jitsi-meet-master master.tar.gz
Step 10: Configure Jitsi Environment
Copy example environment file:
cp env.example .env
Generate strong internal passwords:
./gen-passwords.sh
Edit configuration:
nano .env
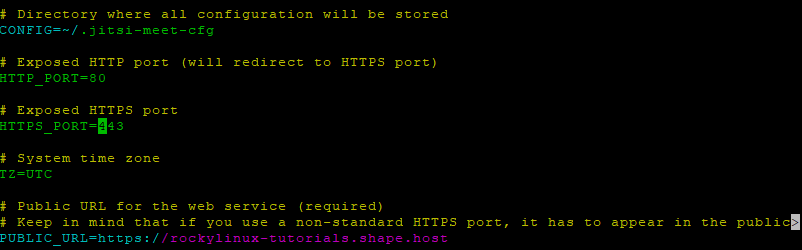
Set the following values:
# Public URL
PUBLIC_URL=https://meet.example.com

# Force correct ports
HTTP_PORT=80
HTTPS_PORT=443

# Timezone
TZ=Europe/Bucharest

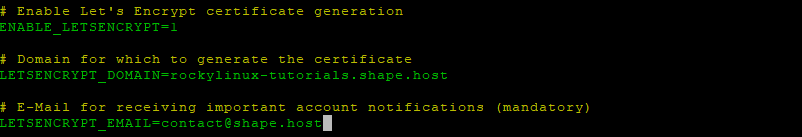
# Enable Let's Encrypt
ENABLE_LETSENCRYPT=1
LETSENCRYPT_DOMAIN=meet.example.com
LETSENCRYPT_EMAIL=admin@example.com
What this configuration does
- Enables automatic Let’s Encrypt SSL
- Defines your public Jitsi domain
- Forces correct HTTP/HTTPS ports
- Sets system timezone for logs and containers
Step 11: Start Jitsi Meet
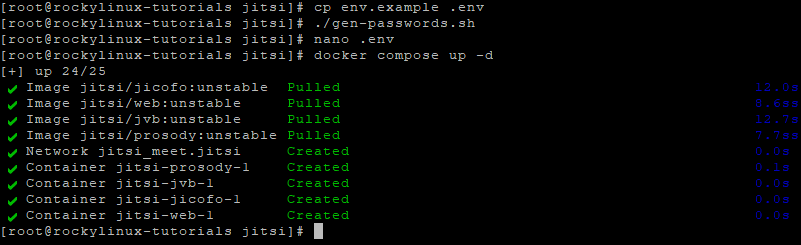
docker compose up -d
This command:
- Pulls all required Jitsi containers
- Automatically requests SSL certificates
- Starts Prosody, Jicofo, Videobridge, Web, and Let’s Encrypt services
View logs (optional):
docker compose logs -f
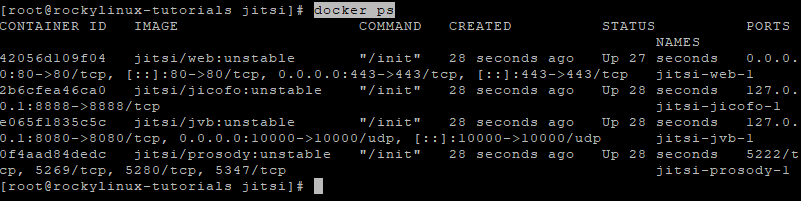
Verify running containers:
docker ps
Step 12: Access Jitsi Meet
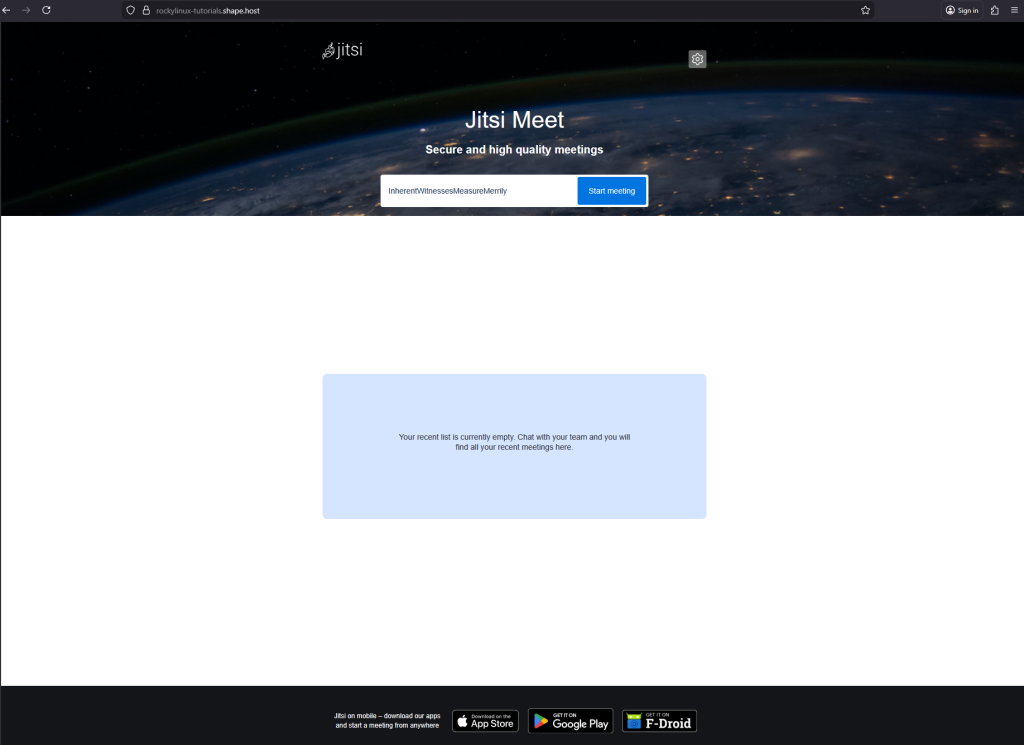
Open your browser:
https://meet.example.com
Your Jitsi Meet instance is now:
- Fully self-hosted
- Running on Rocky Linux 9
- Secured with Let’s Encrypt SSL
- Ready for production video conferencing
You installed Jitsi Meet on Rocky Linux 9 using Docker-Jitsi-Meet, configured hostname, SELinux, firewall rules, and enabled automatic HTTPS with Let’s Encrypt. This Docker-based setup is stable, scalable, and easy to maintain, making it ideal for production use.
For reliable performance, full root access, and scalable infrastructure, Shape.Host Cloud VPS is an excellent choice for hosting real-time communication platforms like Jitsi Meet.