n8n on Ubuntu 24.04 (Docker Compose + Nginx + SSL)
n8n is an open-source workflow automation platform that allows you to connect APIs, databases, and applications with a powerful no-code / low-code interface. Similar to tools like Zapier or Make (Integromat), n8n gives you full control to automate repetitive tasks, integrate cloud services, or orchestrate complex backend processes — all within a self-hosted, privacy-respecting environment.
Running n8n on Ubuntu 24.04 LTS (Noble Numbat) ensures a secure, stable, and modern foundation for automation workflows. Ubuntu 24.04 provides systemd 255, OpenSSL 3, and up-to-date Docker Engine packages, making it ideal for deploying n8n with Docker Compose, Nginx reverse proxy, and SSL encryption.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | Ubuntu 24.04 LTS | Stable, long-term supported Linux base for production use |
| Runtime | Docker Engine + Compose | Manages n8n and related service containers |
| Database | PostgreSQL / SQLite | Stores workflow configurations, executions, and user data |
| Application | n8n Server (Node.js) | Core workflow engine and web interface |
| Reverse Proxy | Nginx | Handles HTTPS termination, routing, compression, and caching |
| TLS | Let’s Encrypt / PKI | Provides secure HTTPS for the n8n dashboard and webhooks |
Why Use n8n?
- Open-source Zapier alternative – build and host your own automation platform.
- Over 400 integrations – connect APIs, databases, cloud services, and custom webhooks.
- Visual workflow builder – drag-and-drop interface for creating complex automations.
- Self-hosted – retain full control over data and credentials.
- Extendable – write custom nodes and logic in JavaScript or TypeScript.
- Webhooks and triggers – integrate real-time events from other systems.
n8n vs Other Automation Tools
| Feature/Capability | n8n (Self-hosted) | Zapier (Cloud) | Make (Cloud) | Node-RED (Self-hosted) |
|---|---|---|---|---|
| Hosting | Self-hosted | SaaS only | SaaS only | Self-hosted |
| Cost | Free (open-source) | Subscription | Subscription | Free (open-source) |
| Integrations | 400+ | 5000+ | 1500+ | 100+ |
| Extensibility | High (custom code) | Limited | Limited | High (custom JS) |
| Privacy | Full data control | Cloud only | Cloud only | Local only |
| Target users | Developers / DevOps | Non-technical | SMBs | Developers |
n8n is the perfect choice for teams that need automation freedom, data ownership, and full customization — without paying for proprietary cloud tools.
Security & Best Practices
- Deploy n8n behind Nginx with HTTPS (using Let’s Encrypt).
- Store environment variables (like credentials, webhook URLs, and JWT secrets) securely in
.env. - Use strong authentication and enable basic auth or reverse proxy protection.
- Keep Ubuntu, Docker, and n8n images regularly updated.
- Restrict webhook ports and firewall all unnecessary traffic (allow only 80/443).
- Regularly back up PostgreSQL or SQLite data and encryption keys.
- Avoid running as root inside containers unless required.
- Automate SSL renewal with Certbot or Traefik’s ACME integration.
Typical Use Cases
- Automating business workflows (e.g., syncing CRM, Slack, and Google Sheets).
- API orchestration and backend logic automation.
- Webhook automation – responding to real-time events.
- Data processing pipelines – transform, store, and forward data between services.
- DevOps automation – deploy CI/CD tasks, monitoring alerts, and cloud integrations.
- Marketing automation – manage email lists, campaigns, and social media APIs.
Deploying n8n on Ubuntu 24.04 with Docker Compose and Nginx gives you a secure, scalable, and fully self-hosted automation platform — offering the flexibility of open-source with the power of enterprise-grade workflow orchestration.
Step 1: Create a Shape.Host Instance
Go to Shape.Host and log in.
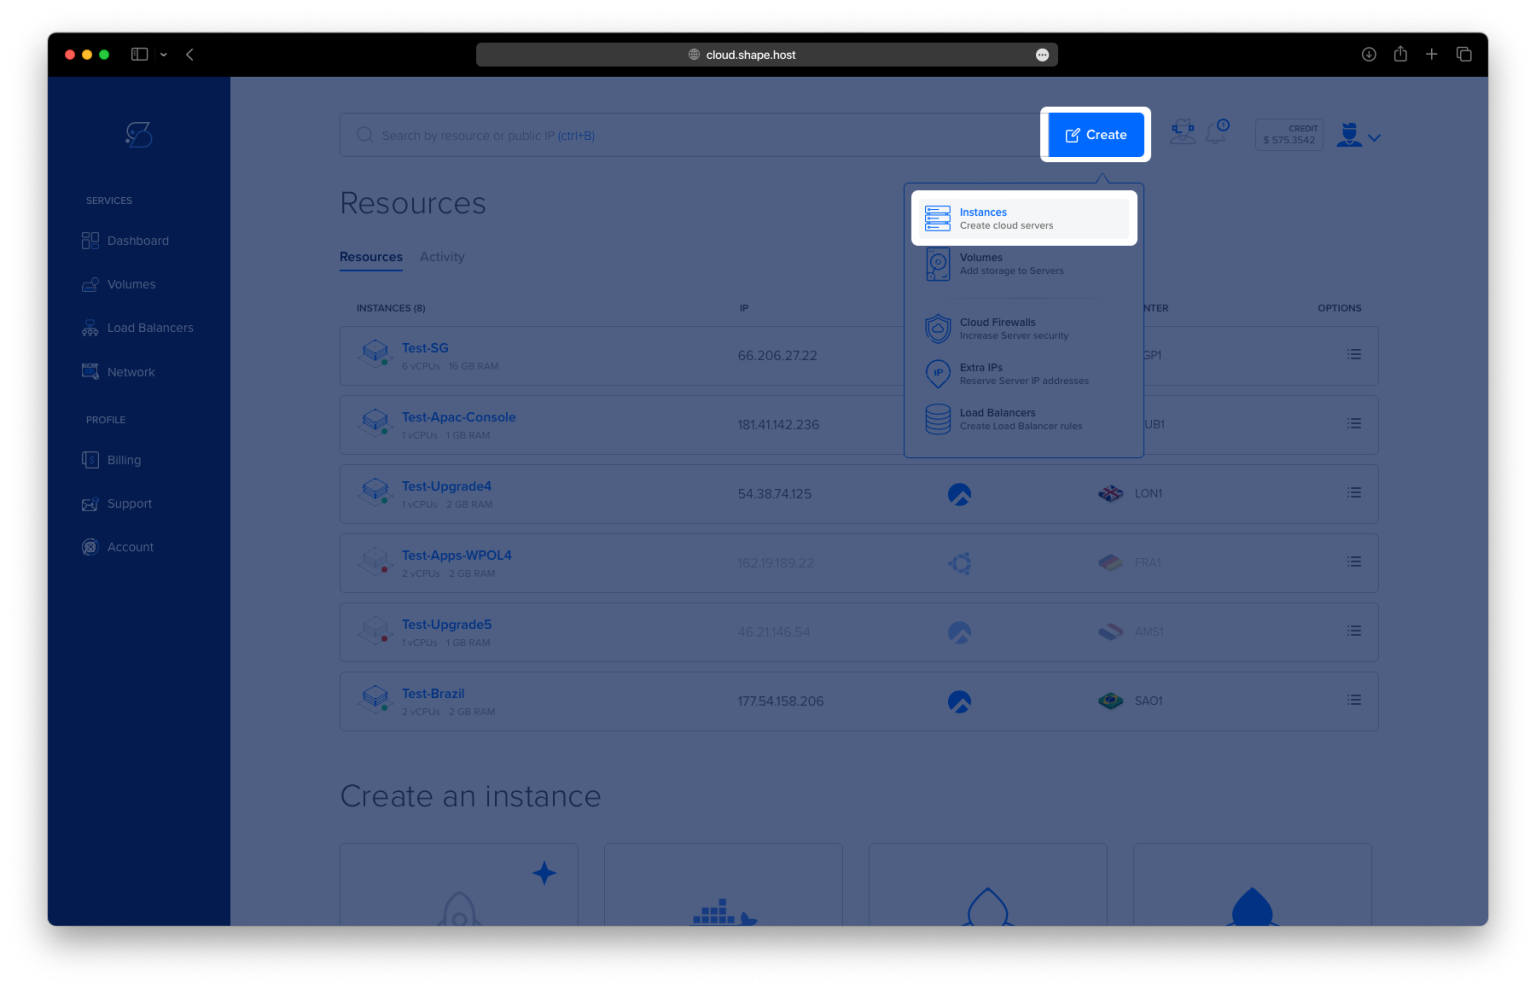
Click Create → Instance.

Choose your desired location.

Select a plan with at least 2 CPUs, 4 GB RAM, and 20 GB SSD.
Choose Ubuntu 24.04 (64-bit) as the operating system.

Click Create Instance.

Once deployed, copy your IP address from the “Resources” section — you’ll use it to connect via SSH.

Step 2: Connect to Your Server
Use SSH to connect as root:
ssh root@your_server_ip
Step 3: Update Your Server
Always start with an update:
apt update
This ensures all repositories and system packages are up to date.

Step 4: Install Docker and Dependencies
Install required dependencies:
apt install apt-transport-https ca-certificates curl software-properties-common

Add the Docker GPG key:
curl -fsSL https://download.docker.com/linux/ubuntu/gpg | gpg --dearmor -o /usr/share/keyrings/docker-archive-keyring.gpg
Add the Docker repository:
echo "deb [arch=$(dpkg --print-architecture) signed-by=/usr/share/keyrings/docker-archive-keyring.gpg] \
https://download.docker.com/linux/ubuntu $(lsb_release -cs) stable" > /etc/apt/sources.list.d/docker.list
Update the package index again:
apt update

Install Docker and Docker Compose:
apt install docker-ce docker-ce-cli containerd.io docker-compose-plugin
Enable Docker for your user:
usermod -aG docker $USER
Apply group changes:
newgrp docker
Check Docker version to confirm installation:
docker --version
Step 5: Set Up n8n Directory Structure
Create a working directory for n8n:
mkdir ~/n8n
cd ~/n8n
Create directories for persistent storage:
mkdir n8n-data
mkdir local-files
Set proper permissions for the n8n Docker user (ID 1000):
chown -R 1000:1000 n8n-data local-files

Step 6: Create Docker Compose File
Create the Docker Compose configuration:
nano docker-compose.yml
Paste the following content:
services:
  n8n:
    image: n8nio/n8n:latest
    container_name: n8n
    restart: unless-stopped
    ports:
      - "5678:5678"
    environment:
      - N8N_HOST=n8n.example.com
      - N8N_PORT=5678
      - N8N_PROTOCOL=https
      - WEBHOOK_URL=https://n8n.example.com
      - N8N_EDITOR_BASE_URL=https://n8n.example.com
      - GENERIC_TIMEZONE=UTC
      - N8N_USER_FOLDER=/home/node/.n8n
    volumes:
      - ./n8n-data:/home/node/.n8n
      - ./local-files:/files
    networks:
      - n8n-network

networks:
  n8n-network:
    driver: bridge
🔸 Replace
n8n.example.comwith your domain name (or use your server IP for testing).

Step 7: Install and Configure Nginx
Install Nginx:
apt install nginx

Create a configuration file for your n8n domain:
nano /etc/nginx/sites-available/n8n.example.com
Paste this configuration:
server {
    listen 80;
    server_name n8n.example.com;

    location / {
        proxy_pass http://localhost:5678;
        proxy_http_version 1.1;
        proxy_set_header Upgrade $http_upgrade;
        proxy_set_header Connection 'upgrade';
        proxy_set_header Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header X-Forwarded-Host $host;
        proxy_set_header X-Forwarded-Port $server_port;

        # WebSocket support
        proxy_buffering off;

        # Timeout settings for long-running workflows
        proxy_read_timeout 300s;
        proxy_connect_timeout 75s;
    }
}

Enable the configuration by creating a symbolic link:
ln -s /etc/nginx/sites-available/n8n.example.com /etc/nginx/sites-enabled/
Test for syntax errors:
nginx -t
Reload Nginx:
systemctl reload nginx
Step 8: Configure the Firewall
Allow necessary ports:
ufw allow 80/tcp
ufw allow 443/tcp
ufw allow ssh
ufw enable

Step 9: Enable HTTPS (SSL) with Certbot
Install Certbot for automatic SSL certificates:
apt install certbot python3-certbot-nginx

Generate and apply an SSL certificate:
certbot --nginx -d n8n.example.com --email contact@shape.host --agree-tos --non-interactive
Replace
n8n.example.comand email with your actual domain and contact address.

Step 10: Start n8n
Navigate to the project directory:
cd ~/n8n
Pull the Docker image and start the container:
docker compose up -d

Check running containers:
docker compose ps

View n8n logs:
docker logs n8n

Step 11: Access the n8n Dashboard
Open your web browser and go to:
https://n8n.example.com
or
http://YOUR_SERVER_IP:5678
You’ll now see the n8n visual workflow builder interface.


You installed n8n on Ubuntu 24.04 with Docker, Nginx, and SSL via Certbot.
Your n8n instance is now ready to build and automate complex workflows securely.
For optimal performance, run n8n on a Shape.Host Linux SSD VPS — optimized for Docker-based applications with root-level access and scalable SSD infrastructure.