Nhost on Rocky Linux 9 (Docker Compose + PostgreSQL + Hasura + GraphQL + SSL)
Nhost is an open-source backend-as-a-service (BaaS) platform that provides a complete, self-hosted backend stack — including PostgreSQL, Hasura GraphQL APIs, authentication, file storage, and serverless functions. Designed as a Firebase alternative, it delivers instant backend functionality while keeping your data under your full control.
Running Nhost on Rocky Linux 9, a community-driven, RHEL-compatible enterprise operating system, ensures a secure, stable, and long-term supported environment. With SELinux enforcement, systemd 252, OpenSSL 3, and full Docker compatibility, Rocky Linux 9 provides an ideal base for hosting Nhost in production — complete with Docker Compose orchestration and SSL integration.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | Rocky Linux 9 | RHEL-compatible, enterprise-grade Linux with SELinux enabled |
| Container Runtime | Docker Engine + Compose | Orchestrates Nhost services and dependencies |
| Database | PostgreSQL 15 | Stores application data, user profiles, and configurations |
| GraphQL Engine | Hasura | Generates real-time GraphQL APIs automatically from PostgreSQL schemas |
| Auth Service | Nhost Auth (GoTrue) | Manages user authentication and authorization via JWT and OAuth |
| Storage | Nhost Storage | Handles file uploads and secure access using S3-compatible storage |
| Functions | Nhost Functions (Node.js) | Runs custom serverless backend logic |
| Reverse Proxy | Nginx / Traefik (optional) | Manages HTTPS, caching, and request routing |
| TLS | Let’s Encrypt / PKI | Provides secure HTTPS connections for APIs and dashboard |
Why Use Nhost?
- Open-source Firebase alternative with full backend control.
- PostgreSQL-powered – relational data with JSONB and extensions.
- GraphQL APIs – generated instantly via Hasura for rapid development.
- Integrated authentication – JWT, OAuth, and magic link support.
- File storage and serverless functions included by default.
- Fully self-hosted – deploy anywhere for privacy and compliance.
Nhost vs Other Backend Platforms
| Feature/Capability | Nhost (Self-hosted) | Supabase (Self-hosted) | Firebase (Google) | Appwrite (Self-hosted) |
|---|---|---|---|---|
| Database | PostgreSQL | PostgreSQL | Firestore (NoSQL) | MariaDB / PostgreSQL |
| API Type | GraphQL (Hasura) | REST + GraphQL | Proprietary SDK | REST + GraphQL |
| Authentication | GoTrue (JWT) | GoTrue (JWT) | Firebase Auth | Custom JWT |
| File Storage | S3-compatible | S3-compatible | Cloud Storage | Local/S3 drivers |
| Serverless Logic | Node.js Functions | Limited (Edge) | Cloud Functions | Node.js Functions |
| Open-source | Yes | Yes | No | Yes |
Nhost is the best choice for teams that need a powerful, GraphQL-first backend with real-time APIs, authentication, and file storage — all self-hosted and open-source.
Security & Best Practices
- Deploy behind Nginx or Traefik with HTTPS enabled.
- Store credentials and API keys in
.envor Docker secrets securely. - Restrict PostgreSQL and Hasura access to internal Docker networks.
- Keep SELinux enforced for enhanced system-level security.
- Automate PostgreSQL backups with
pg_dumpor volume snapshots. - Update Docker images and Rocky Linux packages regularly.
- Configure firewall (firewalld or nftables) to expose only ports 80/443.
- Automate SSL renewals via Certbot or Traefik ACME integration.
Typical Use Cases
- Web and mobile app backends using GraphQL APIs.
- SaaS products requiring scalable authentication and storage.
- Internal dashboards and business analytics tools.
- Prototypes and MVPs with instant backend deployment.
- Enterprise deployments demanding full data control and compliance.
Deploying Nhost on Rocky Linux 9 with Docker Compose gives you a secure, scalable, and enterprise-grade backend platform that merges PostgreSQL, Hasura, and authentication into a unified stack — delivering all the power of Firebase with the flexibility and transparency of open-source software.
Step 1: Create a Server Instance on Shape.Host
Log in to your Shape.Host account.
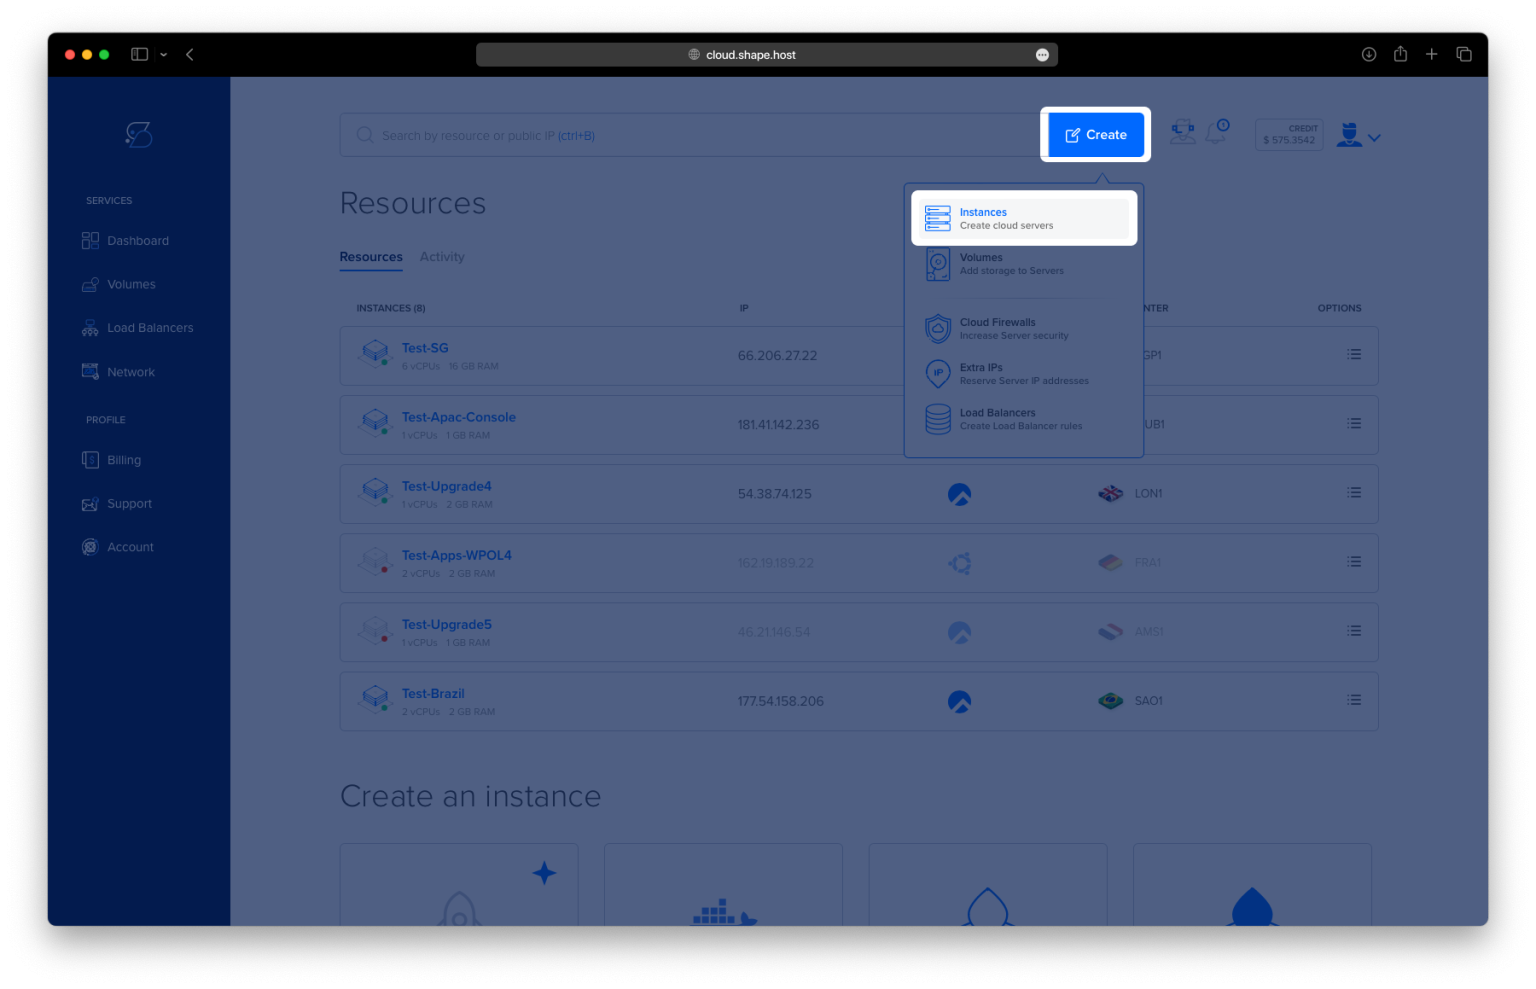
Click Create → Instance.

Choose your preferred data-center region.

Select a plan with at least 4 CPUs, 8 GB RAM, and 40 GB SSD.
Choose Rocky Linux 9 (64-bit) as your operating system.

Click Create Instance.

After deployment, copy your instance’s public IP address from the Resources tab.

Step 2: Connect to Your Server
Use SSH to access your instance:
- Linux/macOS:
ssh root@your_server_ip - Windows (PuTTY):
- Open PuTTY.
- Enter your instance IP.
- Click Open and log in as root.
Step 3: Install Docker and Docker Compose
Install required DNF plugin to manage repositories:
dnf install dnf-plugins-core

This adds repository management commands such as config-manager.
Add the official Docker CE repository:
dnf config-manager --add-repo https://download.docker.com/linux/centos/docker-ce.repo
Even though it’s labeled “CentOS,” this repository works perfectly with Rocky Linux.
Install Docker Engine and all necessary components:
dnf install docker-ce docker-ce-cli containerd.io docker-buildx-plugin docker-compose-plugin
This installs Docker, container runtime, and the Compose plugin.

Enable Docker to start at system boot:
systemctl enable docker
Start the Docker service:
systemctl start docker
Check Docker versions to confirm installation:
docker --version
docker compose version
Step 4: Create Nhost Directory
Create and enter the project directory:
mkdir -p /opt/nhost
cd /opt/nhost
This is where your configuration and application files will live.

Step 5: Configure Nhost with Docker Compose
Create the Docker Compose file:
nano /opt/nhost/docker-compose.yml
Paste the following configuration:
services:
  postgres:
    container_name: nhost-postgres-1
    image: postgres:15
    restart: always
    environment:
      POSTGRES_USER: postgres
      POSTGRES_PASSWORD: "W9b2U8vTKp"
      POSTGRES_DB: nhost
    volumes:
      - postgres_data:/var/lib/postgresql/data
    ports:
      - "5432:5432"

  hasura:
    container_name: hasura
    image: hasura/graphql-engine:v2.41.0
    restart: always
    depends_on:
      - postgres
    ports:
      - "8080:8080"
    environment:
      HASURA_GRAPHQL_DATABASE_URL: "postgres://postgres:W9b2U8vTKp@postgres:5432/nhost"
      HASURA_GRAPHQL_ADMIN_SECRET: "0f8c85264d9d04998fe00881c3c61d9147b51004f5cd1cb7c17d5740d7ab30ef"
      HASURA_GRAPHQL_ENABLE_CONSOLE: "true"
      HASURA_GRAPHQL_JWT_SECRET: '{"type":"HS256","key":"0f8c85264d9d04998fe00881c3c61d9147b51004f5cd1cb7c17d5740d7ab30ef"}'
      HASURA_GRAPHQL_UNAUTHORIZED_ROLE: anonymous
      HASURA_GRAPHQL_CORS_DOMAIN: "*"

  auth:
    container_name: auth
    image: nhost/hasura-auth:latest
    restart: always
    depends_on:
      - postgres
      - hasura
    ports:
      - "4000:4000"
    environment:
      HASURA_GRAPHQL_DATABASE_URL: "postgres://postgres:W9b2U8vTKp@postgres:5432/nhost"
      HASURA_GRAPHQL_ADMIN_SECRET: "0f8c85264d9d04998fe00881c3c61d9147b51004f5cd1cb7c17d5740d7ab30ef"
      HASURA_GRAPHQL_ENDPOINT: "http://hasura:8080/v1/graphql"
      HASURA_GRAPHQL_JWT_SECRET: '{"type":"HS256","key":"0f8c85264d9d04998fe00881c3c61d9147b51004f5cd1cb7c17d5740d7ab30ef"}'
      AUTH_CLIENT_URL: "http://YOUR_SERVER_IP"
      AUTH_JWT_SECRET: '{"type":"HS256","key":"0f8c85264d9d04998fe00881c3c61d9147b51004f5cd1cb7c17d5740d7ab30ef"}'
      AUTH_ADMIN_PASSWORD: "StrongAdminPass123!"
      AUTH_ADMIN_EMAIL: "contact@shape.host"

  minio:
    container_name: nhost-minio-1
    image: minio/minio
    restart: always
    command: server /data --console-address ":9001"
    ports:
      - "9000:9000"
      - "9001:9001"
    environment:
      MINIO_ROOT_USER: "minioadmin"
      MINIO_ROOT_PASSWORD: "minioadminpass"
    volumes:
      - minio_data:/data

  functions:
    container_name: nhost-functions-1
    image: nhost/functions:latest
    restart: always
    depends_on:
      - hasura
    ports:
      - "1337:1337"
    volumes:
      - ./functions:/opt/nhost/functions

volumes:
  postgres_data:
  minio_data:
Explanation of Components
| Service | Description |
|---|---|
| Postgres | Main SQL database for storing app and user data. |
| Hasura | Converts your PostgreSQL schema into a live GraphQL API. |
| Auth | Handles user authentication and JWT token issuance. |
| MinIO | Provides S3-compatible object storage for files. |
| Functions | Enables custom serverless backend logic. |
Save and exit the file with CTRL + O, then CTRL + X.

Step 6: Create Functions Directory
mkdir -p /opt/nhost/functions
This directory will hold your Nhost serverless function files.
Step 7: Start Nhost Services
Start the stack in detached mode:
docker compose up -d
This will pull the required Docker images and launch all containers.

Check if all containers are running:
docker compose ps
You should see all services listed with the status Up.

Step 8: Access Your Nhost Instance
After deployment completes, open your browser and visit:
- Hasura Console:
http://YOUR_SERVER_IP:8080 - Auth API:
http://YOUR_SERVER_IP:4000 - MinIO Console:
http://YOUR_SERVER_IP:9001 - Health Check:
http://YOUR_SERVER_IP:4000/healthz
If /healthz returns OK, your Nhost environment is running correctly.


Step 9 (Optional): Secure with SSL Certificates
To add HTTPS support using Let’s Encrypt, install Certbot:
dnf install certbot python3-certbot-nginx
certbot --nginx -d yourdomain.com
This will automatically configure SSL for your domain.
You’ve successfully installed Nhost on Rocky Linux 9 using Docker Compose.
Your environment now includes:
- A PostgreSQL database
- A Hasura GraphQL API
- A User authentication service
- MinIO file storage
- Support for serverless backend functions
To ensure high performance and scalability, host your Nhost deployment on a Shape.Host Cloud VPS, which offers fast SSD storage, flexible scaling, and full root access for Docker workloads.