Focalboard on Rocky Linux 9 (PostgreSQL + Nginx + SSL)
Focalboard is an open-source project management and collaboration tool that helps teams and individuals organize workflows, tasks, and projects. Comparable to Trello, Asana, or Notion, it offers kanban boards, calendars, task lists, and database-style views. Unlike those SaaS platforms, Focalboard is self-hosted, ensuring that you retain complete control of your infrastructure and data.
Running Focalboard on Rocky Linux 9 — a community-driven, RHEL-compatible enterprise Linux distribution — provides a secure, stable, and long-term supported foundation. With SELinux enforcement, systemd 252, OpenSSL 3, PostgreSQL 15, and modern Node.js support, Rocky Linux is a strong choice for deploying Focalboard behind Nginx with SSL termination, suitable for both small teams and large organizations.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | Rocky Linux 9 | Enterprise-grade, RHEL-compatible Linux base with SELinux enforcement |
| Database | PostgreSQL 15 | Stores boards, tasks, and metadata |
| Application | Focalboard Server | Provides the web interface and APIs for project management |
| Runtime | Node.js (LTS) | Runs the Focalboard backend |
| Process Manager | systemd / PM2 | Ensures Focalboard runs continuously and restarts automatically |
| Reverse Proxy | Nginx | TLS termination, routing, caching, and compression |
| TLS | Let’s Encrypt / PKI | Provides secure HTTPS access for end-users |
Why Use Focalboard?
- Self-hosted alternative to Trello, Asana, or Notion.
- Complete control of data – ideal for compliance and privacy-conscious teams.
- Open-source and free – no licensing fees or vendor lock-in.
- Feature-rich – boards, lists, calendars, filters, and collaboration tools.
- Flexible – useful for freelancers, startups, enterprises, and education.
Focalboard vs Other Tools
| Feature/Capability | Focalboard (Self-hosted) | Trello (Cloud) | Asana (Cloud) | Notion (Cloud) |
|---|---|---|---|---|
| Hosting | Self-hosted | SaaS only | SaaS only | SaaS only |
| Data ownership | Full control | Vendor-owned | Vendor-owned | Vendor-owned |
| Cost | Free, open-source | Paid tiers | Paid tiers | Paid tiers |
| Features | Boards, tasks, calendars | Kanban only | Project mgmt + tasks | Notes + tasks |
Focalboard is ideal for teams that want project management without relying on external SaaS services.
Security & Best Practices
- Deploy Focalboard behind Nginx with SSL enabled.
- Harden PostgreSQL with strong authentication and backups.
- Run the application under a dedicated non-root system user.
- Manage services with systemd to ensure uptime and restarts.
- Keep Node.js, PostgreSQL, and Rocky Linux updated.
- Use SELinux policies and firewall rules for stricter security.
- Add security headers in Nginx (HSTS, CSP, Referrer-Policy, etc.).
Typical Use Cases
- Freelancers managing multiple projects securely.
- Small teams replacing Trello or Asana with a free solution.
- Organizations under compliance requirements needing data sovereignty.
- Educational institutions providing collaboration platforms.
- Enterprises embedding self-hosted project management into IT systems.
Step 1: Create a Server Instance on Shape.Host
Start with a clean Rocky Linux 9 VPS. On Shape.Host:
Log in to your Shape.Host dashboard.
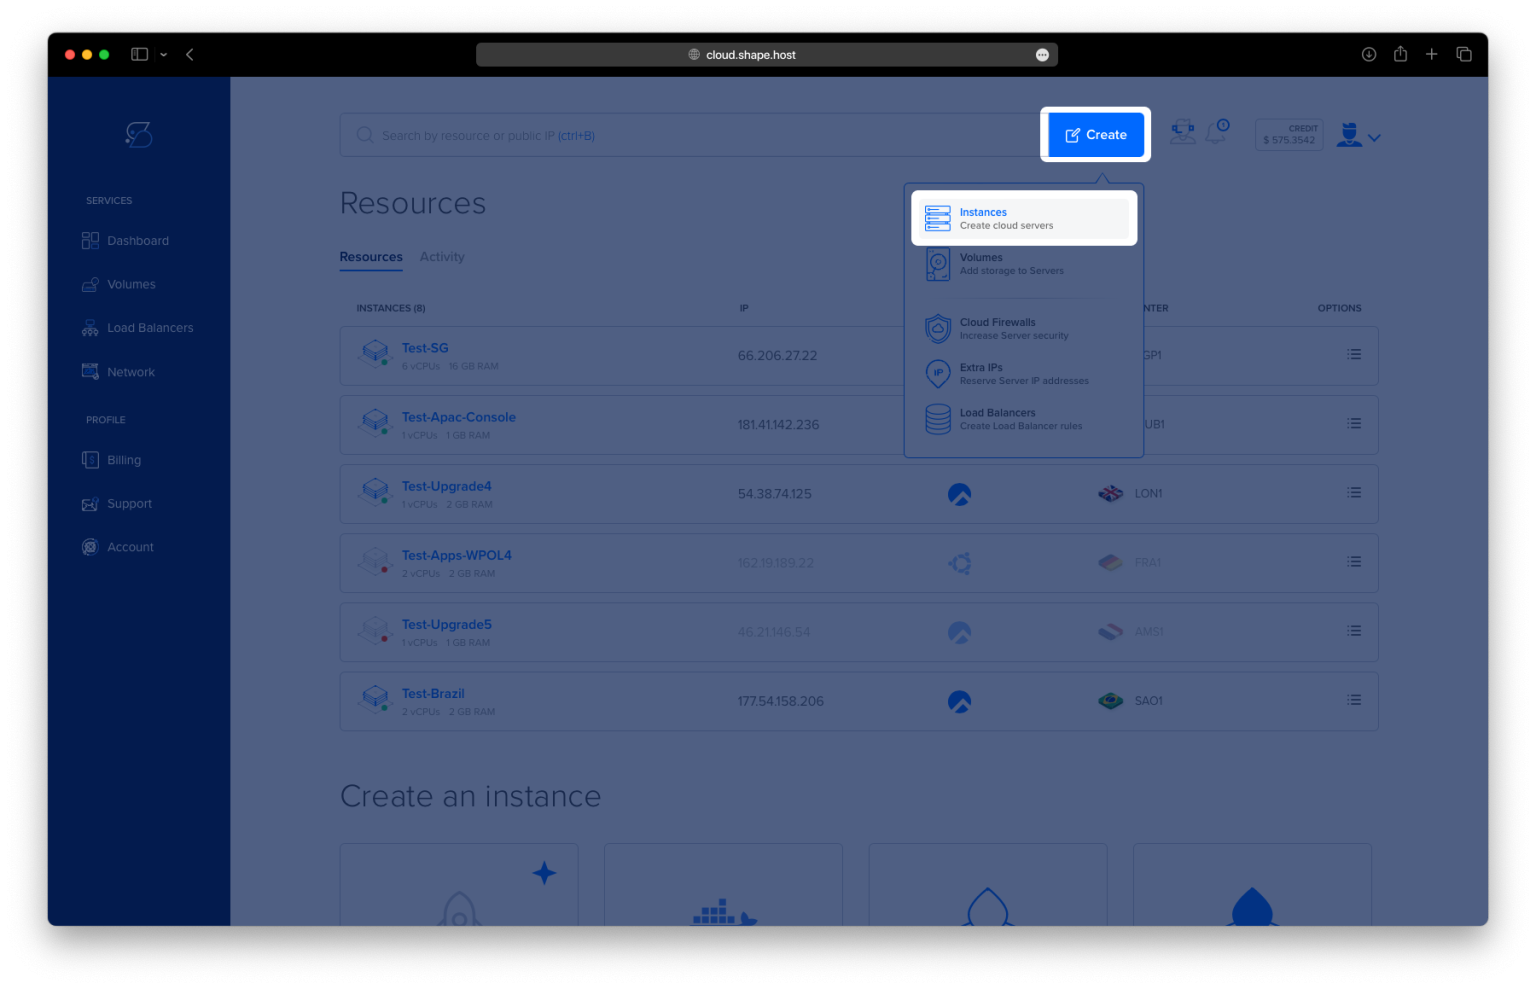
Click Create → Instance.

Choose a data center location close to your users.

Select a plan with at least 2 CPUs, 4 GB RAM, and 20 GB SSD.
Pick Rocky Linux 9 (64-bit) as the OS.

Click Create Instance.

Copy the server’s public IP address from the Resources section.

Step 2: Connect to Your Server
- Linux/macOS:
ssh root@your_server_ip - Windows (PuTTY):
- Open PuTTY, enter your server’s IP.
- Select SSH and connect.
- Log in with the root credentials from Shape.Host.
Step 3: Update System and Install Dependencies
Update system packages:
dnf update

Install essential tools and Nginx with SSL support:
dnf install wget curl unzip nginx certbot python3-certbot-nginx firewalld

Enable and start Nginx:
systemctl enable --now nginx

Step 4: Install and Configure PostgreSQL
Install PostgreSQL server and contrib tools:
dnf install postgresql-server postgresql-contrib

Initialize the database:
postgresql-setup --initdb
Enable and start PostgreSQL:
systemctl enable --now postgresql

Switch to the PostgreSQL user if you want to configure databases:
su - postgres
psql
CREATE DATABASE focalboard;
CREATE USER focaluser WITH PASSWORD 'StrongPassword123!';
GRANT ALL PRIVILEGES ON DATABASE focalboard TO focaluser;
\q
exit(For now, Focalboard will use SQLite by default. You can switch to PostgreSQL by adjusting the config later.)

Step 5: Download and Extract Focalboard
Create a directory for the app:
mkdir -p /opt/focalboard
cd /opt/focalboard
Download Focalboard:
wget https://sourceforge.net/projects/focalboard.mirror/files/v7.10.6/focalboard-server-linux-amd64.tar.gz/download -O focalboard.tar.gz
Extract archive:
tar -xzf focalboard.tar.gz

Step 6: Configure Focalboard
Edit the configuration file:
nano /opt/focalboard/focalboard/config.json
Example config (default SQLite):
{
    "serverRoot": "http://localhost:8000",
    "port": 8000,
    "dbtype": "sqlite3",
    "dbconfig": "./focalboard.db",
    "postgres_dbconfig": "dbname=focalboard sslmode=disable",
    "useSSL": false,
    "webpath": "./pack",
    "filespath": "./files",
    "telemetry": true,
    "prometheusaddress": ":9092",
    "session_expire_time": 2592000,
    "session_refresh_time": 18000,
    "localOnly": false,
    "enableLocalMode": true,
    "localModeSocketLocation": "/var/tmp/focalboard_local.socket"
}

Step 7: Create a systemd Service
Create the service file:
nano /etc/systemd/system/focalboard.service
Paste this configuration:
[Unit]
Description=Focalboard Server
After=network.target

[Service]
Type=simple
Restart=always
RestartSec=5s
ExecStart=/opt/focalboard/focalboard/bin/focalboard-server
WorkingDirectory=/opt/focalboard/focalboard

[Install]
WantedBy=multi-user.target

Reload systemd and start service:
systemctl daemon-reload
systemctl enable --now focalboard
systemctl status focalboard

Step 8: Configure Nginx Reverse Proxy
Create an Nginx configuration:
nano /etc/nginx/conf.d/focalboard.conf
Paste:
upstream focalboard {
    server 127.0.0.1:8000;
    keepalive 32;
}

server {
    listen 80;
    server_name yourdomain.com;

    location / {
        proxy_pass http://focalboard;
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }

    location ~ /ws/* {
        proxy_http_version 1.1;
        proxy_set_header Upgrade $http_upgrade;
        proxy_set_header Connection "upgrade";
        proxy_pass http://focalboard;
    }
}

Test and reload Nginx:
nginx -t
systemctl reload nginx

Step 9: Secure with Let’s Encrypt SSL
Run Certbot to obtain and configure an SSL certificate:
certbot --nginx -d rockylinux-tutorials.shape.host

Now open your site in a browser:
https://rockylinux-tutorials.shape.host
You should see Focalboard running securely.


You installed Focalboard on Rocky Linux 9 with systemd, Nginx reverse proxy, and Let’s Encrypt SSL.
This gives you a production-ready, secure, and scalable setup for project management.
For maximum performance and reliability, deploy Focalboard on Shape.Host Cloud VPS, optimized for apps like Focalboard.