Dozzle Log Viewer on Debian 12 (Docker + Nginx + SSL)
Dozzle is a fast, lightweight log viewer for Docker containers. Instead of attaching manually with docker logs -f, Dozzle provides a real-time, web-based dashboard that streams logs from all running containers in one place. It’s simple to deploy (just one container), requires no database, and gives you instant visibility into your containerized applications.
Debian 12 (Bookworm) provides a stable, secure, and long-supported foundation, with systemd 252, modern OpenSSL 3, and up-to-date Docker packages. It is trusted for production environments, making it an excellent choice for hosting Dozzle in both small-scale and enterprise-grade infrastructures.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | Debian 12 (Bookworm) | Rock-solid base; systemd service supervision |
| Runtime | Docker Engine | Runs Dozzle container in isolation |
| Application | Dozzle | Real-time web UI for viewing container logs |
| Reverse Proxy | Nginx (optional) | TLS termination, routing, access control, HTTP/2 |
| TLS | Let’s Encrypt / PKI | Secure HTTPS for the log viewer |
Why Use Dozzle?
- Zero-setup deployment – Single Docker container, no extra services.
- Real-time visibility – Stream logs instantly across all containers.
- Lightweight & efficient – Minimal CPU/RAM usage compared to ELK or Loki.
- Accessible UI – Simple web interface, no need to SSH into servers.
- Scalable – Works standalone or alongside enterprise logging stacks.
Dozzle vs Other Logging Tools
| Feature/Capability | Dozzle | Loki + Grafana | ELK/EFK Stack | Plain Docker CLI |
|---|---|---|---|---|
| Setup complexity | Very low (1 container) | Medium (multi-service) | High (Elasticsearch, Beats, Kibana, etc.) | None |
| Storage | No (stream only) | Yes (time-series DB) | Yes (Elasticsearch DB) | No |
| UI | Built-in Web UI | Grafana dashboards | Full dashboards | None (terminal) |
| Use case | Quick, live logs | Centralized storage | Enterprise-scale logging | Debug only |
Dozzle excels when you just need a simple, real-time view of logs without the complexity of managing a full observability stack. For persistent log retention or analytics, it works well alongside tools like Loki or ELK.
Security & Best Practices
- Run Dozzle behind Nginx with HTTPS for production access.
- Enable basic authentication or integrate with OAuth/SSO if exposed publicly.
- Restrict access with firewall rules or VPN where possible.
- Keep the Dozzle Docker image updated (
amir20/dozzle:latest). - Pair with Prometheus/Grafana for a complete observability solution.
Typical Use Cases
- Development environments for quick container log inspection.
- Small production servers where full ELK/Loki stacks are overkill.
- Staging/test systems to quickly debug issues.
- Complementing centralized logging with live log tailing.
1. Create a Shape.Host VPS Instance
Go to https://shape.host and log in.
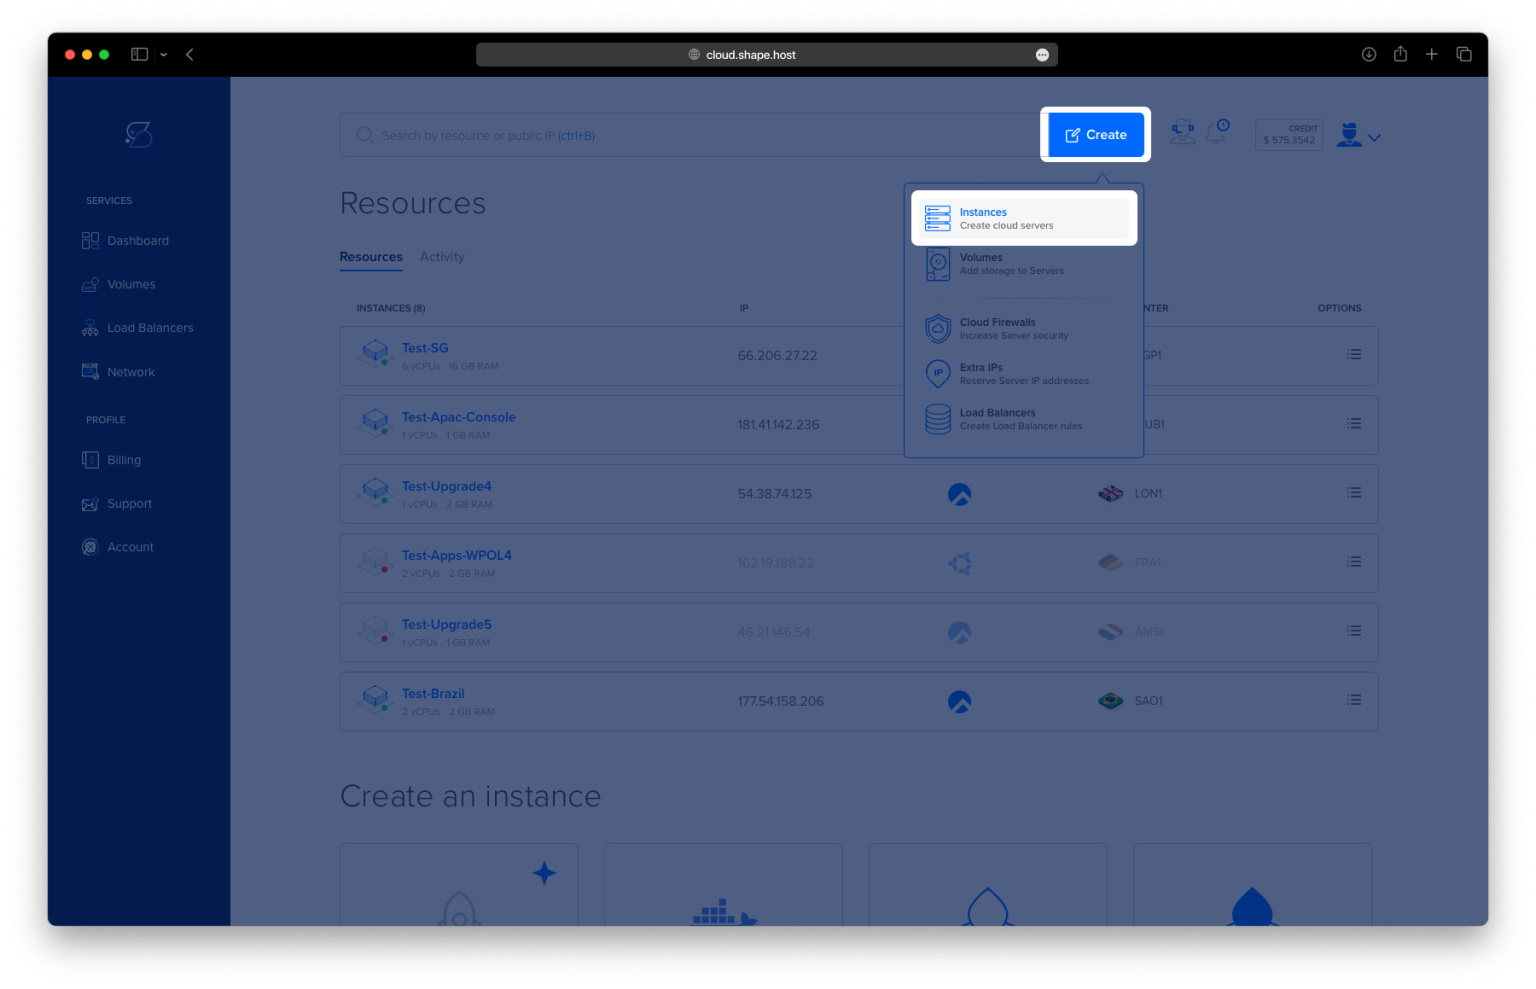
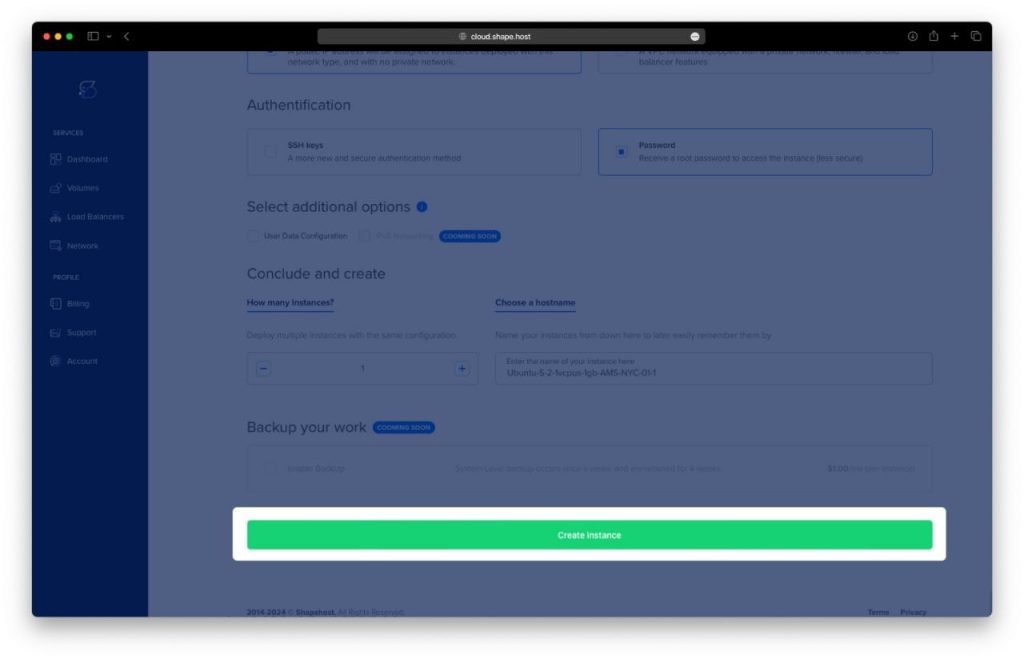
Click “Create” → “Instance”.
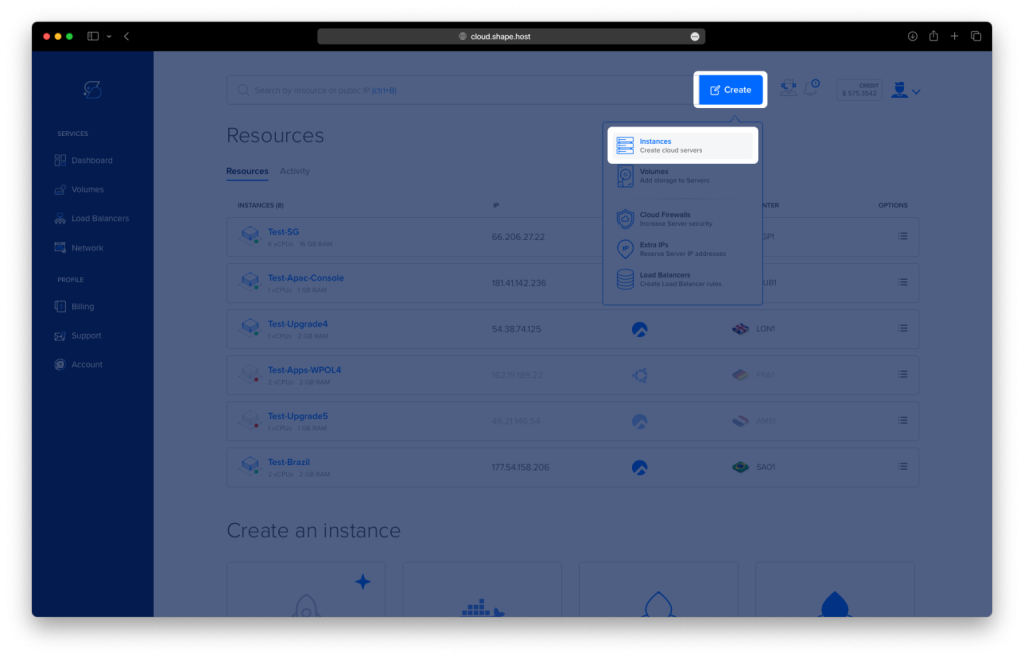
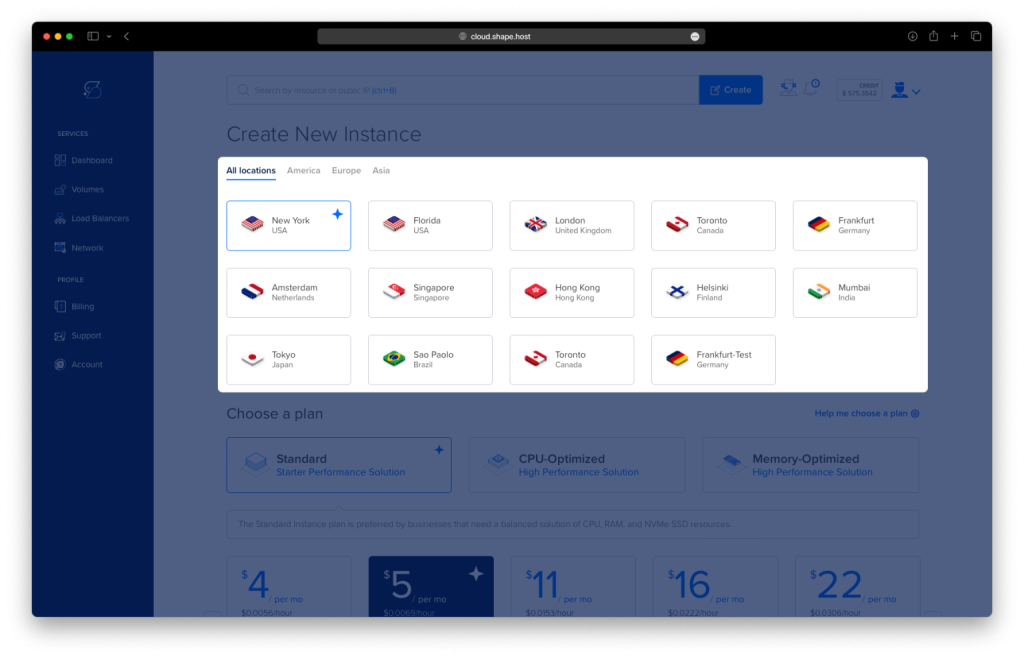
Select a server location closest to your users.
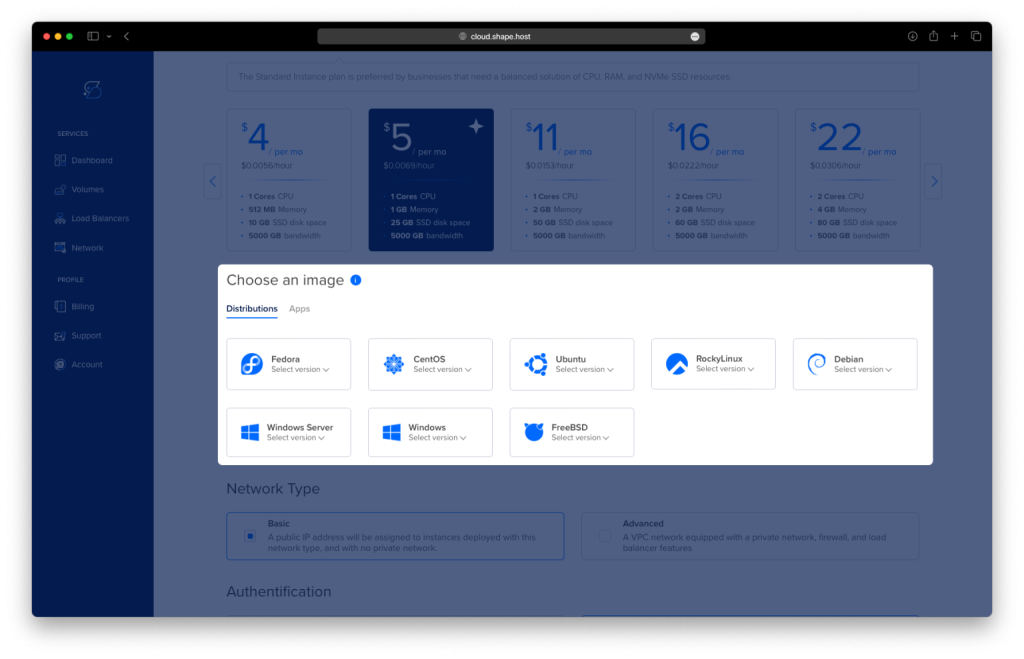
Choose Debian 12 (64-bit) as the OS.
Pick a plan with at least 2 CPUs, 4 GB RAM, and 20 GB SSD.
Click “Create Instance”.
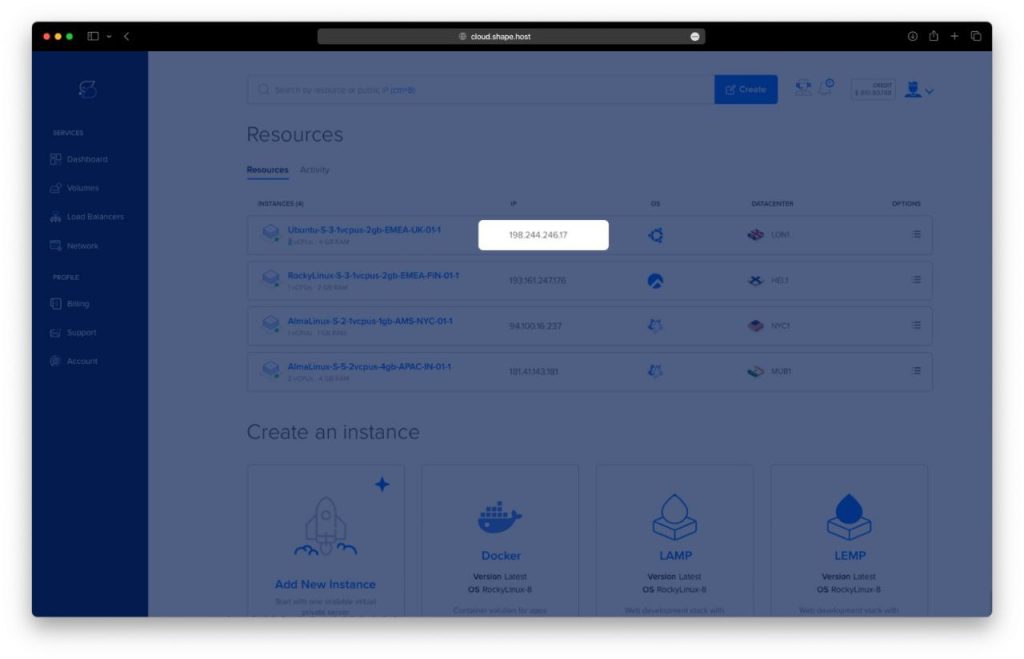
Copy the server IP from the Resources section.
2. Connect to Your VPS
Linux / macOS
ssh root@your-server-ip
Windows
- If on Windows 10/11, open PowerShell:
ssh root@your-server-ip - On older Windows, use PuTTY. Enter your server IP and log in as root.
3. Update the System and Install Prerequisites
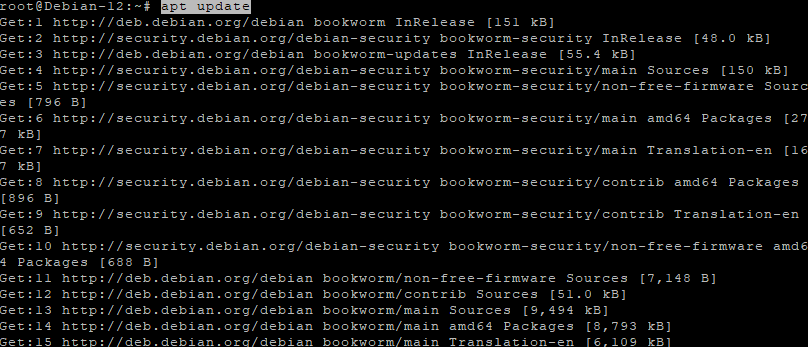
apt update
apt upgrade
Updates the package list and upgrades installed software.
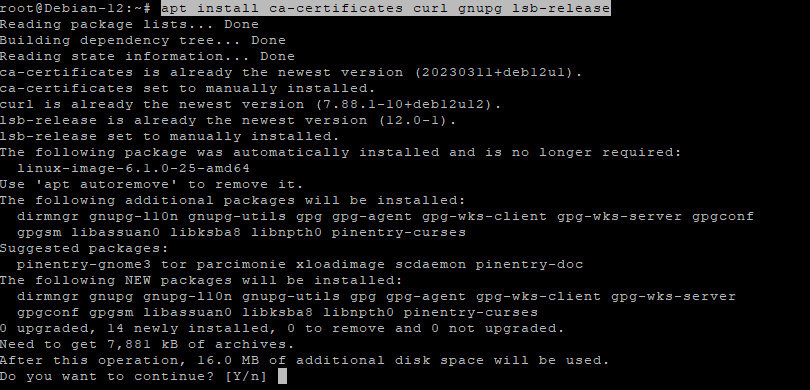
apt install -y ca-certificates curl gnupg lsb-release
Installs required tools for managing repositories securely.
4. Install Docker and Docker Compose
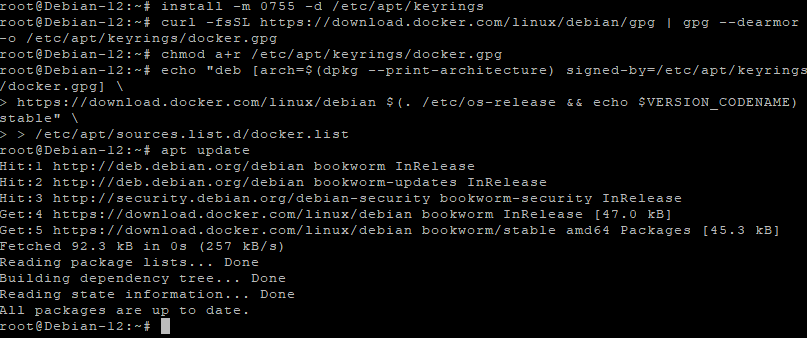
Create the keyrings directory:
install -m 0755 -d /etc/apt/keyrings
Download and store Docker’s GPG key:
curl -fsSL https://download.docker.com/linux/debian/gpg | gpg --dearmor -o /etc/apt/keyrings/docker.gpg
Fix permissions:
chmod a+r /etc/apt/keyrings/docker.gpg
Add Docker’s repository:
echo "deb [arch=$(dpkg --print-architecture) signed-by=/etc/apt/keyrings/docker.gpg] \
https://download.docker.com/linux/debian $(. /etc/os-release && echo $VERSION_CODENAME) stable" > /etc/apt/sources.list.d/docker.list
Update repositories and install Docker:
apt update
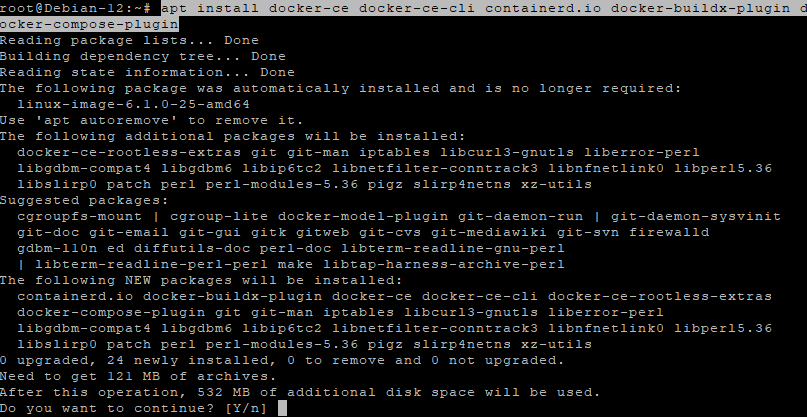
apt install docker-ce docker-ce-cli containerd.io docker-buildx-plugin docker-compose-plugin
Enable Docker at boot:
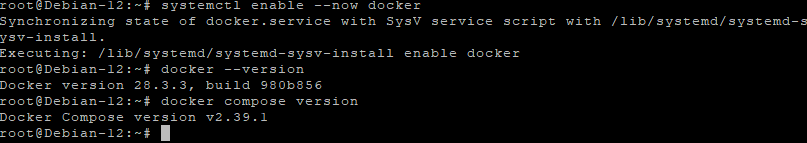
systemctl enable --now docker
Check versions:
docker --version
docker compose version
5. Deploy Dozzle with Docker Compose
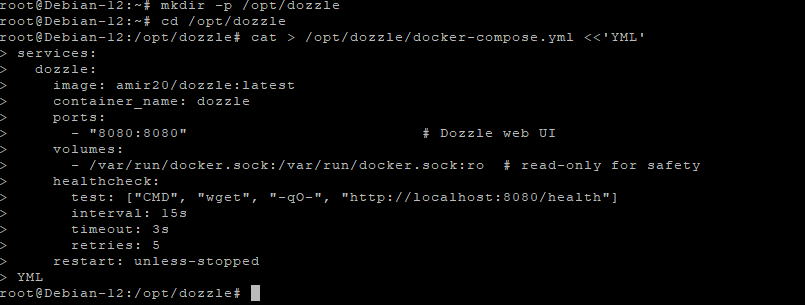
Create directory:
mkdir -p /opt/dozzle
cd /opt/dozzle
Create the Docker Compose file:
cat > /opt/dozzle/docker-compose.yml <<'YML'
services:
  dozzle:
    image: amir20/dozzle:latest
    container_name: dozzle
    ports:
      - "8080:8080"                          # Dozzle web UI
    volumes:
      - /var/run/docker.sock:/var/run/docker.sock:ro  # read-only for safety
    healthcheck:
      test: ["CMD", "wget", "-qO-", "http://localhost:8080/health"]
      interval: 15s
      timeout: 3s
      retries: 5
    restart: unless-stopped
YML
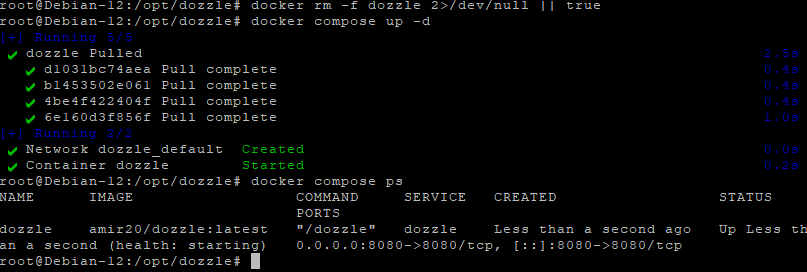
Remove any old container:
docker rm -f dozzle 2>/dev/null || true
Start Dozzle:
docker compose up -d
Check running containers:
docker compose ps
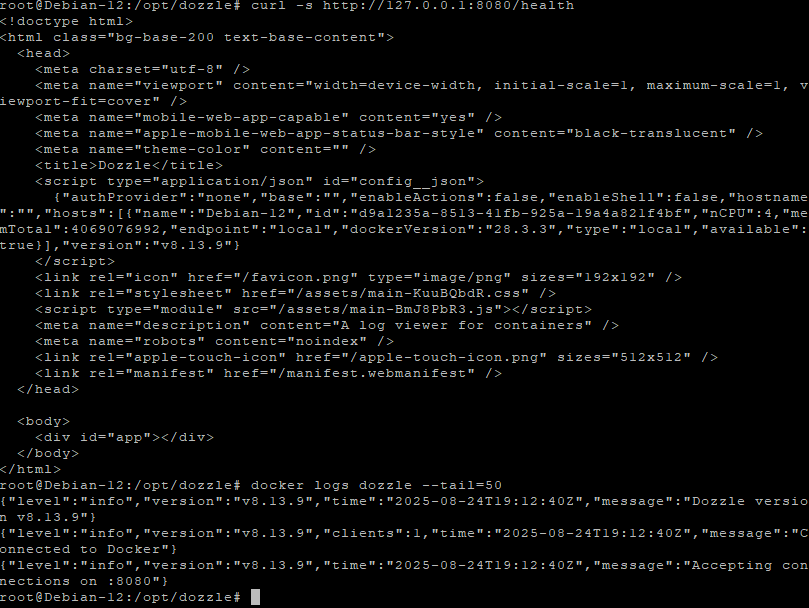
Verify health check:
curl -s http://127.0.0.1:8080/health
Check logs:
docker logs dozzle --tail=50
6. Configure Nginx as Reverse Proxy
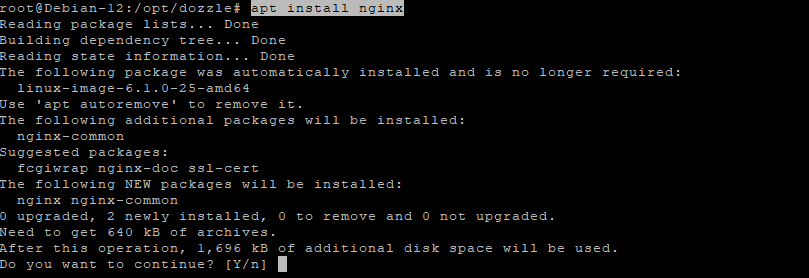
Install Nginx:
apt install nginx
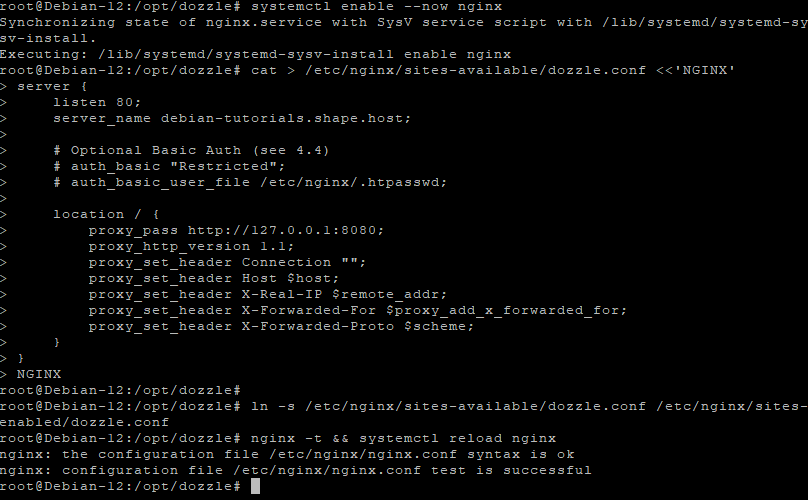
Enable and start Nginx:
systemctl enable --now nginx
Create site configuration:
cat > /etc/nginx/sites-available/dozzle.conf <<'NGINX'
server {
    listen 80;
    server_name your-domain.com;

    # Optional Basic Auth (see 4.4)
    # auth_basic "Restricted";
    # auth_basic_user_file /etc/nginx/.htpasswd;

    location / {
        proxy_pass http://127.0.0.1:8080;
        proxy_http_version 1.1;
        proxy_set_header Connection "";
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
NGINX
Enable the site and reload Nginx:
ln -s /etc/nginx/sites-available/dozzle.conf /etc/nginx/sites-enabled/dozzle.conf
nginx -t && systemctl reload nginx
7. Enable SSL with Let’s Encrypt
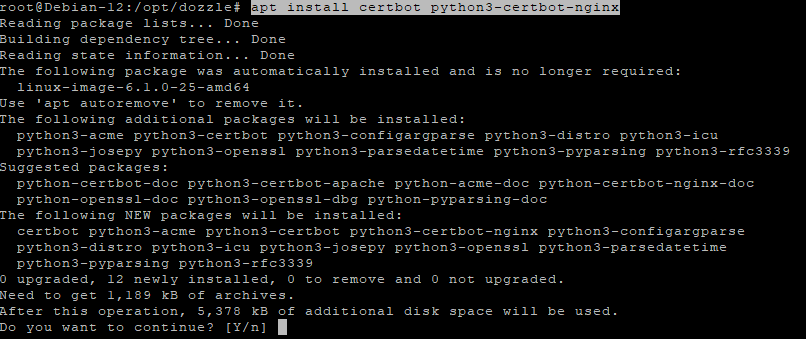
Install Certbot:
apt install certbot python3-certbot-nginx
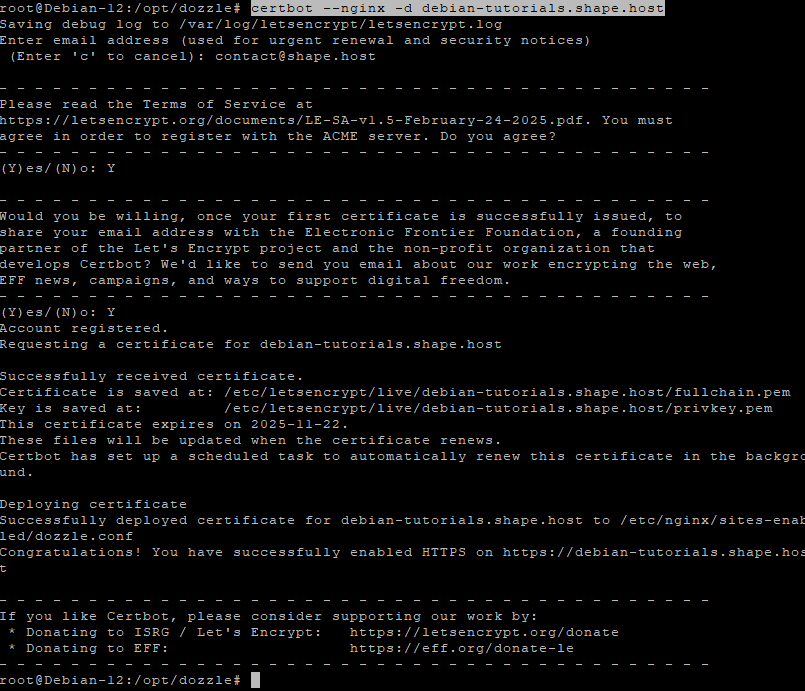
Obtain a free SSL certificate:
certbot --nginx -d your-domain.com
8. Access Dozzle
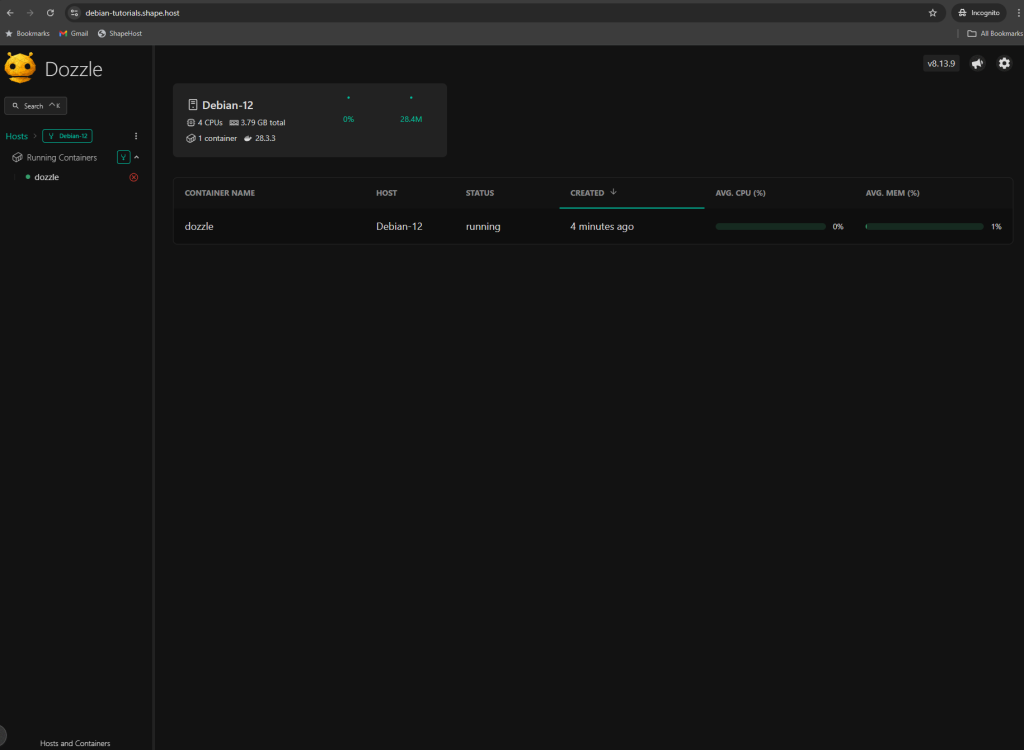
Now open your browser and go to:
https://your-domain.com
You’ll see the Dozzle log viewer UI, showing real-time logs from your Docker containers 🎉.
This tutorial was tested on a Shape.Host Cloud VPS.
With Shape.Host you can:
- Deploy fast, reliable VPS servers worldwide.
- Choose from Debian, Ubuntu, AlmaLinux, Rocky Linux.
- Scale resources instantly as your projects grow.
- Use built-in backups, snapshots, and monitoring.
Start today at https://shape.host and set up Dozzle in just a few minutes.