Dozzle Log Viewer on Rocky Linux 9 (Docker + Nginx + SSL)
Dozzle is a lightweight, web-based log viewer for Docker containers. Instead of running docker logs -f on each container, Dozzle gives you a real-time, searchable dashboard where you can see logs from all containers in one place. It runs as a single container with no database, making it fast to deploy and easy to maintain — perfect for developers and sysadmins who want instant visibility into their workloads without the complexity of a full logging stack.
Rocky Linux 9 is a community-driven, RHEL-compatible enterprise distribution that focuses on stability, performance, and long-term support. With strong security updates and binary compatibility with Red Hat Enterprise Linux, Rocky Linux provides a reliable foundation for running production services like Dozzle.
Architecture Overview
| Layer | Component | Role |
|---|---|---|
| OS | Rocky Linux 9 | Enterprise-grade, RHEL-compatible base with long-term support |
| Runtime | Docker Engine | Runs Dozzle in an isolated container |
| Application | Dozzle | Real-time web UI for container logs |
| Reverse Proxy | Nginx (optional) | TLS termination, routing, HTTP/2, compression, authentication |
| TLS | Let’s Encrypt / PKI | Provides HTTPS for secure log access |
Why Use Dozzle?
- One-command setup – runs as a single Docker container.
- Instant log visibility – stream logs across all containers in real time.
- Low resource usage – extremely lightweight compared to ELK or Loki stacks.
- Simple web UI – easy access to logs without SSH.
- Flexible integration – use it standalone or alongside centralized logging systems.
Dozzle vs Other Logging Tools
| Feature/Capability | Dozzle | Loki + Grafana | ELK/EFK Stack | Docker CLI |
|---|---|---|---|---|
| Setup complexity | Very low (1 container) | Medium (multi-service) | High (Elasticsearch, Beats, Kibana) | None |
| Log storage | No (stream only) | Yes (time-series DB) | Yes (Elasticsearch DB) | No |
| UI | Built-in web UI | Grafana dashboards | Kibana dashboards | None (terminal) |
| Use case | Quick log viewing | Centralized logging | Enterprise log analysis | Debugging only |
Dozzle shines when you need real-time logs without setup overhead, while ELK or Loki stacks are better suited for environments that require long-term log retention and advanced analytics.
Security & Best Practices
- Place Dozzle behind Nginx with SSL for secure external access.
- Add basic authentication or SSO/OAuth for user access control.
- Limit exposure with firewall rules and SELinux/AppArmor.
- Regularly update Dozzle (
amir20/dozzle:latest) to patch vulnerabilities. - Use alongside monitoring tools (Prometheus, Grafana) for full observability.
Typical Use Cases
- Development environments for quick container debugging.
- Staging or test servers where a lightweight solution is enough.
- Small to medium production setups that don’t need centralized log retention.
- Complementing heavy stacks (ELK/Loki) with fast, live log streaming.
1. Create a Shape.Host VPS Instance
Go to https://shape.host and log in.
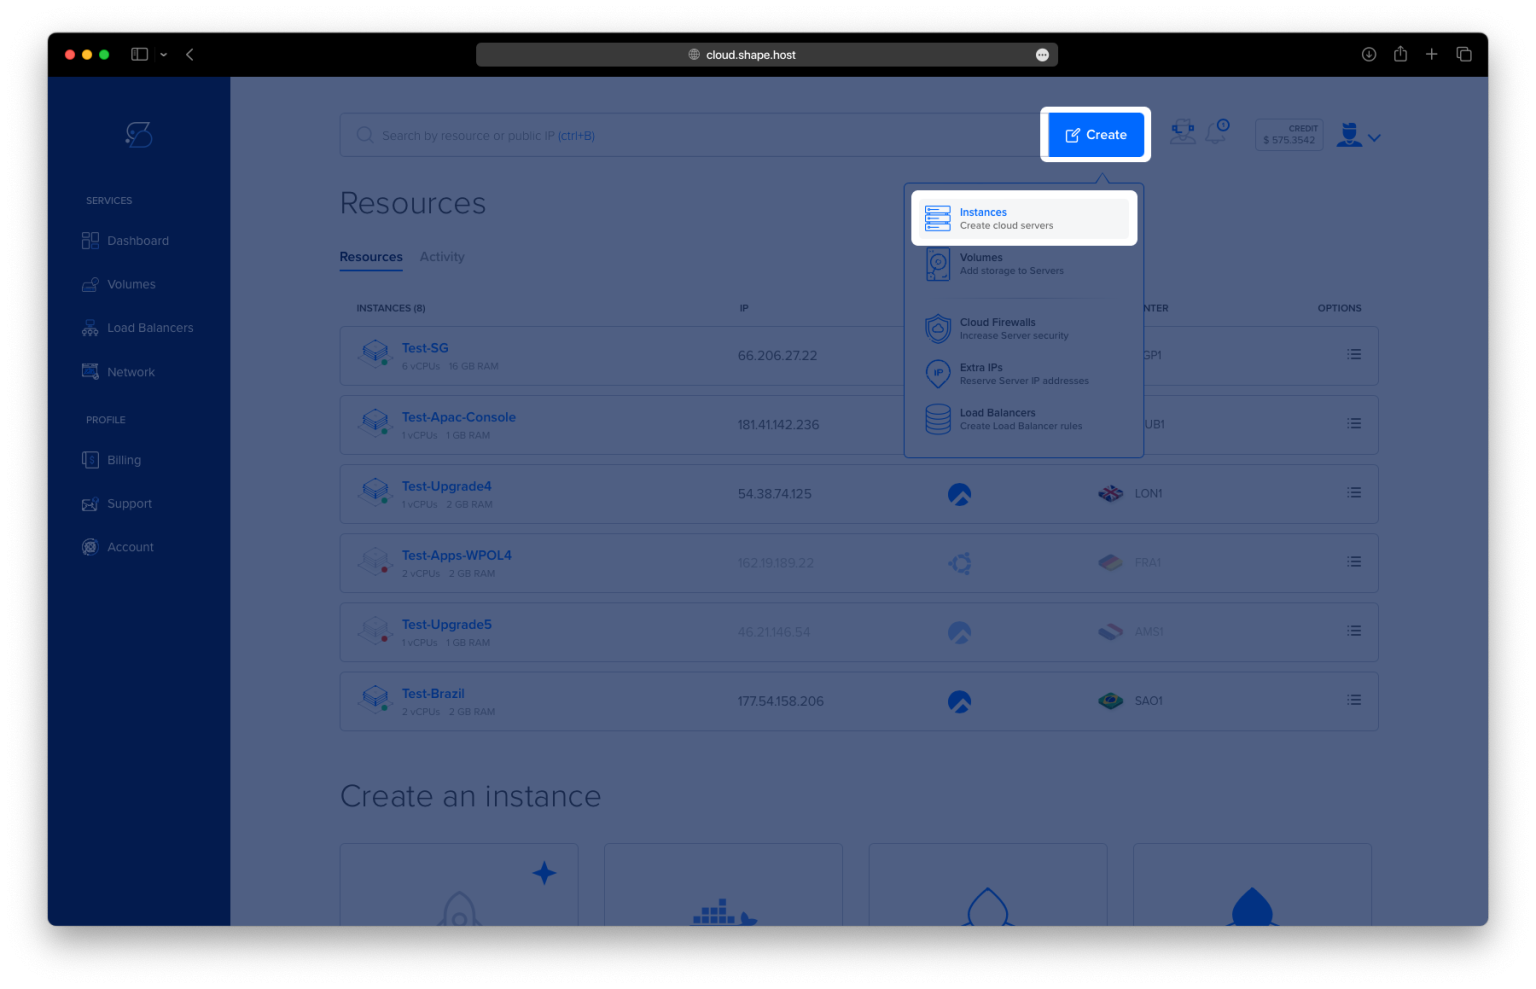
Click “Create” → “Instance”.

Select the server location closest to your users.

Choose Rocky Linux 9 (64-bit) as the OS.
Pick a plan with at least 2 CPUs, 4 GB RAM, and 20 GB SSD.

Click “Create Instance”.

Copy the IP address from the Resources section.

2. Connect to Your VPS
On Linux/macOS
ssh root@your-server-ip
On Windows
- If using PowerShell on Windows 10/11:
ssh root@your-server-ip - On older Windows, download PuTTY, enter your server IP, and log in as root.
3. Update the System and Install Required Tools
dnf update
Updates all system packages.

dnf install yum-utils device-mapper-persistent-data lvm2 curl wget
Installs repository management utilities and basic tools.

4. Install Docker and Docker Compose
Add the official Docker repository:
dnf config-manager --add-repo https://download.docker.com/linux/centos/docker-ce.repo
Install Docker CE and plugins:
dnf install docker-ce docker-ce-cli containerd.io docker-buildx-plugin docker-compose-plugin

Enable and start Docker:
systemctl enable --now docker
Check versions:
docker --version
docker compose version

5. Deploy Dozzle with Docker Compose
Create directory:
mkdir -p /opt/dozzle
cd /opt/dozzle
Create the docker-compose.yml file:
cat > /opt/dozzle/docker-compose.yml <<'YML'
services:
  dozzle:
    image: amir20/dozzle:latest
    container_name: dozzle
    ports:
      - "8080:8080"
    volumes:
      - /var/run/docker.sock:/var/run/docker.sock:ro
    healthcheck:
      test: ["CMD", "wget", "-qO-", "http://localhost:8080/health"]
      interval: 15s
      timeout: 3s
      retries: 5
    restart: unless-stopped
YML

Remove any old Dozzle container if it exists:
docker rm -f dozzle 2>/dev/null || true
Start Dozzle:
docker compose up -d
Check running containers:
docker compose ps

View logs:
docker logs dozzle --tail=50
Test health endpoint:
curl -s http://127.0.0.1:8080/health

6. Configure Nginx as Reverse Proxy
Install Nginx:
dnf install nginx

Enable and start Nginx:
systemctl enable --now nginx
Create configuration file:
cat > /etc/nginx/conf.d/dozzle.conf <<'NGINX'
server {
    listen 80;
    server_name your-domain.com;

    # Optional Basic Auth (see 4.4)
    # auth_basic "Restricted";
    # auth_basic_user_file /etc/nginx/.htpasswd;

    location / {
        proxy_pass http://127.0.0.1:8080;
        proxy_http_version 1.1;
        proxy_set_header Connection "";
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
NGINX
Test and reload Nginx:
nginx -t && systemctl reload nginx

7. Enable SSL with Let’s Encrypt
Install Certbot:
dnf install certbot python3-certbot-nginx

Run Certbot to issue a free SSL certificate:
certbot --nginx -d your-domain.com

8. Access Dozzle
Now open your browser and visit:
https://your-domain.com
You should see the Dozzle log viewer UI, showing real-time Docker logs. 🎉

This tutorial was created and tested on a Shape.Host Cloud VPS.
With Shape.Host you can:
- Deploy fast, reliable Cloud VPS servers worldwide.
- Run Linux distributions like Rocky Linux, AlmaLinux, Debian, Ubuntu.
- Scale resources instantly (CPU, RAM, Storage) as your project grows.
- Take advantage of snapshots, backups, and monitoring.
Start your own VPS at https://shape.host and deploy Dozzle in just a few minutes.