What is OpenLDAP?
OpenLDAP is an open-source implementation of the Lightweight Directory Access Protocol (LDAP). It provides a hierarchical, centralized directory service for managing and querying user accounts, groups, roles, and other structured data.
OpenLDAP is widely used for:
- Centralized authentication and authorization
- Directory-based configuration and access control
- Identity and account management across multiple systems
- Integration with Linux, Windows, and third-party applications
Why Use OpenLDAP on Debian 12?
Debian 12 “Bookworm” is known for its stability, security, and long-term support, making it a reliable choice for deploying OpenLDAP in production environments.
Key benefits of using OpenLDAP on Debian 12:
- Available via official APT repositories with OpenLDAP 2.5+
- Systemd-based service management and improved logging
- Integration with PAM, NSS, Kerberos, and SSSD
- Full support for IPv6, TLS encryption, and modern password hashing
- Regular security updates and package stability from Debian maintainers
Core Components in an OpenLDAP Setup
- slapd – The main OpenLDAP directory server daemon
- ldap-utils – A set of command-line tools for managing and querying the LDAP directory
- LDIF files – Used to define and load entries and schemas
- Schemas – Define structure for entries (e.g., person, groupOfNames, inetOrgPerson)
- Access Control Lists (ACLs) – Enforce permissions at the entry or attribute level
- TLS – Provides encrypted communication using SSL certificates
Typical Use Cases
- Managing user logins for multiple Linux servers from a central source
- Authenticating web applications or internal tools via LDAP
- Hosting a shared company-wide address book
- Integrating with email servers, Samba, or FTP servers for unified access
- Supporting compliance and audit needs for identity control
Key Features of OpenLDAP on Debian 12
| Feature | Description |
|---|---|
| Directory Structure | Hierarchical and searchable (e.g., dc=company,dc=com) |
| Secure Communication | Supports TLS/SSL and SASL authentication |
| Flexible Schemas | Extend or customize object classes and attributes |
| Fine-Grained Access Control | ACLs allow per-user or per-group permissions |
| Replication | Multi-master or read-only replication for high availability |
| Integration Ready | Works with PAM, SSSD, sudo, Samba, Kerberos, and more |
Security Considerations
- Use StartTLS or LDAPS to encrypt directory traffic
- Enforce strong password hashing (e.g., SSHA, bcrypt)
- Restrict anonymous access and disable unused bind methods
- Harden access via ACLs, limiting read/write scope by user/group
- Use firewalld or UFW to restrict access to LDAP ports (389/636)
- Regularly monitor logs and bind activity with
journalctlor custom syslog configurations
Administrative Tools and Interfaces
- ldapsearch / ldapadd / ldapmodify / ldapdelete – CLI tools for managing directory entries
- phpLDAPadmin – Web-based GUI (optional, lightweight)
- LDAP Account Manager (LAM) – Advanced web interface for user/group management
- SSSD + NSS/PAM – For integrating OpenLDAP authentication into Linux login systems
Debian 12 Configuration Notes
- Debian 12 uses the dynamic runtime configuration model (
cn=config) instead of the older staticslapd.conf - Configuration is managed using
ldapmodifyorslapaddwith LDIF format - You can reconfigure the server interactively using
dpkg-reconfigure slapd - Default database backend is MDB (Memory-Mapped Database) for performance and stability
Common Directory Layout
For a domain like example.org, the structure would be:
- Base DN:
dc=example,dc=org - Users OU:
ou=People,dc=example,dc=org - Groups OU:
ou=Groups,dc=example,dc=org - Admin DN:
cn=admin,dc=example,dc=org(bind user)
Deploying OpenLDAP on Debian 12 provides a robust, scalable, and secure directory service for managing user identities and access control across your infrastructure. Debian’s conservative update policies, paired with OpenLDAP’s flexibility, make this combination highly suitable for enterprise-grade and long-term deployments.
Whether you’re implementing centralized logins, integrating authentication across multiple systems, or managing users in a mixed environment, OpenLDAP on Debian 12 offers the tools and stability required.
🔹 Create a Server Instance on Shape.Host
Before installation, provision a clean Debian 12 VPS:
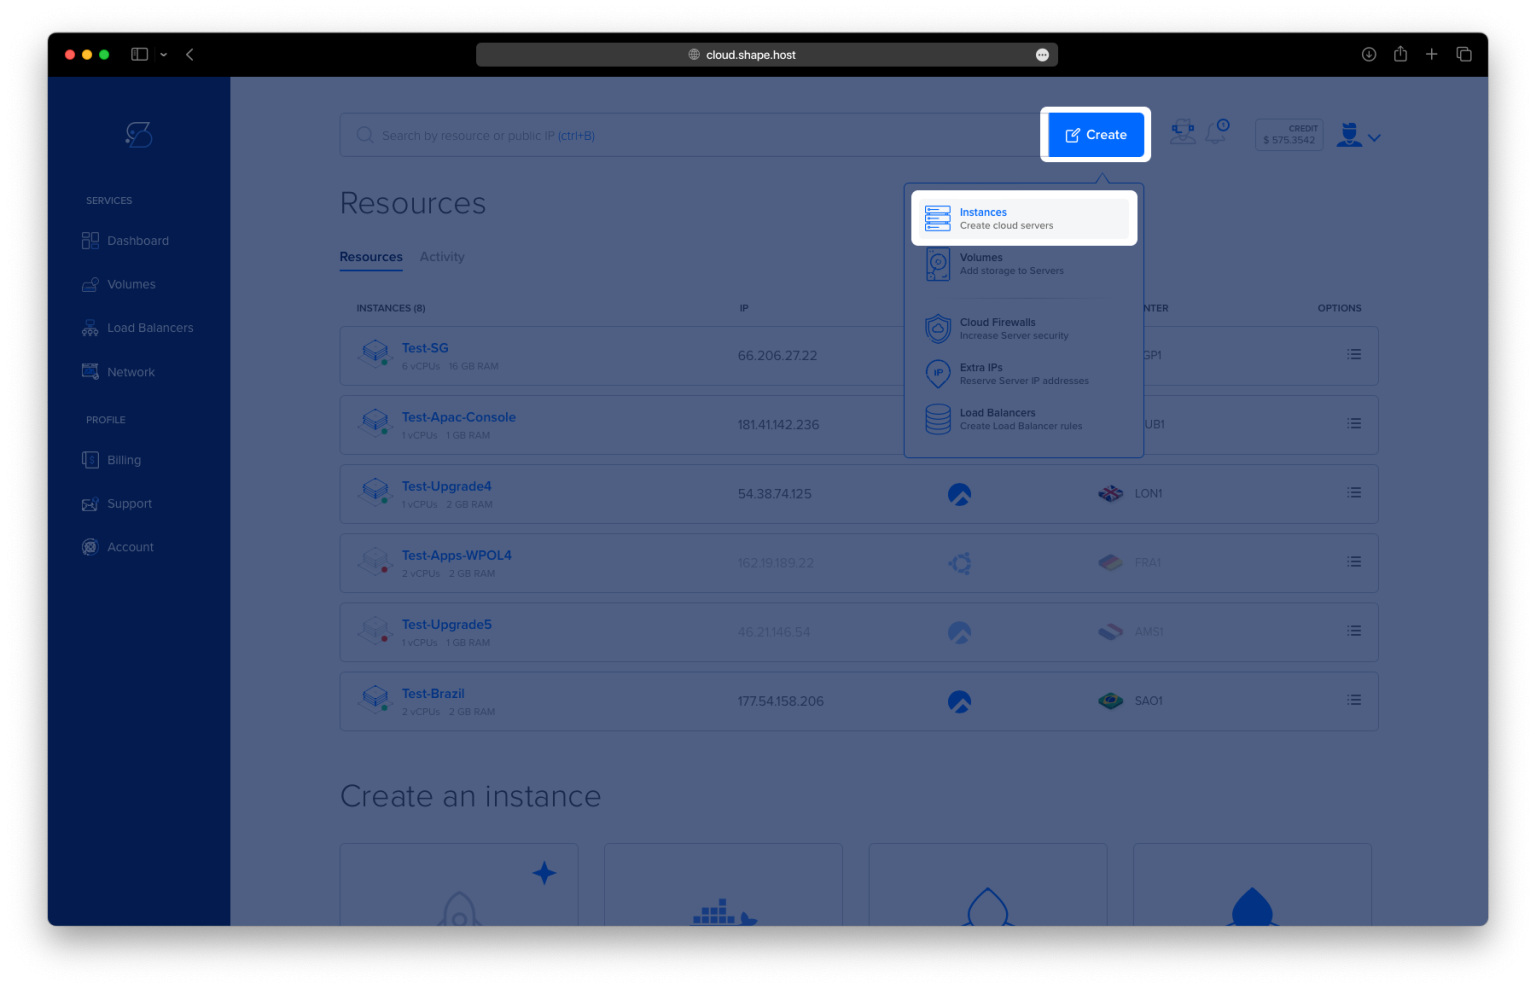
Go to https://shape.host and log in.
Click “Create”, then choose “Instance”.
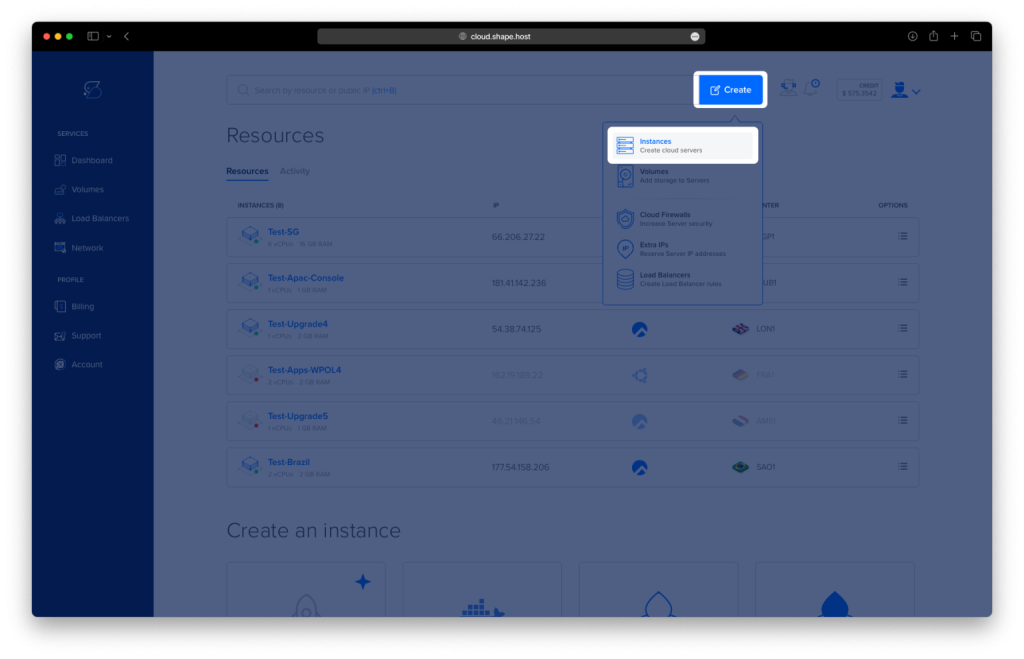
Set:
Location: your preferred region.
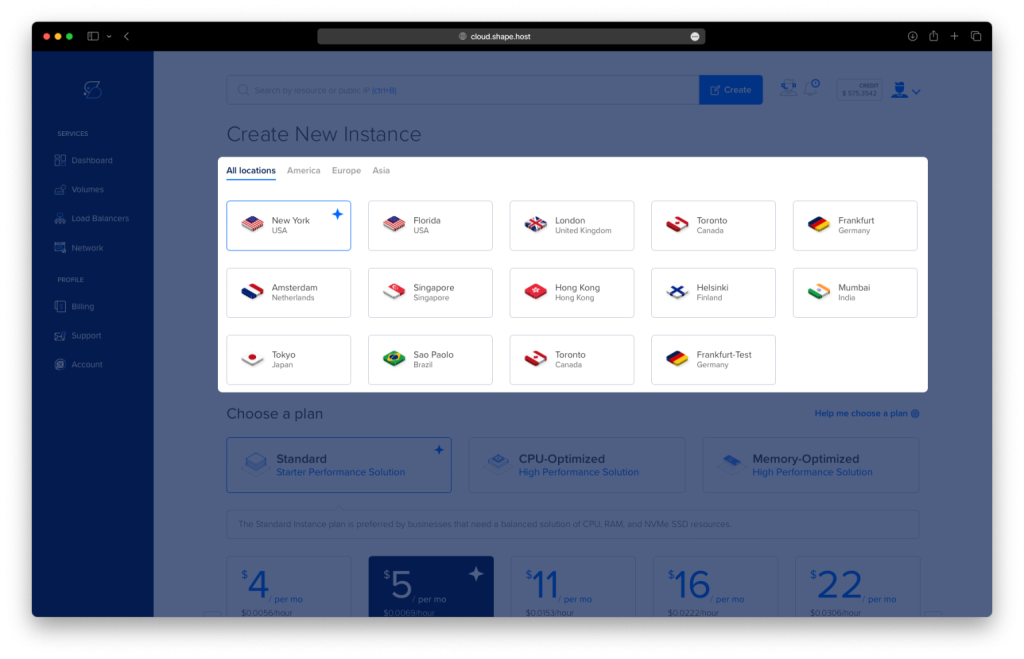
OS: Debian 12 (64-bit)
Plan: at least 2 CPUs, 2 GB RAM, 20 GB SSD
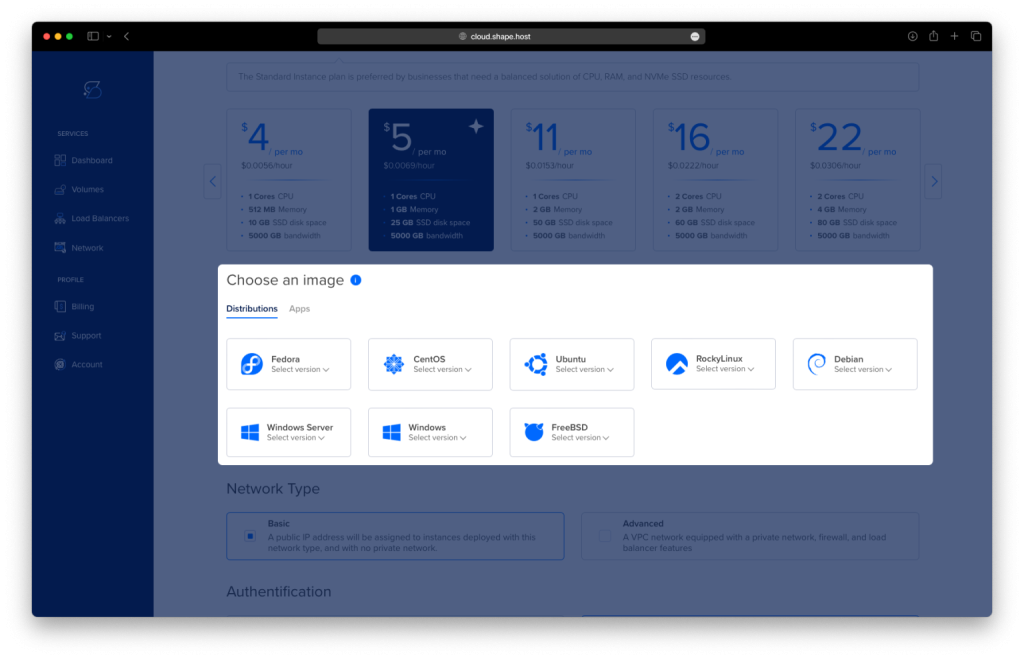
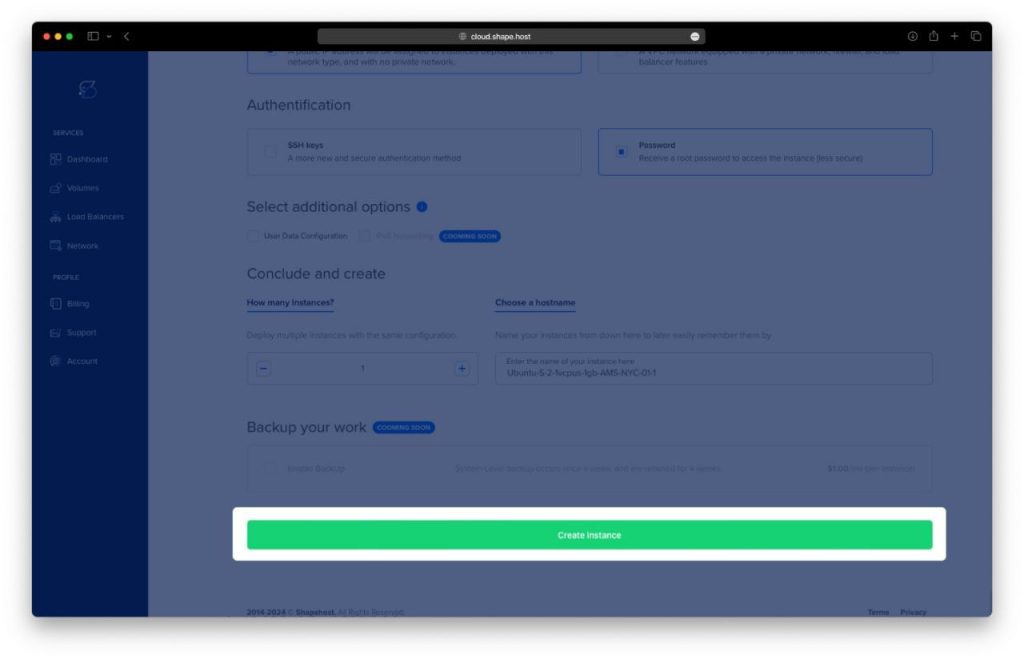
Click “Create Instance”.
After deployment, note your server’s IP address under Resources.
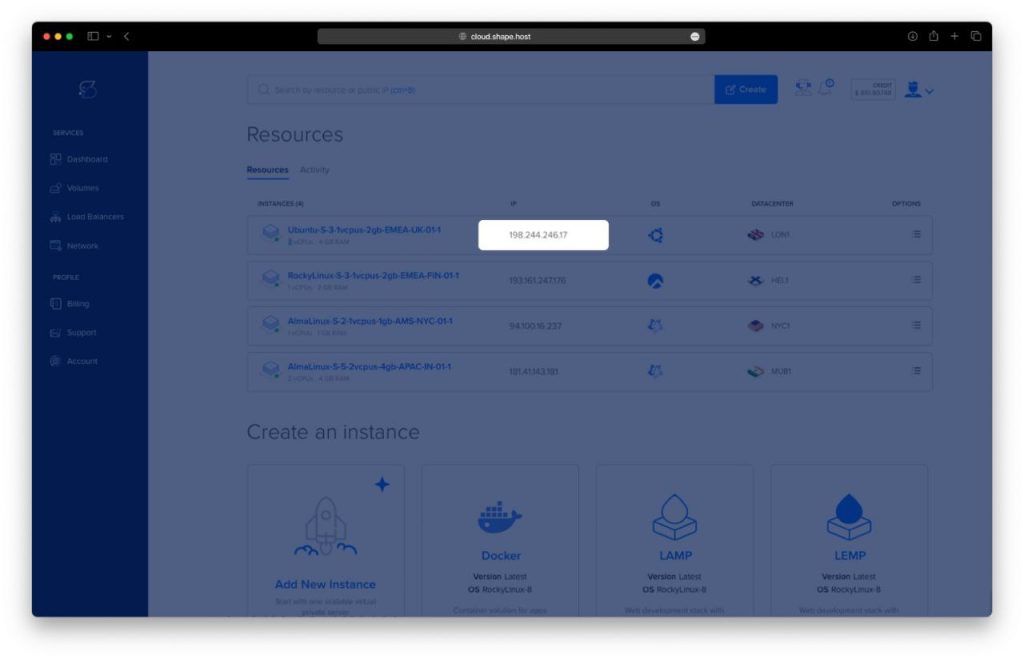
You’ll use this server to host your OpenLDAP environment.
Connect to Your Server via SSH
On Linux/macOS:
ssh root@your_server_ip
On Windows:
Use PuTTY, enter the IP, and connect as root.
🔹 Step 1: Update the System
apt update && apt upgrade -y
apt update: Refreshes the package index from repositories.apt upgrade -y: Automatically upgrades all installed packages to the latest version without prompting.
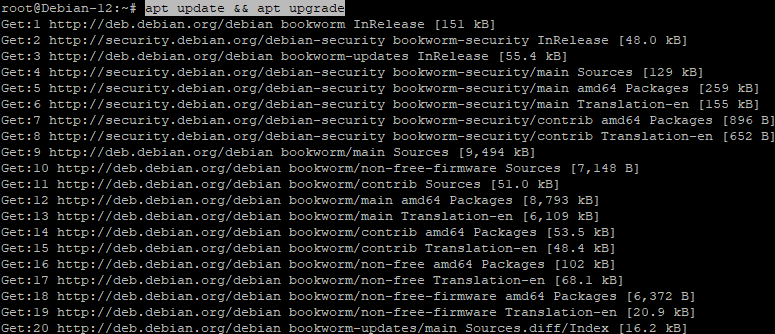
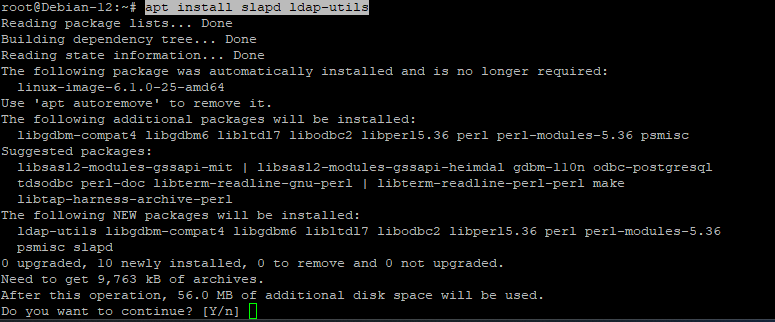
🔹 Step 2: Install OpenLDAP Server
apt install slapd ldap-utils -y
- Installs the OpenLDAP server (
slapd) and LDAP client utilities (ldap-utils) needed for querying and managing the directory.
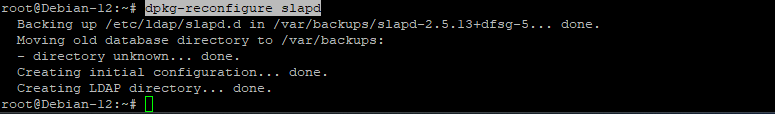
If not prompted during installation, reconfigure OpenLDAP manually:
dpkg-reconfigure slapd
This will open a guided setup. Choose:
- Domain name:
shape.host→ This will generate the DN root:dc=shape,dc=host. - Admin password: Set a secure password for the LDAP admin user (
cn=admin). - Backend type: Choose MDB (fast, modern database backend).
- Leave configuration intact (do not omit the configuration database).
🔹 Step 3: Verify LDAP Server
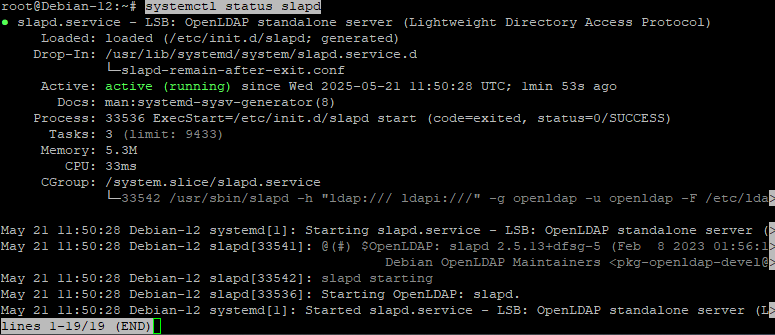
systemctl status slapd
- Checks if the OpenLDAP daemon (
slapd) is running properly.
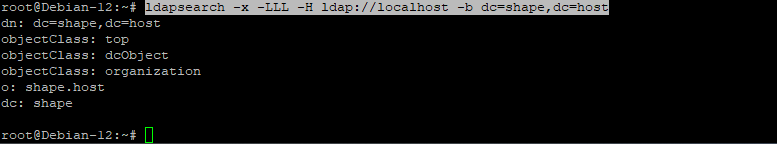
ldapsearch -x -LLL -H ldap://localhost -b dc=shape,dc=host
ldapsearch: CLI tool to query the LDAP directory.-x: Use simple authentication.-LLL: Format output without comments or version info.-H ldap://localhost: Connect to the local LDAP server.-b dc=shape,dc=host: Set the base DN for the search.
🔹 Step 4: Install phpLDAPadmin (Optional GUI)
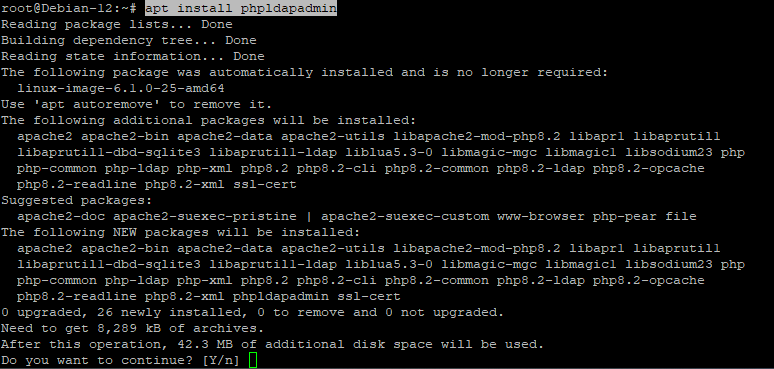
apt install phpldapadmin -y
- Installs a web-based GUI to manage LDAP easily via a browser.
Edit the phpLDAPadmin configuration:
nano /etc/phpldapadmin/config.php
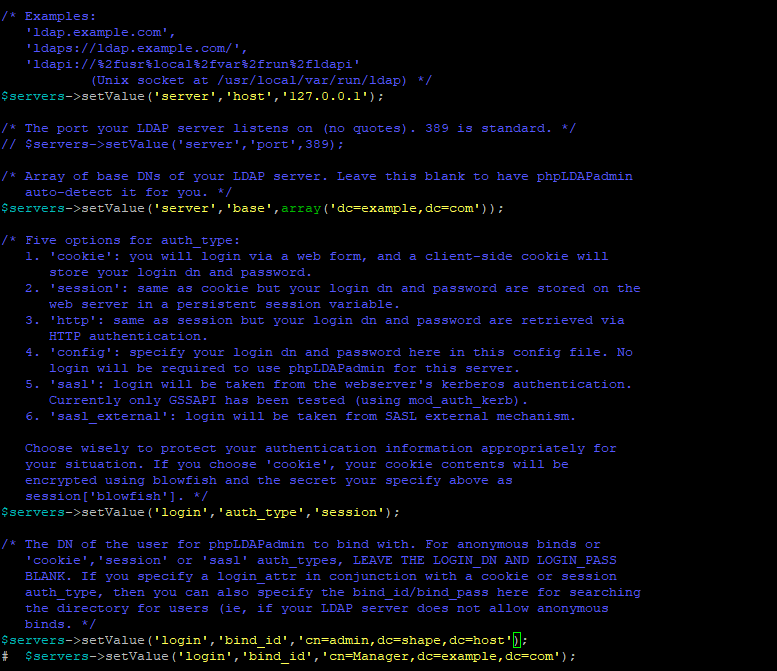
Update these lines to connect to your local LDAP server:
$servers->setValue('server','host','127.0.0.1');
$servers->setValue('login','bind_id','cn=admin,dc=shape,dc=host');
Edit Apache config to allow external access:
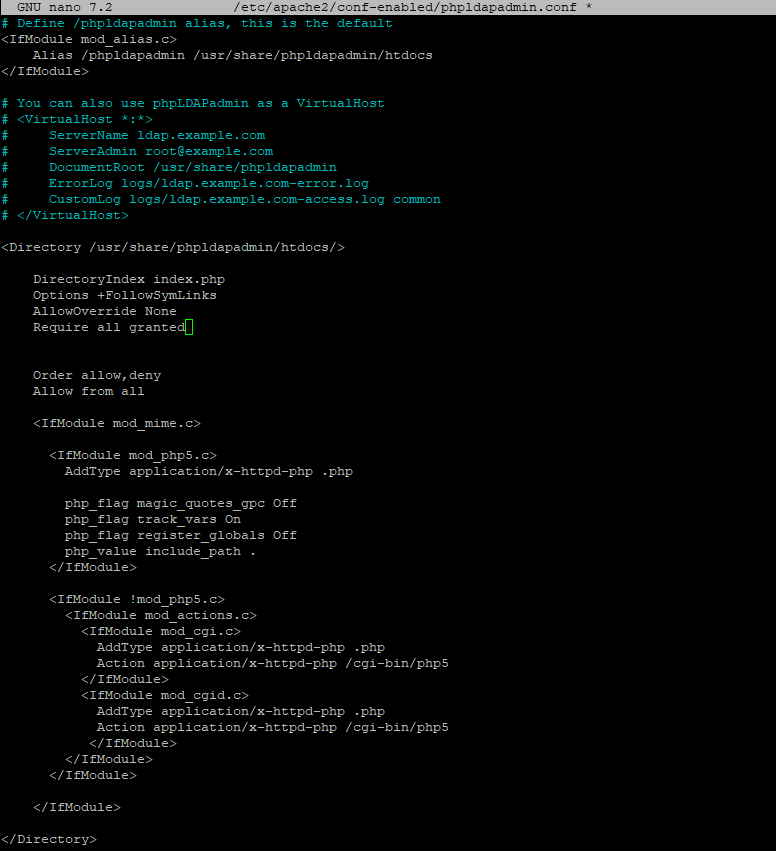
nano /etc/apache2/conf-enabled/phpldapadmin.conf
Find this line:
Require local
Change it to:
Require all granted
- This allows external web access to phpLDAPadmin via your IP or domain.
Restart Apache:
systemctl restart apache2
- Applies the new config and restarts the web server.

You can now access:
http://your-server-ip/phpldapadmin/
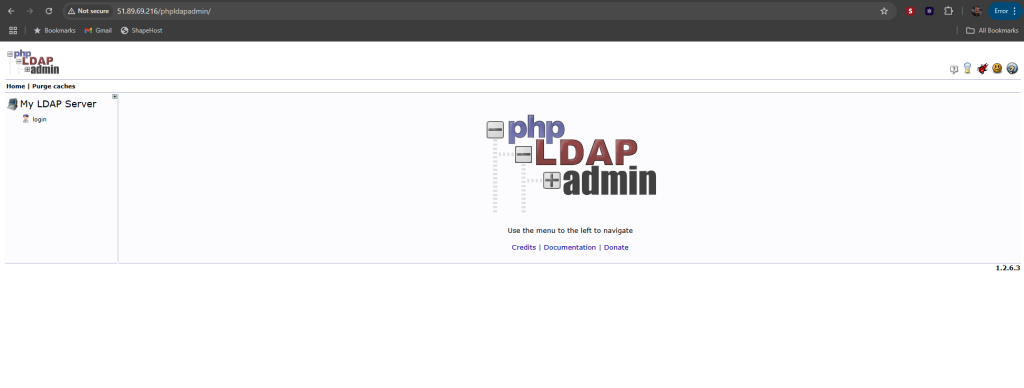
or via your domain:
http://debian-tutorials.shape.host/phpldapadmin/
🔹 Step 5: Create Base LDAP Structure
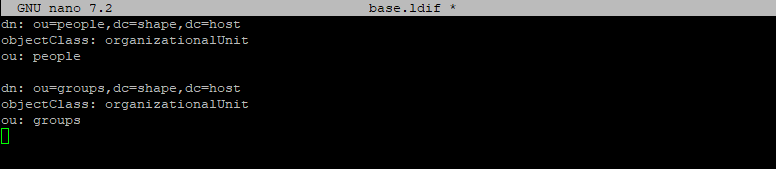
Create a base LDIF file:
nano base.ldif
Paste the following:
dn: ou=people,dc=shape,dc=host
objectClass: organizationalUnit
ou: people

dn: ou=groups,dc=shape,dc=host
objectClass: organizationalUnit
ou: groups
- This creates two organizational units (OUs):
peopleandgroups, useful for organizing users and roles.
Add it to LDAP:
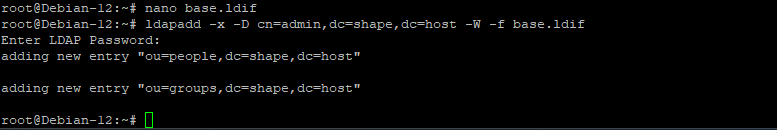
ldapadd -x -D cn=admin,dc=shape,dc=host -W -f base.ldif
-D: Specifies the bind DN (LDAP admin).-W: Prompts for the admin password.-f base.ldif: File containing entries to add.
🔹 Step 6: Add an LDAP User
Create the user entry:
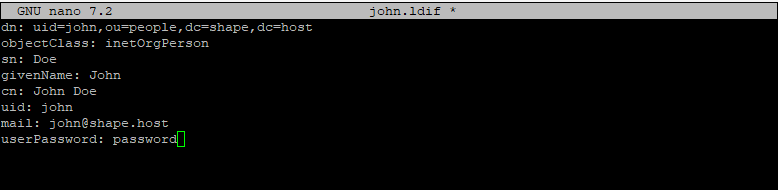
nano john.ldif
Add the following:
dn: uid=john,ou=people,dc=shape,dc=host
objectClass: inetOrgPerson
sn: Doe
givenName: John
cn: John Doe
uid: john
mail: john@shape.host
userPassword: password
This adds a user named John Doe with email and password.
Add the user to LDAP:
ldapadd -x -D cn=admin,dc=shape,dc=host -W -f john.ldif
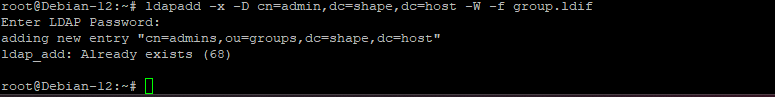
- Same syntax as before, using the new file.
🔐 Tip: Hash the password before using it:
slappasswd
- Enter a password and copy the hashed output into the
userPassword:field.
🔹 Step 7: Enable HTTPS (SSL) with Let’s Encrypt
Install Certbot:
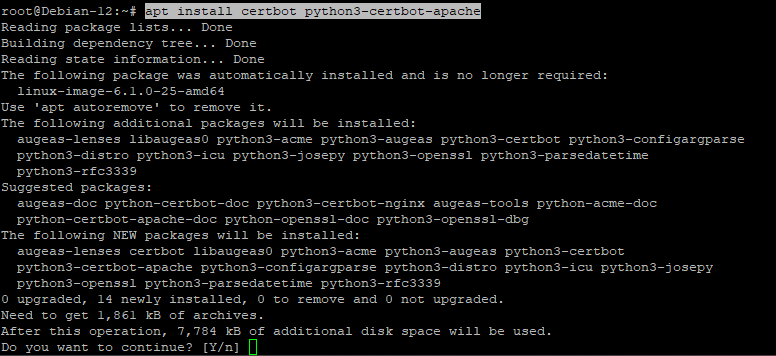
apt install certbot python3-certbot-apache -y
Installs the Let’s Encrypt client (certbot) and the Apache plugin.
Obtain SSL certificate:
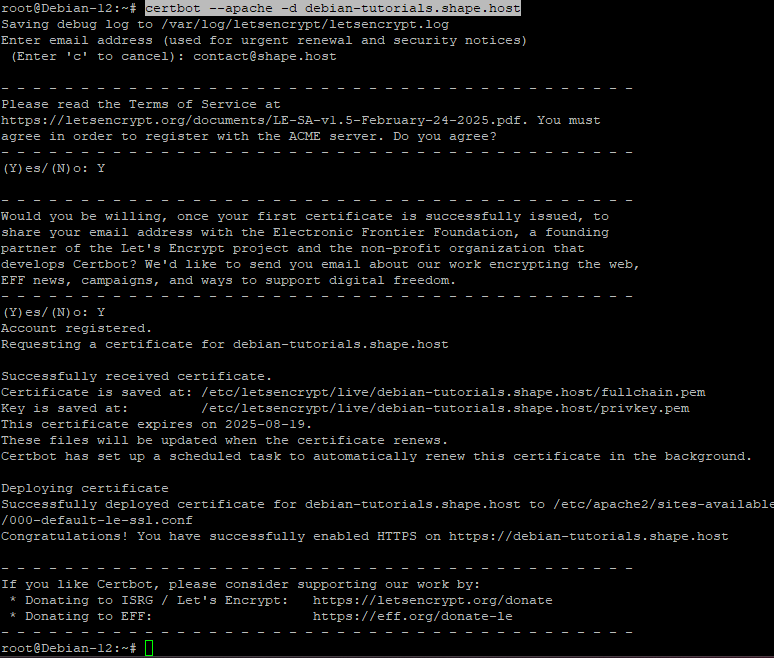
certbot --apache -d debian-tutorials.shape.host
- Requests and installs a free SSL cert for your domain.
- Choose the redirect option to force HTTPS.
Final Access Points
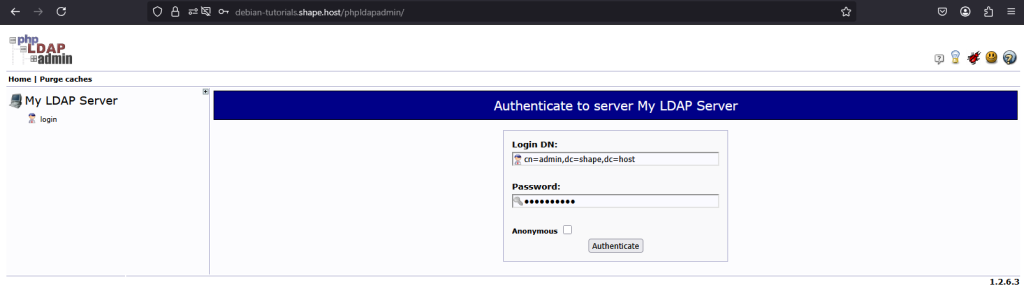
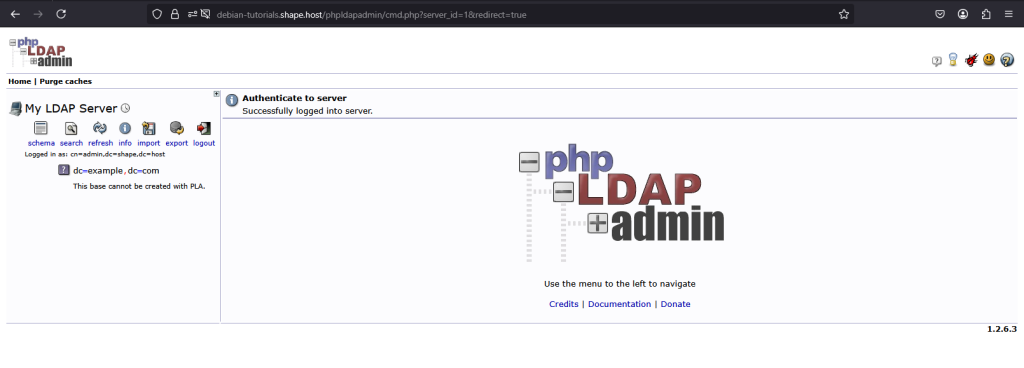
phpLDAPadmin (Web GUI):
https://debian-tutorials.shape.host/phpldapadmin/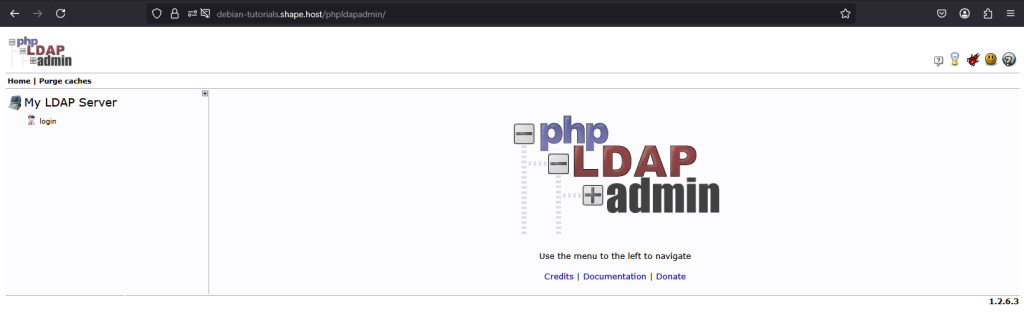
Test LDAP connection:
ldapsearch -x -LLL -H ldap://localhost -b dc=shape,dc=host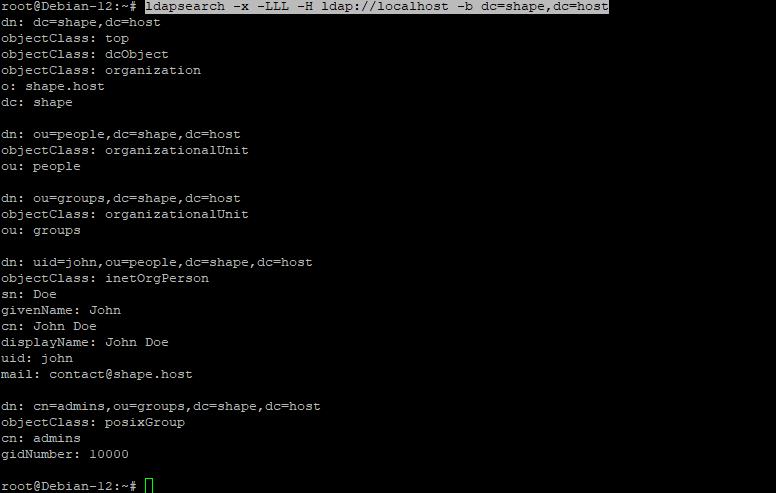
Need dependable hosting?
Choose Shape.Host Linux SSD VPS for:
- Ultra-fast SSD performance
- Global data centers
- Instant setup with full root access
- Ready-to-go support for Debian 12, Ubuntu, CentOS & more
Start building secure directory infrastructure on Shape.Host today!