What is OpenLDAP?
OpenLDAP is a free and open-source implementation of the Lightweight Directory Access Protocol (LDAP). It provides a centralized directory service for storing user accounts, passwords, group information, and other directory-based data in a hierarchical and searchable format.
OpenLDAP is commonly used for:
- Centralized user authentication
- Address book services
- Access control and identity management
- Integration with Samba, Apache, Dovecot, sudo, and other Linux/UNIX services
Why Use OpenLDAP on Ubuntu 24.04?
Ubuntu 24.04 LTS is a modern, secure, and long-term supported platform. It provides a stable environment for directory services like OpenLDAP due to:
- Support for OpenLDAP 2.5+ via APT
- Updated systemd, AppArmor, and TLS 1.3 integration
- Enhanced performance, logging, and IPv6 readiness
- Compatibility with SSSD, Kerberos, and Samba for centralized authentication
Ubuntu’s LTS support until 2029 makes it ideal for enterprise-grade directory deployments.
Key Components of an OpenLDAP Setup
- slapd – The LDAP directory server daemon
- ldap-utils – Command-line tools to interact with the directory
- LDIF (LDAP Data Interchange Format) – Text files used to represent directory entries
- Schemas – Define object types, attributes, and relationships (e.g., inetOrgPerson)
- Access Control Lists (ACLs) – Fine-grained permission rules for reading or modifying data
- TLS – Secure LDAP communications with certificates (LDAPS)
Common Use Cases
- Manage Linux server logins with centralized LDAP user accounts
- Control access to internal applications (e.g., GitLab, Nextcloud, Zabbix)
- Serve as a backend directory for mail servers or web-based address books
- Provide identity backend for Samba/Active Directory compatibility
- Store and query hierarchical organizational data (users, departments, etc.)
Advantages of OpenLDAP
| Feature | Description |
|---|---|
| Scalable | Supports thousands of entries and replicas |
| Flexible Schema | Supports custom attribute types and object classes |
| Interoperable | Integrates with UNIX, Windows, macOS, and cloud services |
| Secure | TLS, SASL, strong ACLs, and integration with PAM |
| CLI and GUI Options | Manage via CLI (ldapadd, ldapsearch) or GUIs like phpLDAPadmin or LDAP Account Manager (LAM) |
Security Features
- TLS encryption with X.509 certificates (for
ldaps://or StartTLS) - Strong password hashing (SSHA, BCRYPT)
- Fine-grained ACLs to control read/write access
- Integration with Kerberos or SASL for single sign-on (SSO)
- Ability to restrict anonymous binds or specific operations
Tools and Interfaces
- ldapsearch / ldapadd / ldapmodify / ldapdelete – Powerful command-line utilities
- phpLDAPadmin – Web-based admin UI (optional)
- LDAP Account Manager (LAM) – Feature-rich web interface for user/group management
- SSSD – For LDAP-based login integration on Linux clients
Deployment Notes on Ubuntu 24.04
- By default,
slapduses dynamic configuration under/etc/ldap/slapd.d - The traditional
slapd.confis deprecated - Ubuntu 24.04 supports systemd services, AppArmor, and automatic TLS provisioning
- Configuration can be done interactively during install or manually via
dpkg-reconfigure slapd
Typical Directory Structure
A default domain of example.com creates a base DN like:
dc=example,dc=com
Under which you’ll define entries such as:
ou=People– user entriesou=Groups– group entriescn=admin– admin (bind) useruid=john.doe– individual user account
OpenLDAP on Ubuntu 24.04 offers a stable, secure, and fully-featured solution for directory-based identity and access management. Whether you’re deploying a centralized login system or integrating enterprise apps with LDAP authentication, Ubuntu 24.04 provides a modern, well-supported platform for OpenLDAP services.
Its compatibility with modern security protocols, web admin interfaces, and Linux integration tools makes it a powerful choice for organizations of all sizes.
🔹Create a Server Instance on Shape.Host
Before installation, provision a clean Ubuntu 24.04 VPS:
Go to https://shape.host and log in.
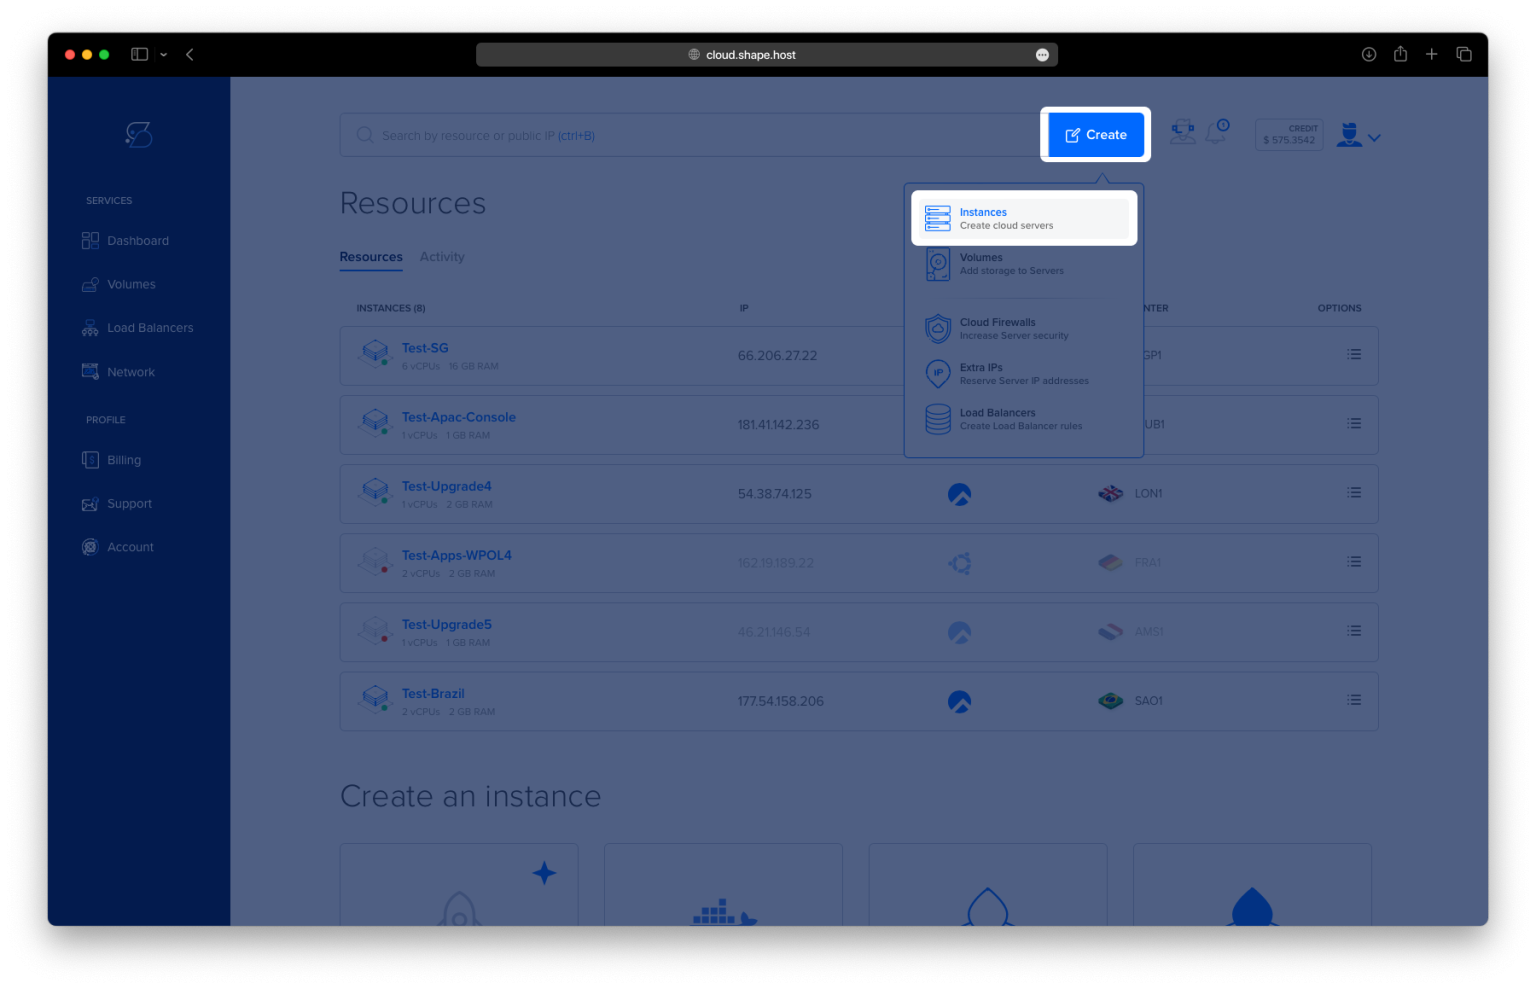
Click “Create”, then choose “Instance”.

Set:
Location: your preferred region.

OS: Ubuntu 24.04 (64-bit)
Plan: at least 2 CPUs, 2 GB RAM, 20 GB SSD

Click “Create Instance”.

After deployment, note your server’s IP address under Resources.

You’ll use this server to host your OpenLDAP environment.
Connect to Your Server via SSH
On Linux/macOS:
ssh root@your_server_ip
On Windows:
Use PuTTY, enter the IP, and connect as root.
🔹 Step 1: Update the System
apt update && apt upgrade -y

🔹 Step 2: Install OpenLDAP Server
apt install slapd ldap-utils -y

If not prompted, reconfigure manually:
dpkg-reconfigure slapd
During reconfiguration, choose:
- Omit OpenLDAP server configuration? →
No - DNS domain name: example.com → results in
dc=example,dc=com - Organization name: Example Inc
- Admin password: (choose securely)
- Database backend: MDB
- Do you want the database to be removed when slapd is purged? →
No - Move old database? →
Yes

🔹 Step 3: Verify LDAP Server
systemctl status slapd

Test:
ldapsearch -x -LLL -H ldap://localhost -b dc=shape,dc=host

🔹 Step 4: Install phpLDAPadmin (Optional GUI)
apt install phpldapadmin -y

Edit config:
nano /etc/phpldapadmin/config.php
Update these lines:
$servers->setValue('server','host','127.0.0.1');
$servers->setValue('login','bind_id','cn=admin,dc=shape,dc=host');

Edit Apache config:
nano /etc/apache2/conf-enabled/phpldapadmin.conf
Change:
Require local
To:
Require all granted

Restart Apache:
systemctl restart apache2
Now open:
http://51.89.69.203/phpldapadmin/

or (after DNS propagation):
http://ubuntu-tutorials.shape.host/phpldapadmin/
🔹 Step 5: Create Base LDAP Structure
Create file:
nano base.ldif
dn: ou=people,dc=shape,dc=host
objectClass: organizationalUnit
ou: people

dn: ou=groups,dc=shape,dc=host
objectClass: organizationalUnit
ou: groups

Apply:
ldapadd -x -D cn=admin,dc=shape,dc=host -W -f base.ldif

🔹 Step 6: Add an LDAP User
nano john.ldif
dn: uid=john,ou=people,dc=shape,dc=host
objectClass: inetOrgPerson
sn: Doe
givenName: John
cn: John Doe
uid: john
mail: john@shape.host
userPassword: password

Then:
ldapadd -x -D cn=admin,dc=shape,dc=host -W -f john.ldif

🔐 You can hash the password using:
slappasswd
🔹 Step 7: Enable HTTPS (SSL) with Let’s Encrypt
Install Certbot:
apt install certbot python3-certbot-apache -y

Obtain SSL cert:
certbot --apache -d ubuntu-tutorials.shape.host
Choose redirect to force HTTPS access.

Final Access Points
phpLDAPadmin (Web GUI):
https://ubuntu-tutorials.shape.host/phpldapadmin/
Test LDAP:
ldapsearch -x -LLL -H ldap://localhost -b dc=shape,dc=host
This OpenLDAP setup runs best on fast, secure, and scalable cloud infrastructure.
Need reliable hosting?
Choose Shape.Host Cloud VPS for:
- Enterprise-grade performance
- SSD storage and high-availability locations
- Full root access for maximum control
- Instant deployment with Ubuntu 24.04 support