What is DenyHosts?
DenyHosts is an open-source security tool for Unix-like systems designed to prevent brute-force SSH attacks by monitoring authentication logs and blocking IP addresses that show suspicious login activity.
On Ubuntu 24.04 (Noble Numbat), DenyHosts is still a relevant and lightweight option to protect SSH access on servers by automatically updating the /etc/hosts.deny file with malicious IP addresses.
Key Features of DenyHosts
SSH Protection
- Monitors
/var/log/auth.logfor failed SSH login attempts. - Detects and blocks repeated failed login attempts from the same IP.
Hosts Deny Integration
- Adds offending IP addresses to the system’s
/etc/hosts.denyfile. - Prevents further access to SSH from those IPs using TCP Wrappers.
onfigurable Thresholds
- Set limits on:
- Number of failed login attempts.
- Time intervals before banning.
- Whitelist trusted IPs.
- Synchronization with global DenyHosts server (optional).
Email Alerts
- Sends email notifications about blocked hosts and suspicious activity.
Auto-Sync and Updates
- Optionally sync with a shared blacklist from other DenyHosts installations.
Why Use DenyHosts on Ubuntu 24.04?
Ubuntu 24.04 includes modern security tools like UFW, Fail2Ban, and AppArmor, but DenyHosts remains a lightweight and effective solution for systems where:
- Minimal resource usage is critical.
- You need a simple setup with clear log-based banning.
- You prefer host-based blocking via TCP Wrappers.
It is especially useful on headless servers or VPSes exposed to the internet with SSH enabled.
How DenyHosts Works
- Monitors
/var/log/auth.login real time. - Detects multiple failed SSH login attempts from an IP.
- Adds the IP to
/etc/hosts.denyto block further connections. - Optionally, logs and reports the activity.
- Periodically checks for new suspicious activity.
DenyHosts vs Similar Tools
| Feature | DenyHosts | Fail2Ban | SSHGuard |
|---|---|---|---|
| SSH protection | ✅ Yes | ✅ Yes | ✅ Yes |
| Configurable bans | ✅ Yes | ✅ Yes | ✅ Yes |
| Protocol support | ❌ SSH only | ✅ Multi-service | ⚠️ SSH & syslog-based |
| Uses TCP Wrappers | ✅ Yes | ❌ No | ❌ No |
| IPTables/firewall integration | ❌ No | ✅ Yes | ✅ Yes |
| Email alerts | ✅ Yes | ✅ Yes | ⚠️ Limited |
| Resource usage | ✅ Low | ⚠️ Medium | ✅ Low |
| Ease of setup | ✅ Easy | ⚠️ Moderate | ✅ Easy |
Advantages of DenyHosts on Ubuntu 24.04
✅ Very lightweight and simple to configure
✅ Effective at blocking brute-force SSH attempts
✅ Email alerts keep you informed of suspicious activity
✅ Doesn’t require additional firewall setup
✅ Easily integrates into minimal or legacy systems
Limitations
❌ Only protects SSH (not other services like FTP, web apps, etc.)
❌ Uses TCP Wrappers, which are considered deprecated in some environments
❌ Doesn’t integrate directly with iptables or nftables
❌ Fewer customization options compared to Fail2Ban
❌ Less suited for systems with dynamic IPs or NAT environments
Best Use Cases
- VPS or cloud servers running OpenSSH on default ports
- Lightweight Linux installations needing basic brute-force protection
- Developers and sysadmins who want quick SSH hardening
- Secure environments where advanced firewalls are not required
DenyHosts on Ubuntu 24.04 is a straightforward and reliable security solution to protect SSH access from brute-force attacks. While more advanced tools like Fail2Ban exist, DenyHosts excels in simplicity, minimalism, and low overhead, making it ideal for lightweight servers and legacy systems.
If your primary concern is protecting SSH with minimal setup, DenyHosts is a solid tool that continues to serve well—even in modern Linux environments like Ubuntu 24.04.
Step 1: Launch an Ubuntu 24.04 Server on Shape.Host
Before we begin the installation, you’ll need a running VPS with Ubuntu 24.04. Here’s how to create one using Shape.Host:
Log in to your Shape.Host account.
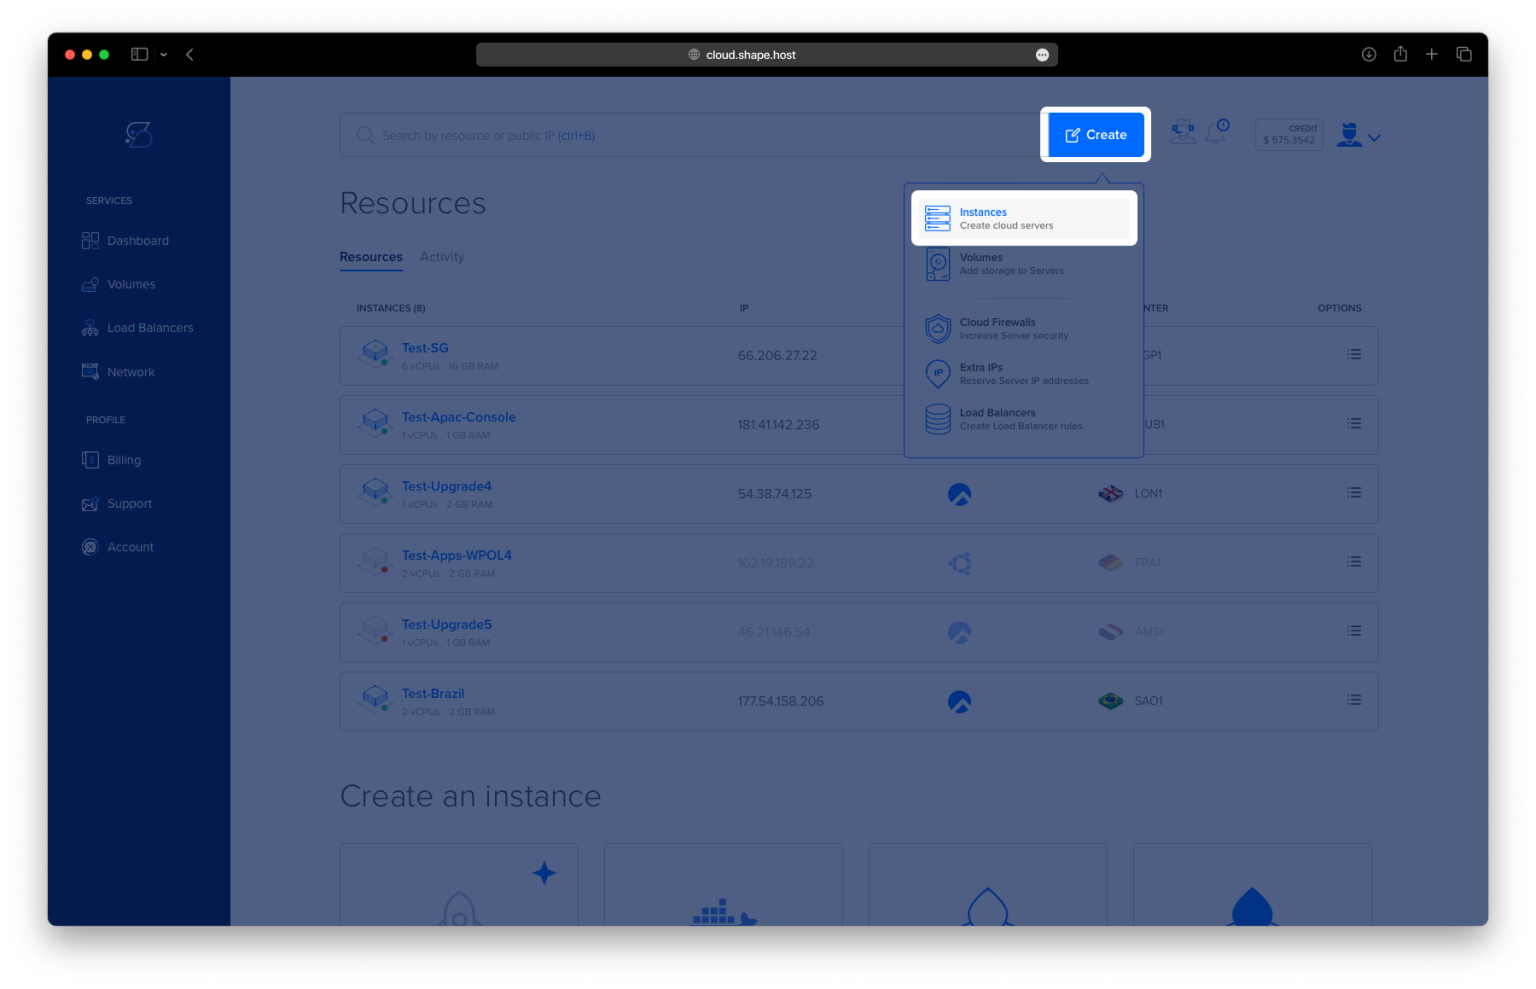
Click “Create”.
Select Instance and choose Ubuntu 24.04 as the operating system.
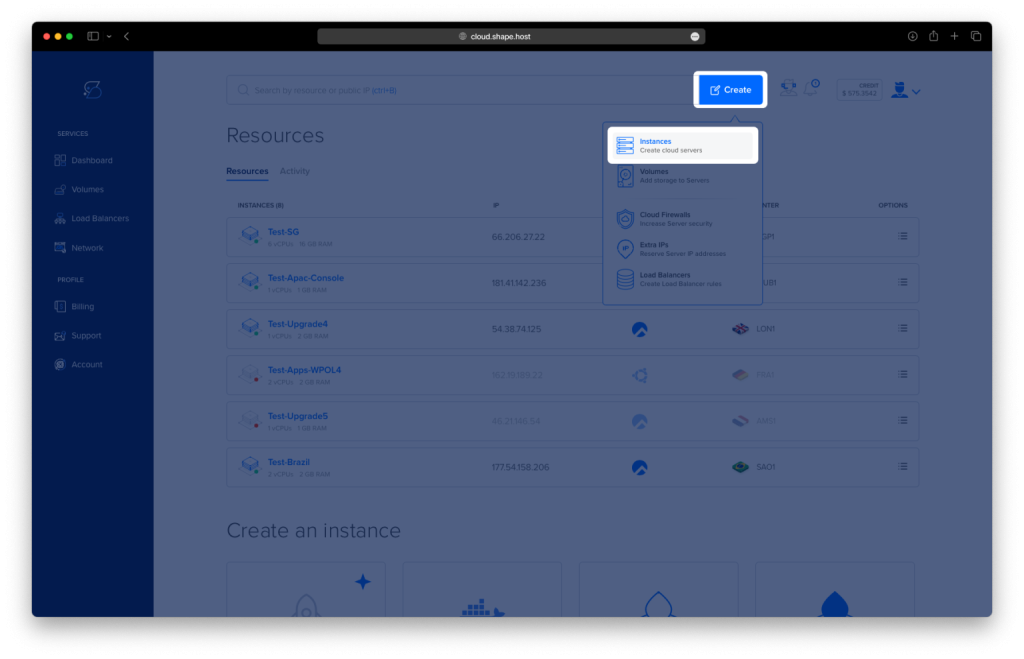
Choose your preferred server location.
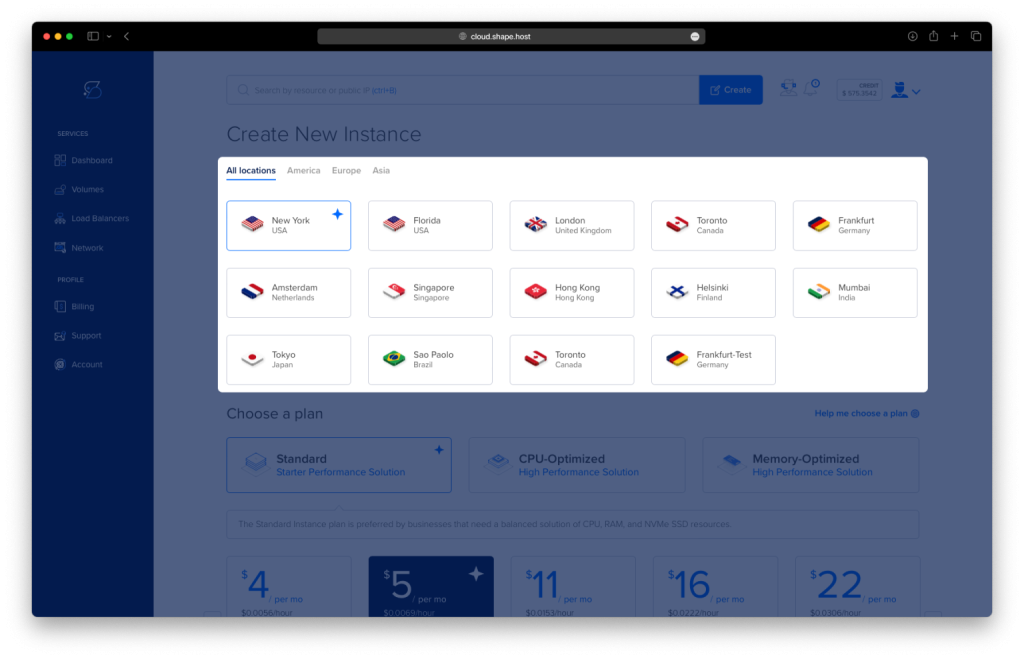
Pick a plan with at least 1 GB RAM and 10 GB storage.
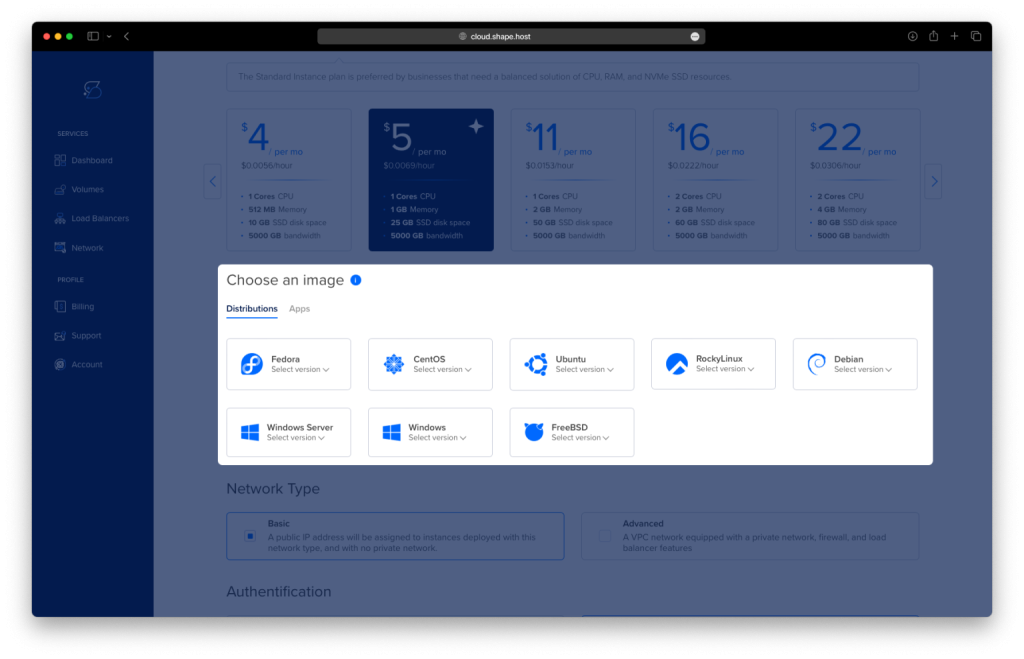
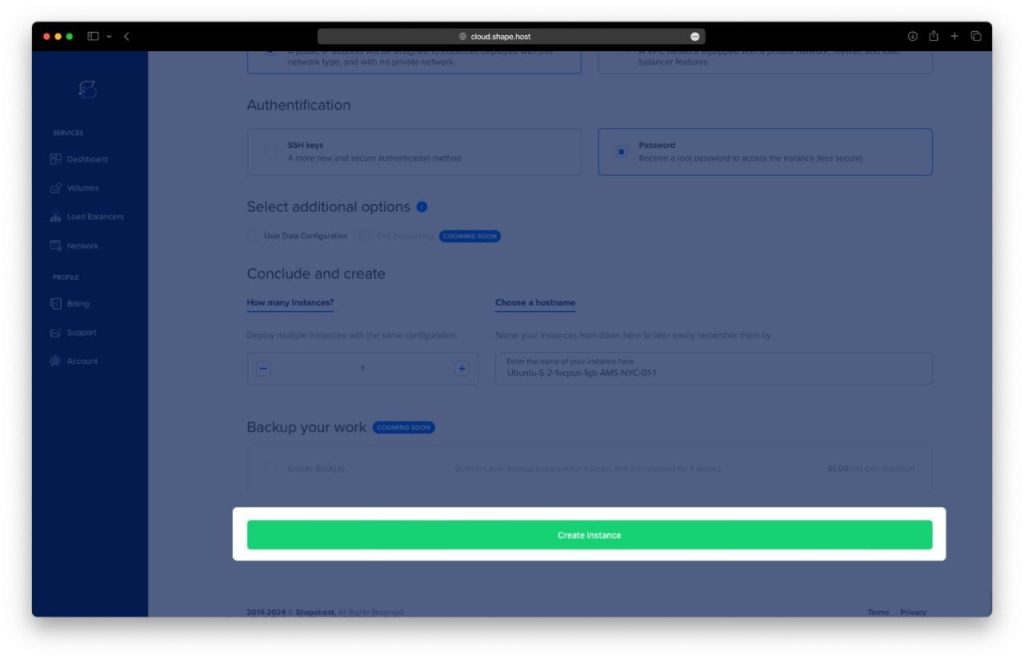
Launch the Instance by selecting either SSH keys or a password for authentication. Click Create Instance to complete the process.
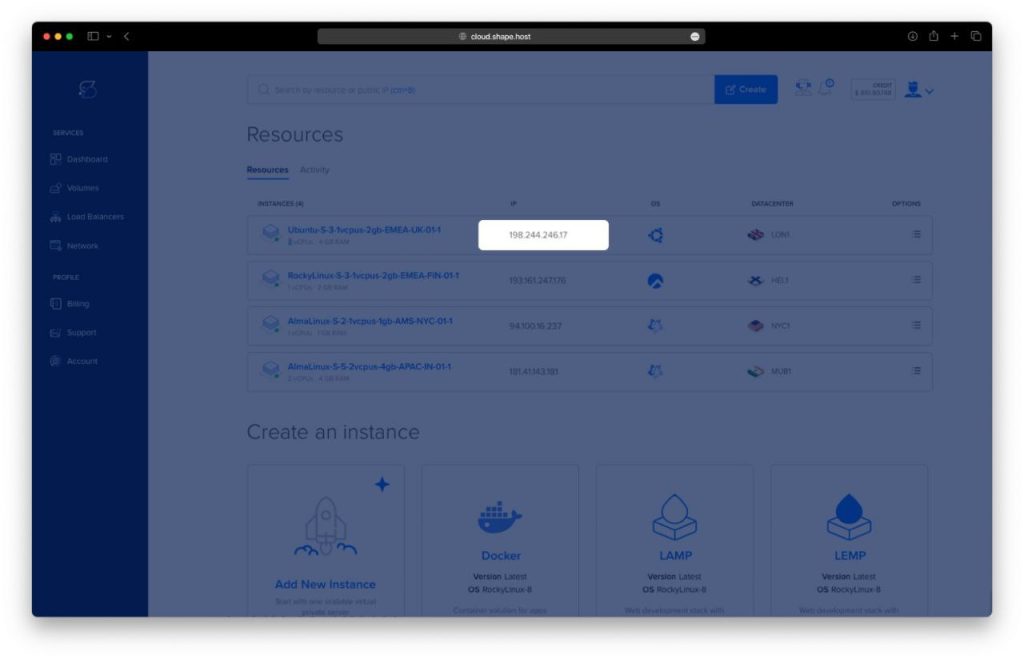
Find your instance’s IP address under the Resources section and use it to access your server.
Step 2: Connect to Your Server
Use SSH to log in to your newly created server.
From Linux/macOS:
ssh root@your_server_ip
From Windows:
Use PuTTY and connect with the server’s IP address and root credentials.
Step 3: Download DenyHosts
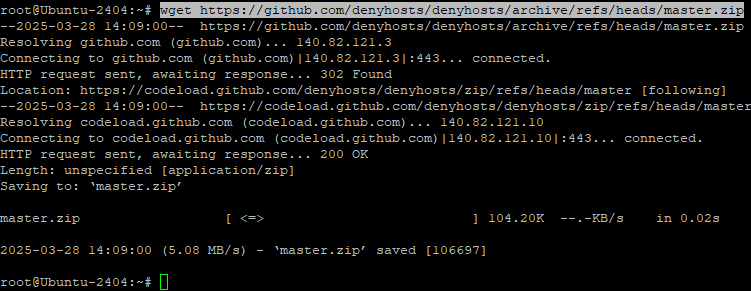
DenyHosts is available on GitHub. We’ll download the latest version manually:
wget https://github.com/denyhosts/denyhosts/archive/refs/heads/master.zip
Step 4: Install Required Packages
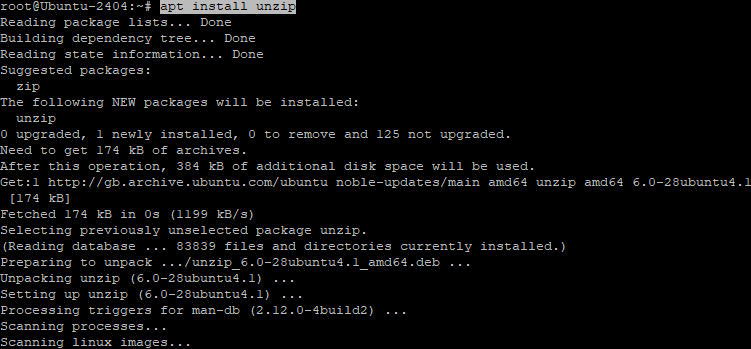
Before installing DenyHosts, make sure the necessary tools are available:
apt install unzip
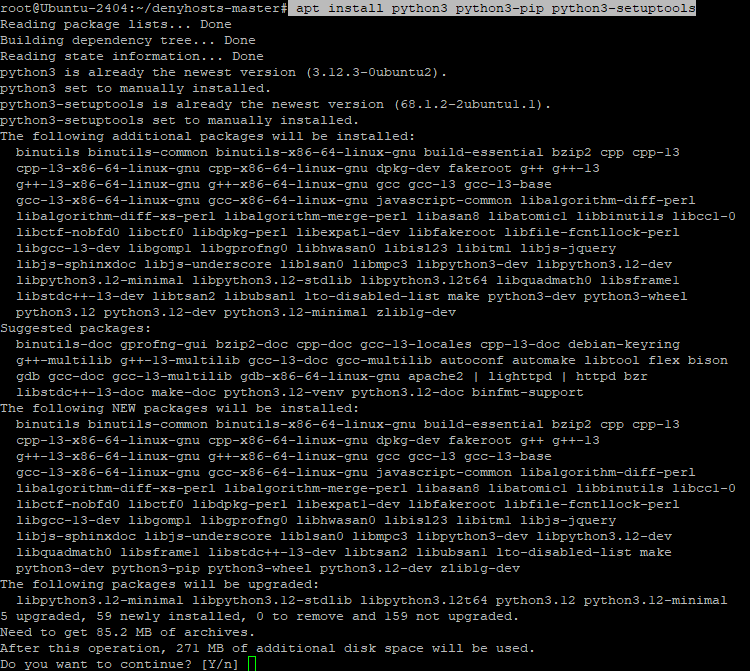
apt install python3 python3-pip python3-setuptools
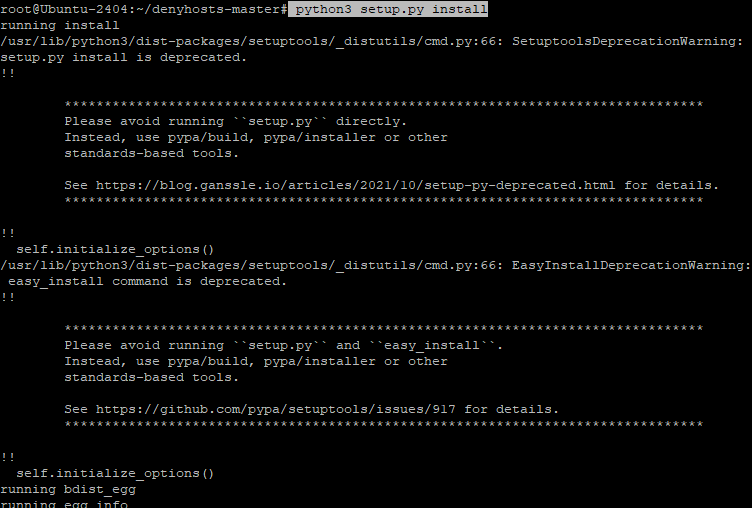
python3 setup.py install
Step 5: Unzip and Install DenyHosts
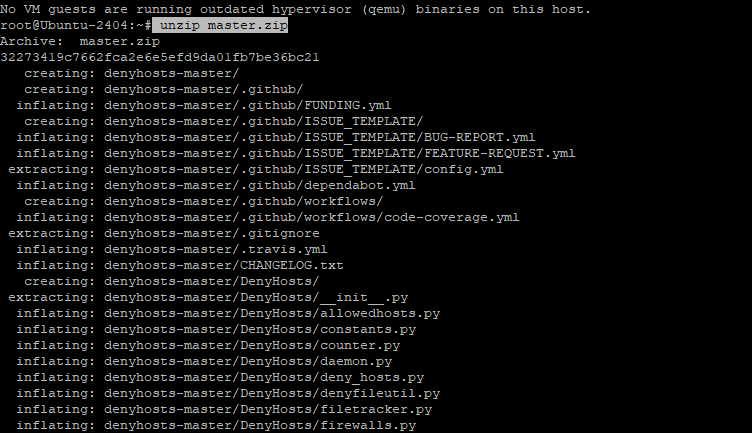
Extract the downloaded archive and run the installation:
unzip master.zip
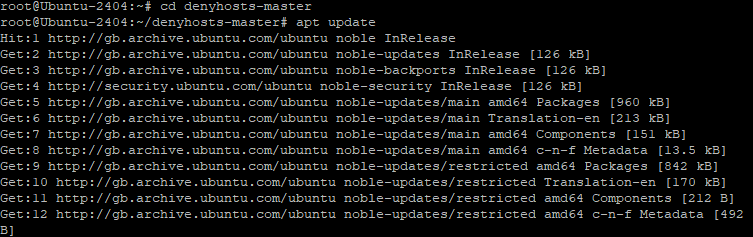
cd denyhosts-master
apt update
DenyHosts is now installed on your server.
Step 6: Configure DenyHosts
Open the main configuration file:
nano /etc/denyhosts.conf
Here are key settings to adjust:
- BLOCK_SERVICE
This defines the service to monitor. For SSH, use:BLOCK_SERVICE = sshd - HOSTS_DENY
This file will store the blocked IPs:HOSTS_DENY = /etc/hosts.deny - ADMIN_EMAIL
Email address where you’ll receive notifications about blocked IPs:ADMIN_EMAIL = your_email@example.com - DENY_THRESHOLD_INVALID
The number of failed login attempts allowed before blocking:DENY_THRESHOLD_INVALID = 5
Save and exit the file after editing.
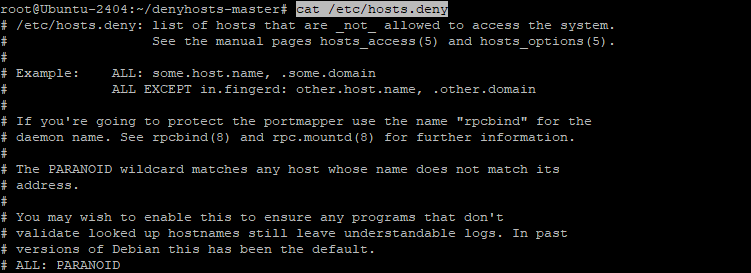
Step 7: Review the Blocked IPs
To see which IPs have been blocked so far:
cat /etc/hosts.deny
Step 8: Allowlist Trusted IPs
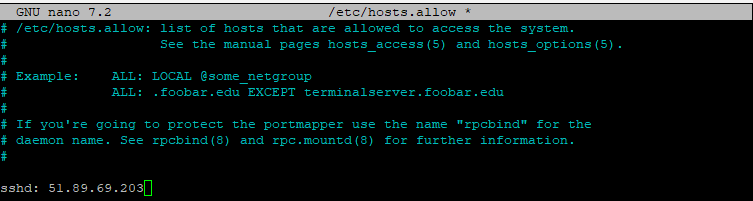
To ensure your own IP is never blocked, add it to the hosts.allow file:
nano /etc/hosts.allow
Add this line, replacing IP_address with your actual trusted IP:
sshd: IP_address
This tells DenyHosts to always allow SSH from that IP.
Need secure and high-performance VPS hosting?
Choose Shape.Host for fast deployment, flexible plans, and full root access — ideal for running Linux tools like DenyHosts.